Don’t wait for the breach
to read the signal.
Your controls are drifting right now, and most platforms won’t tell you until something breaks. Draxis pulls Key Risk Indicators from the tools you already run, trends them every day, and warns you when the drift starts to match a pattern that preceded a failure. Then it puts a dollar figure on the exposure.
Read-only API access to EDR, SIEM, CSPM, identity, and vuln scanners. No agents to deploy.
Explainer film · 1:04 · sound on
What is Draxis.ai?
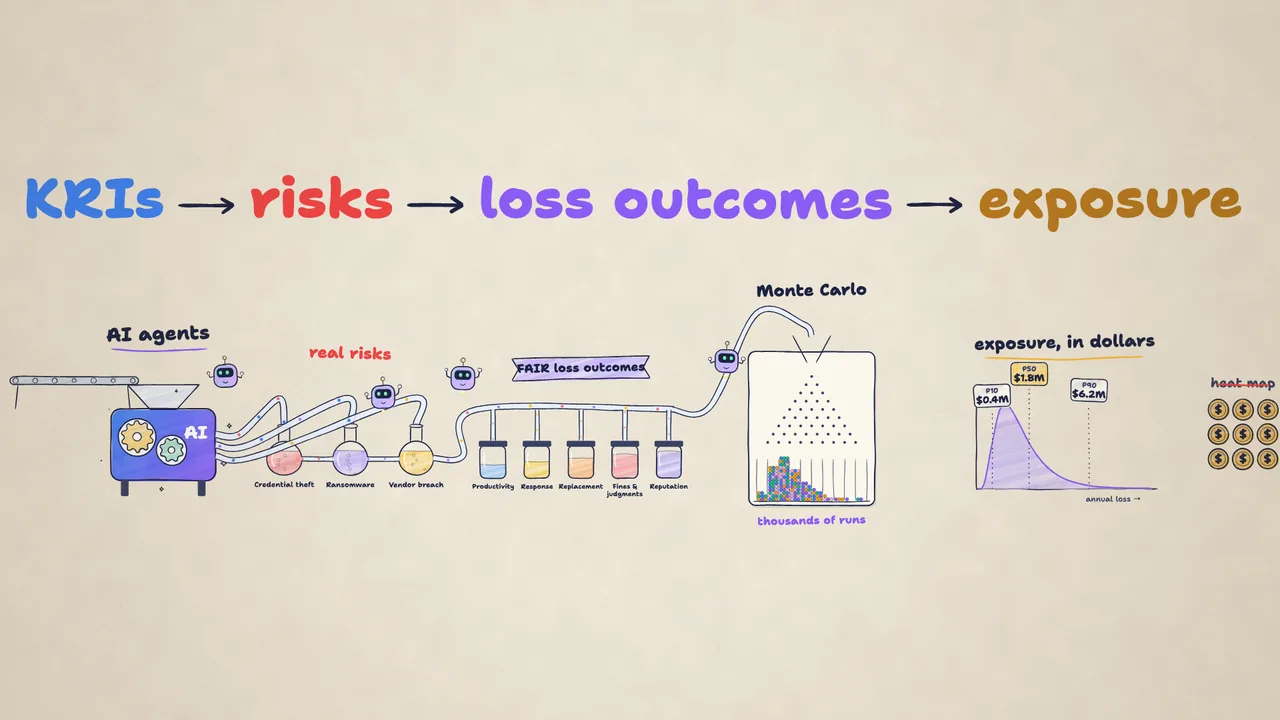
Draxis reads Key Risk Indicators from the tools you already run, trends every one daily, and warns you when your drift starts to look like the lead-up to a past incident. The film shows the whole loop in a minute.
Read the transcript
Your security stack never stops talking.
Twenty consoles, each working in isolation, and the story of your real risk is buried in between.
Draxis brings them all together, like a central nervous system for your entire security posture, reading Key Risk Indicators from the tools you already run.
Then it trends every one, every day. Not just where you stand, but which way you’re drifting.
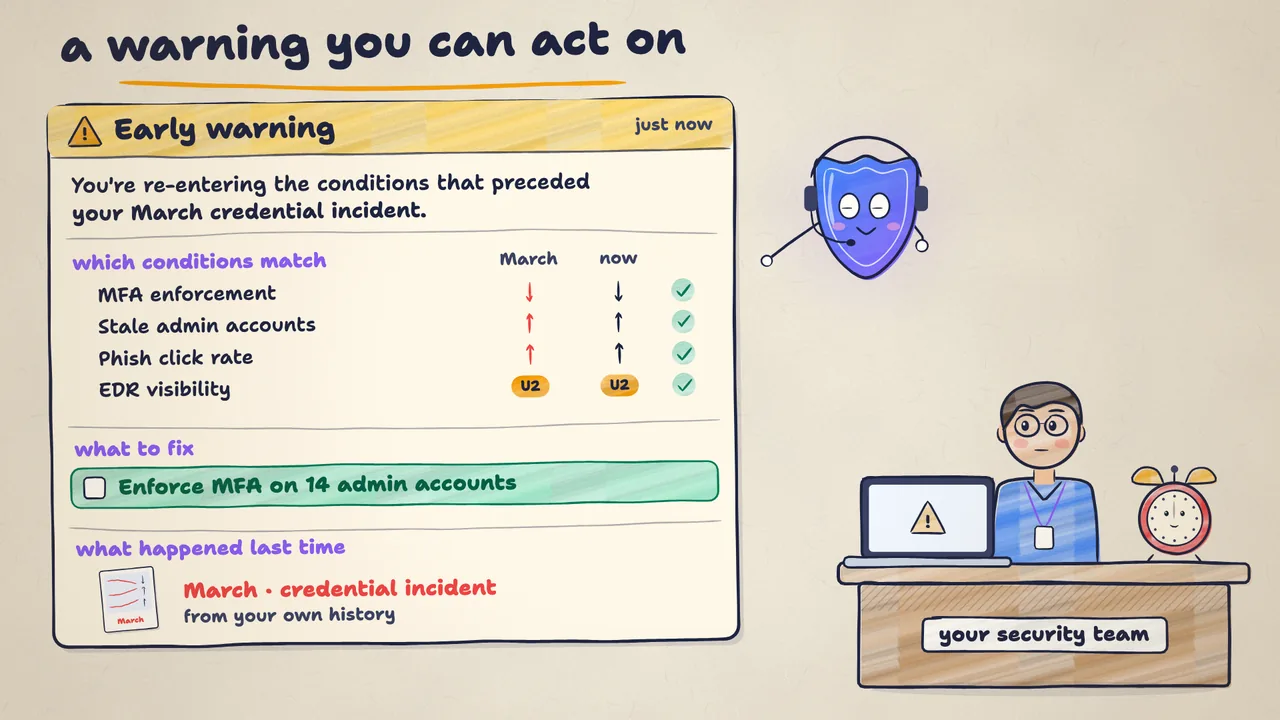
When your drift starts to match the trends that preceded your past incidents, Draxis warns you early, and shows you why.
But what good is real-time intelligence if the business can’t understand it?
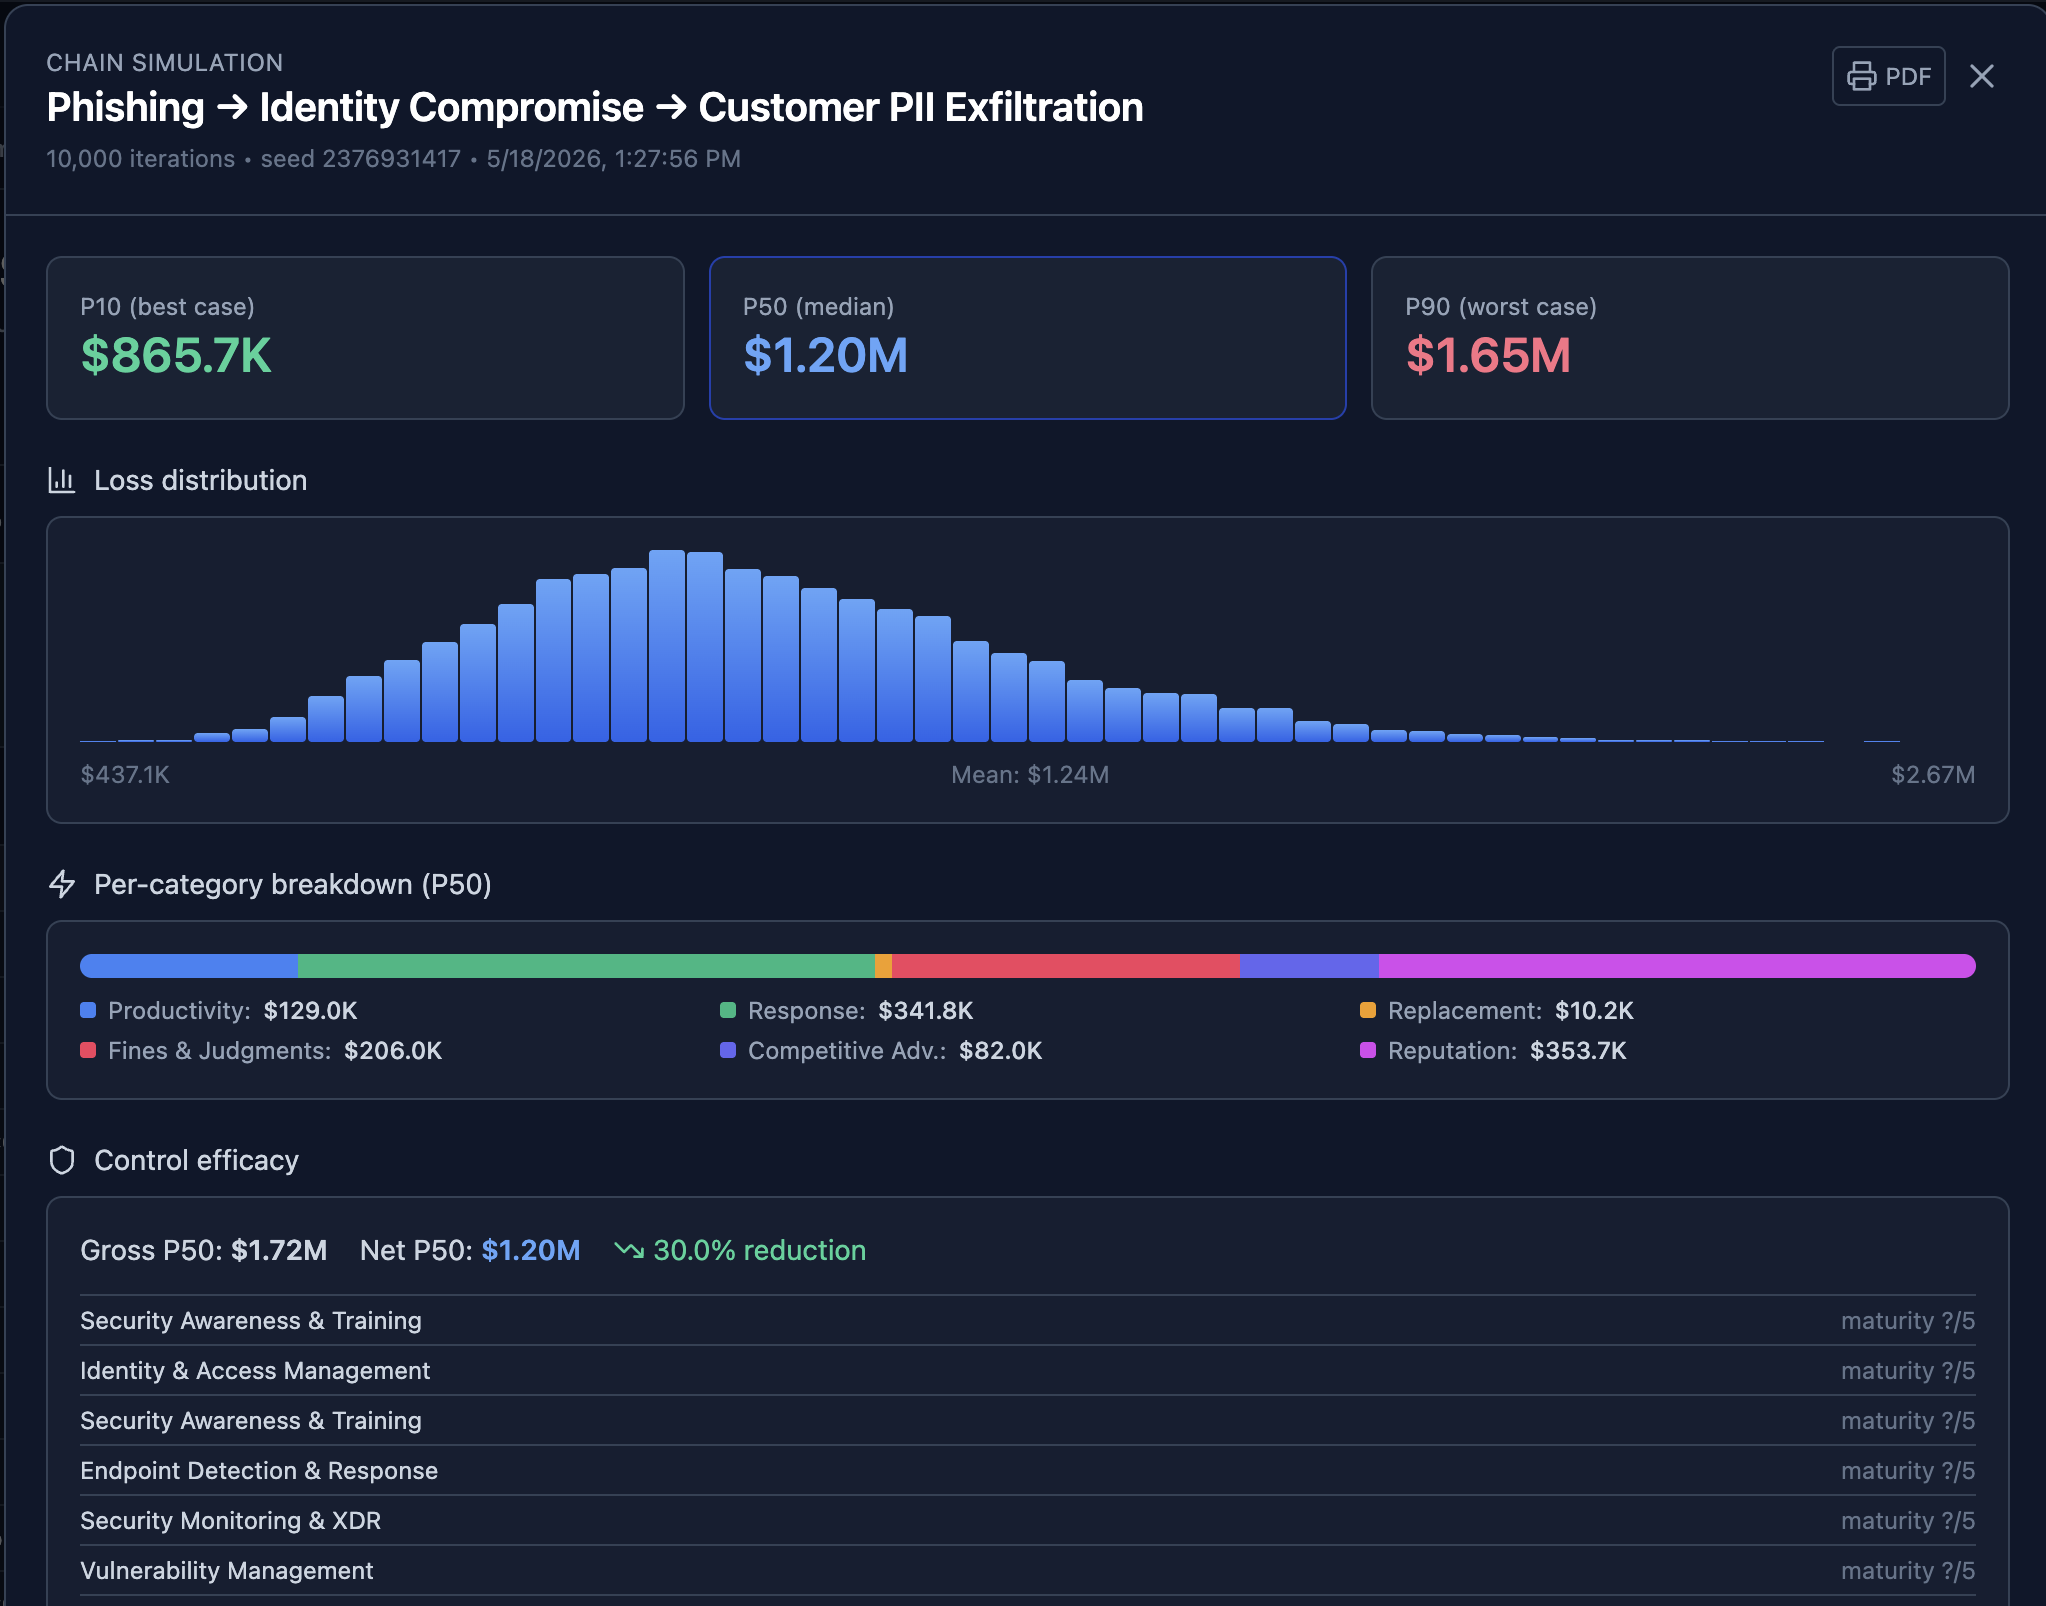
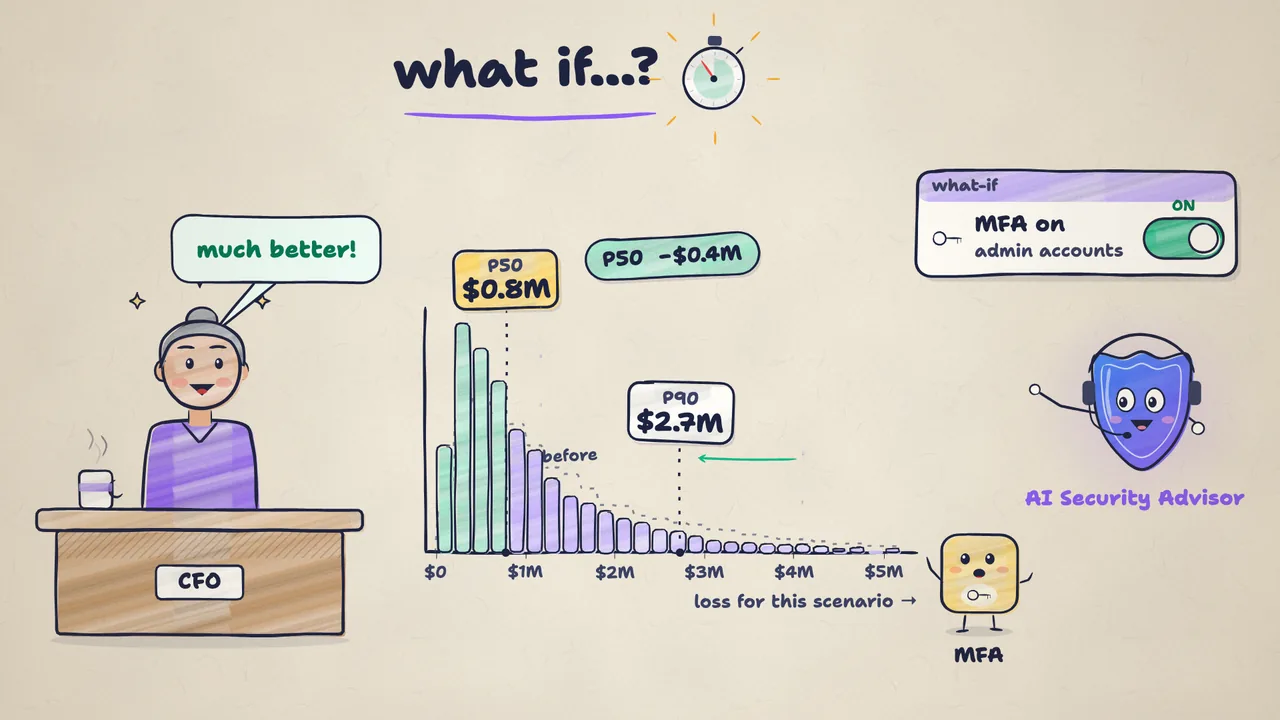
So AI agents translate every signal into FAIR loss outcomes, run thousands of simulations, and show your exposure in dollars, not just colors.
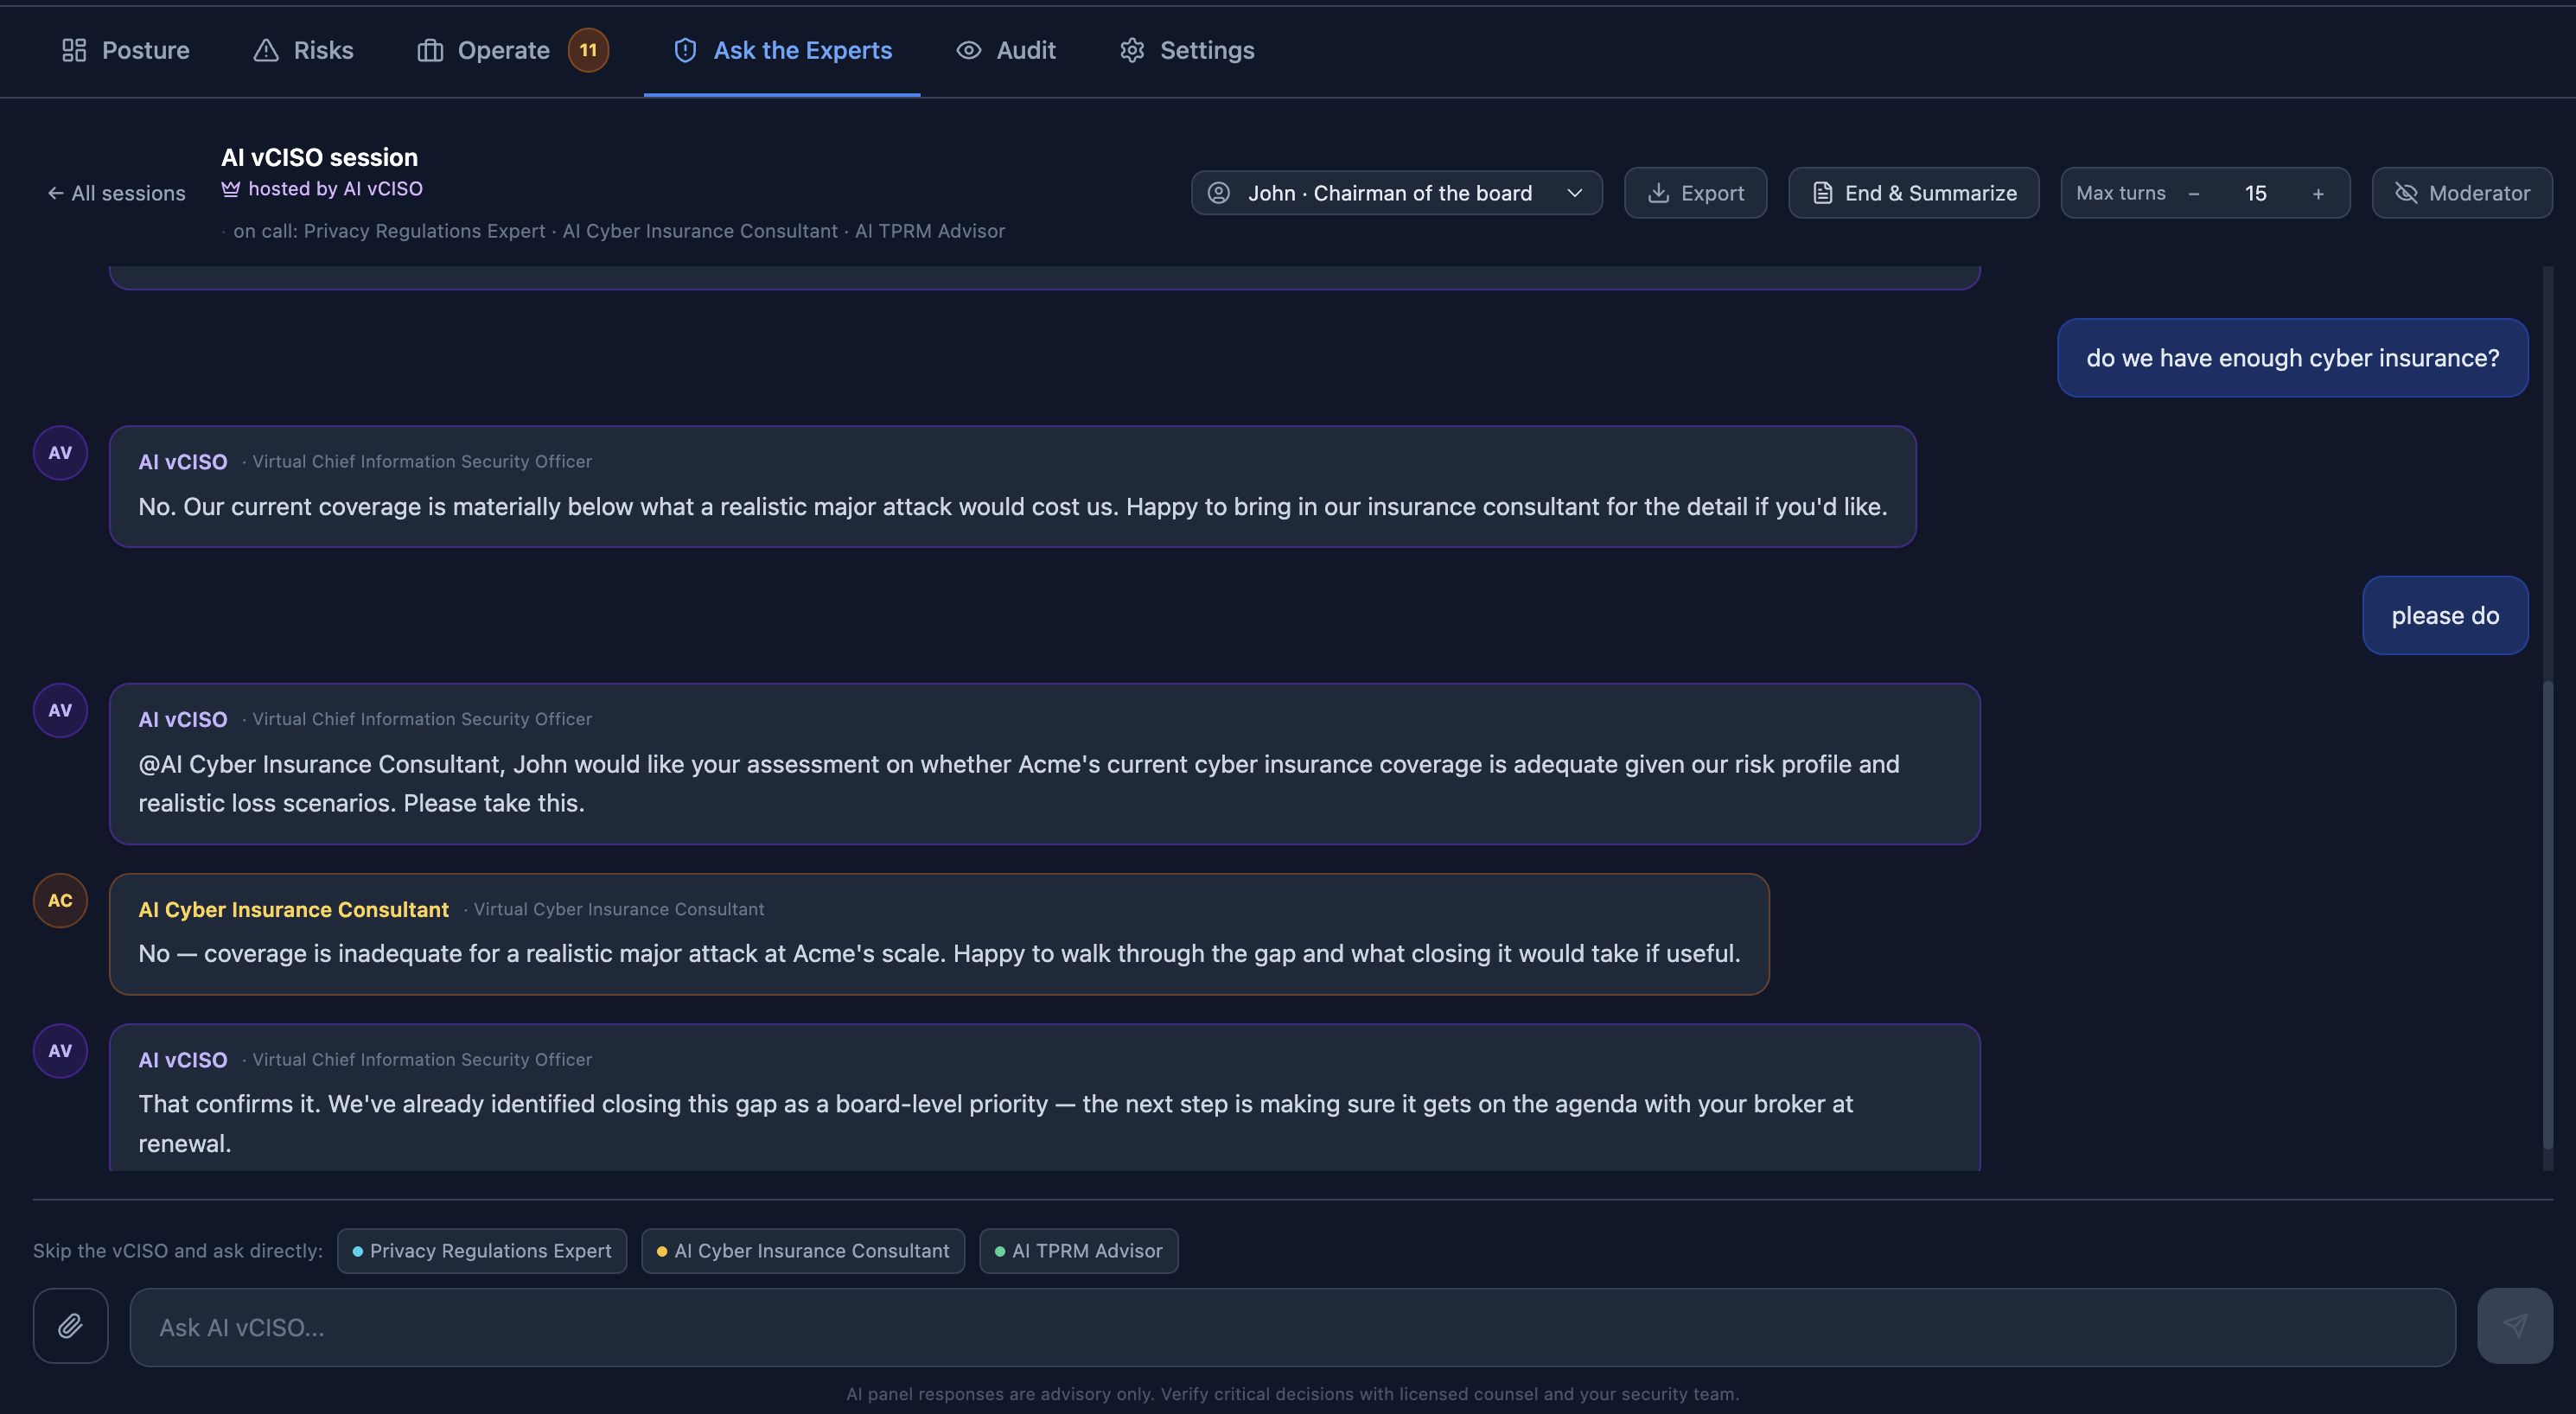
Your AI Security Advisor works beside your security and tech leadership, with clear answers for the CFO and the board.
Draxis. Don’t wait for the breach to read the signal.
Seven one-minute deep dives go through each part of the platform. See all explainer films →
How it works
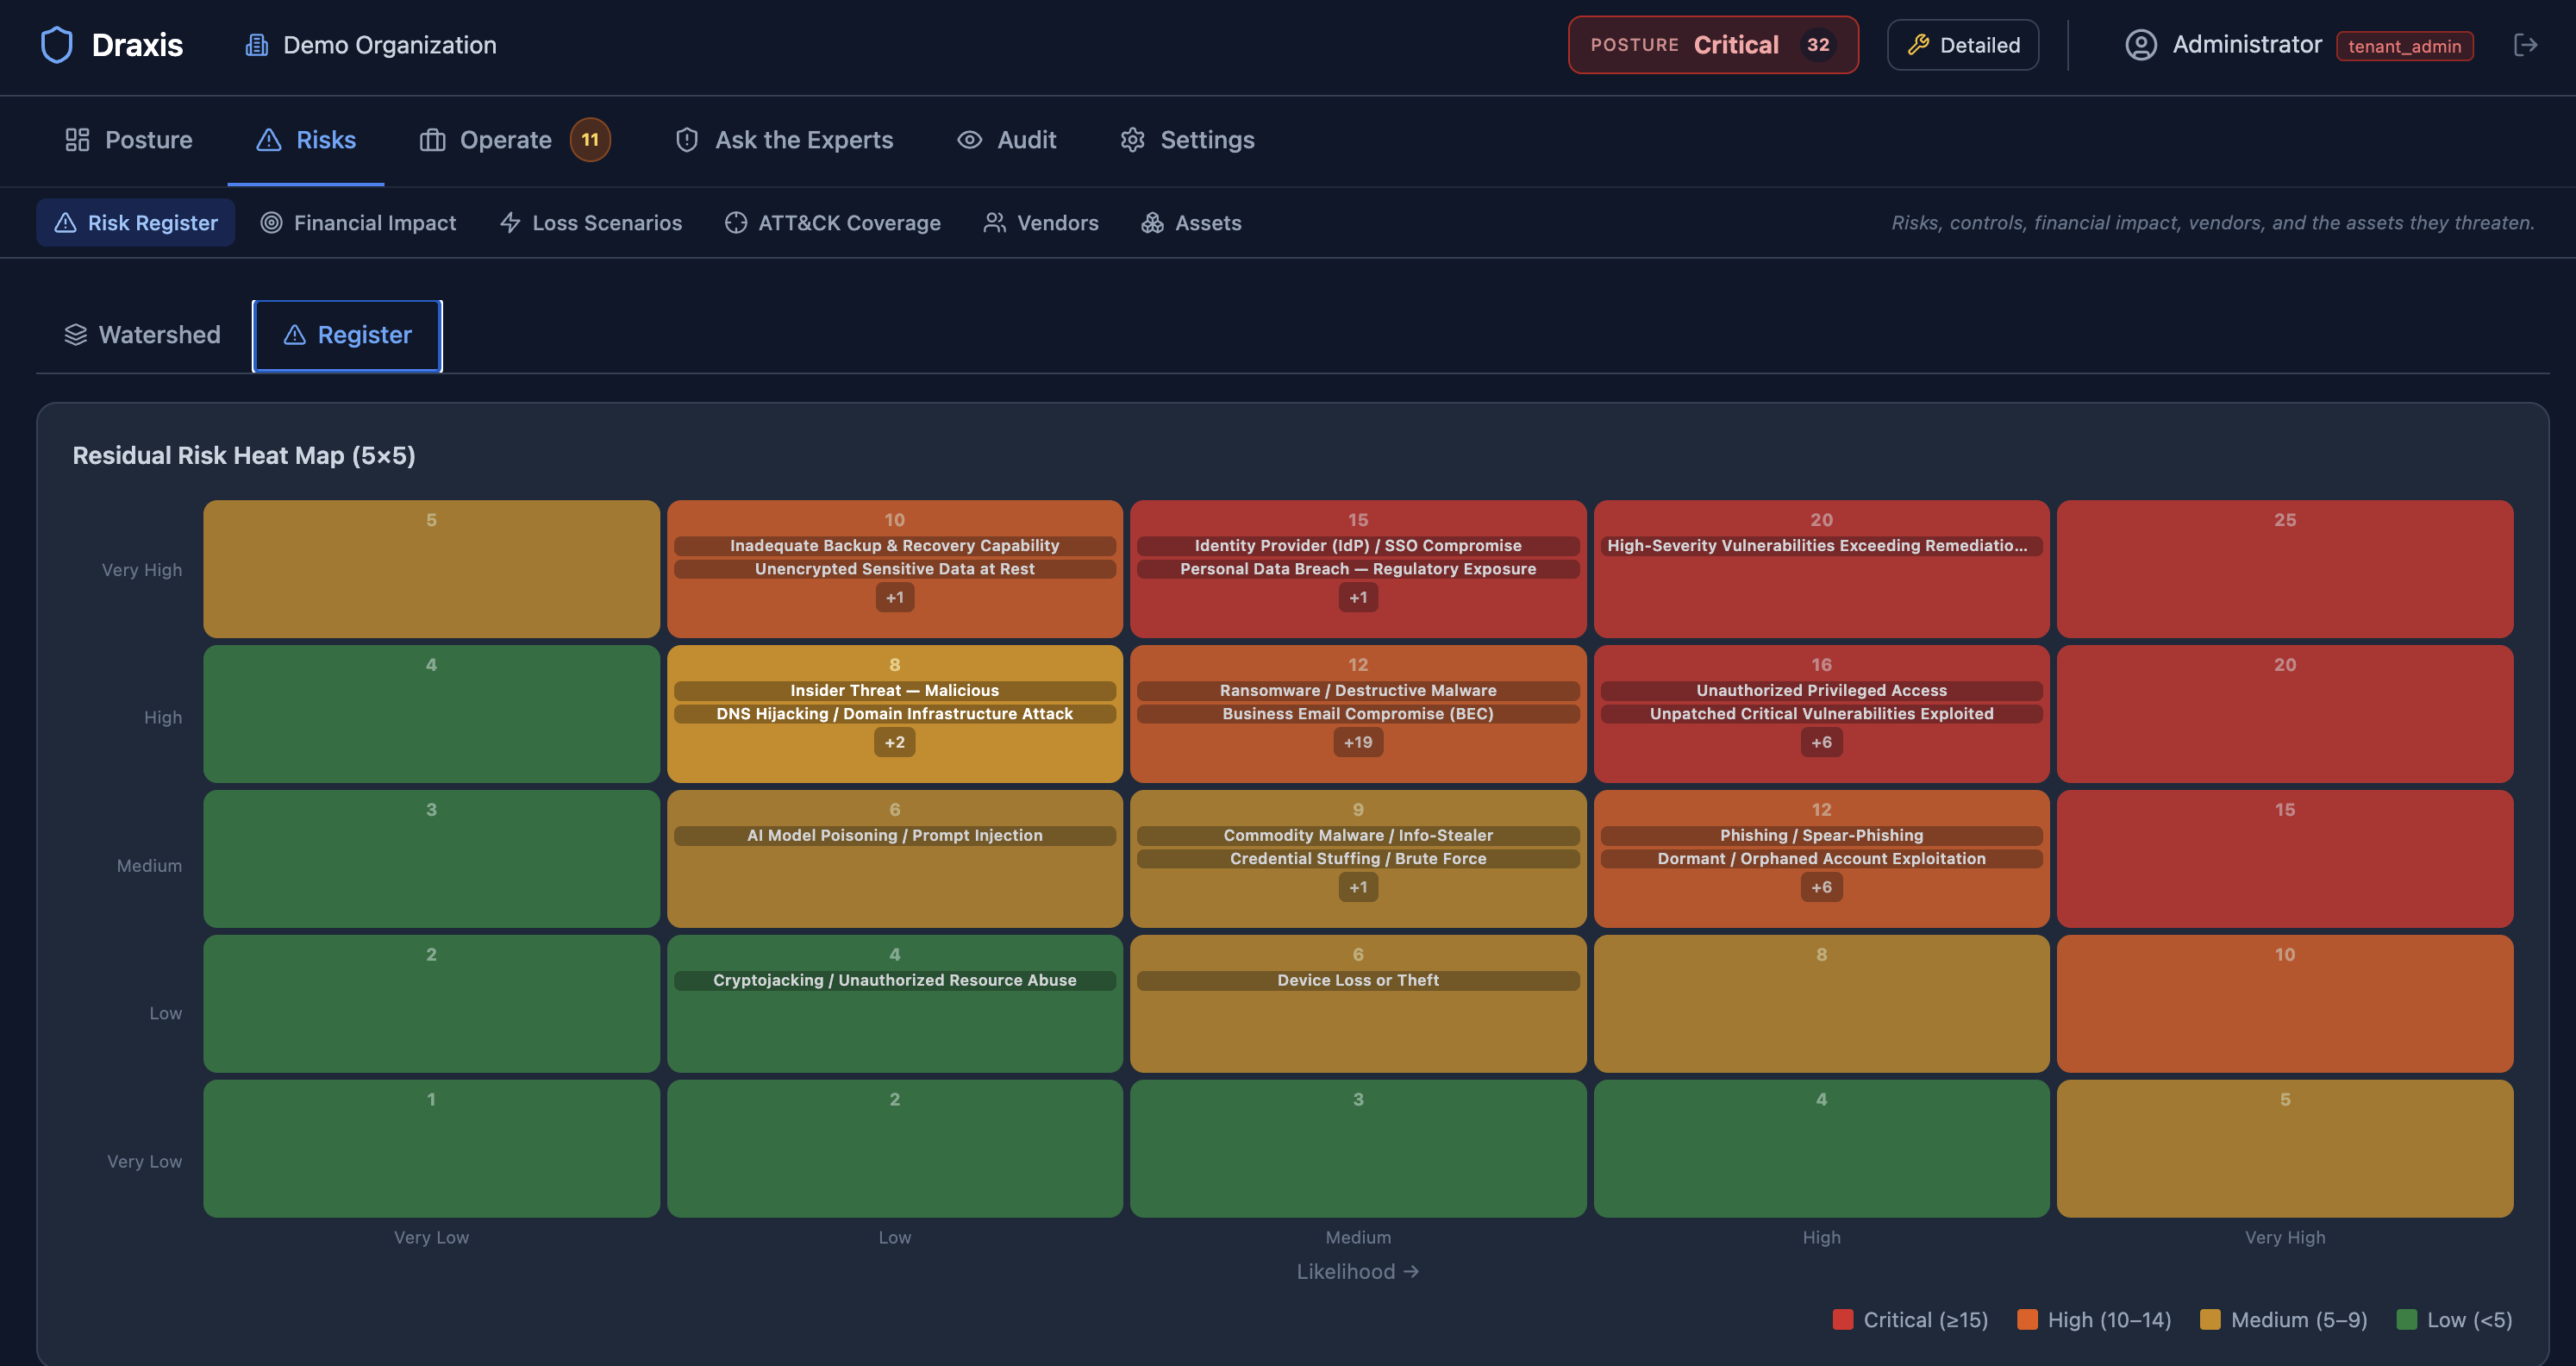
Your security tools are doing their job. Nobody has time to read them.
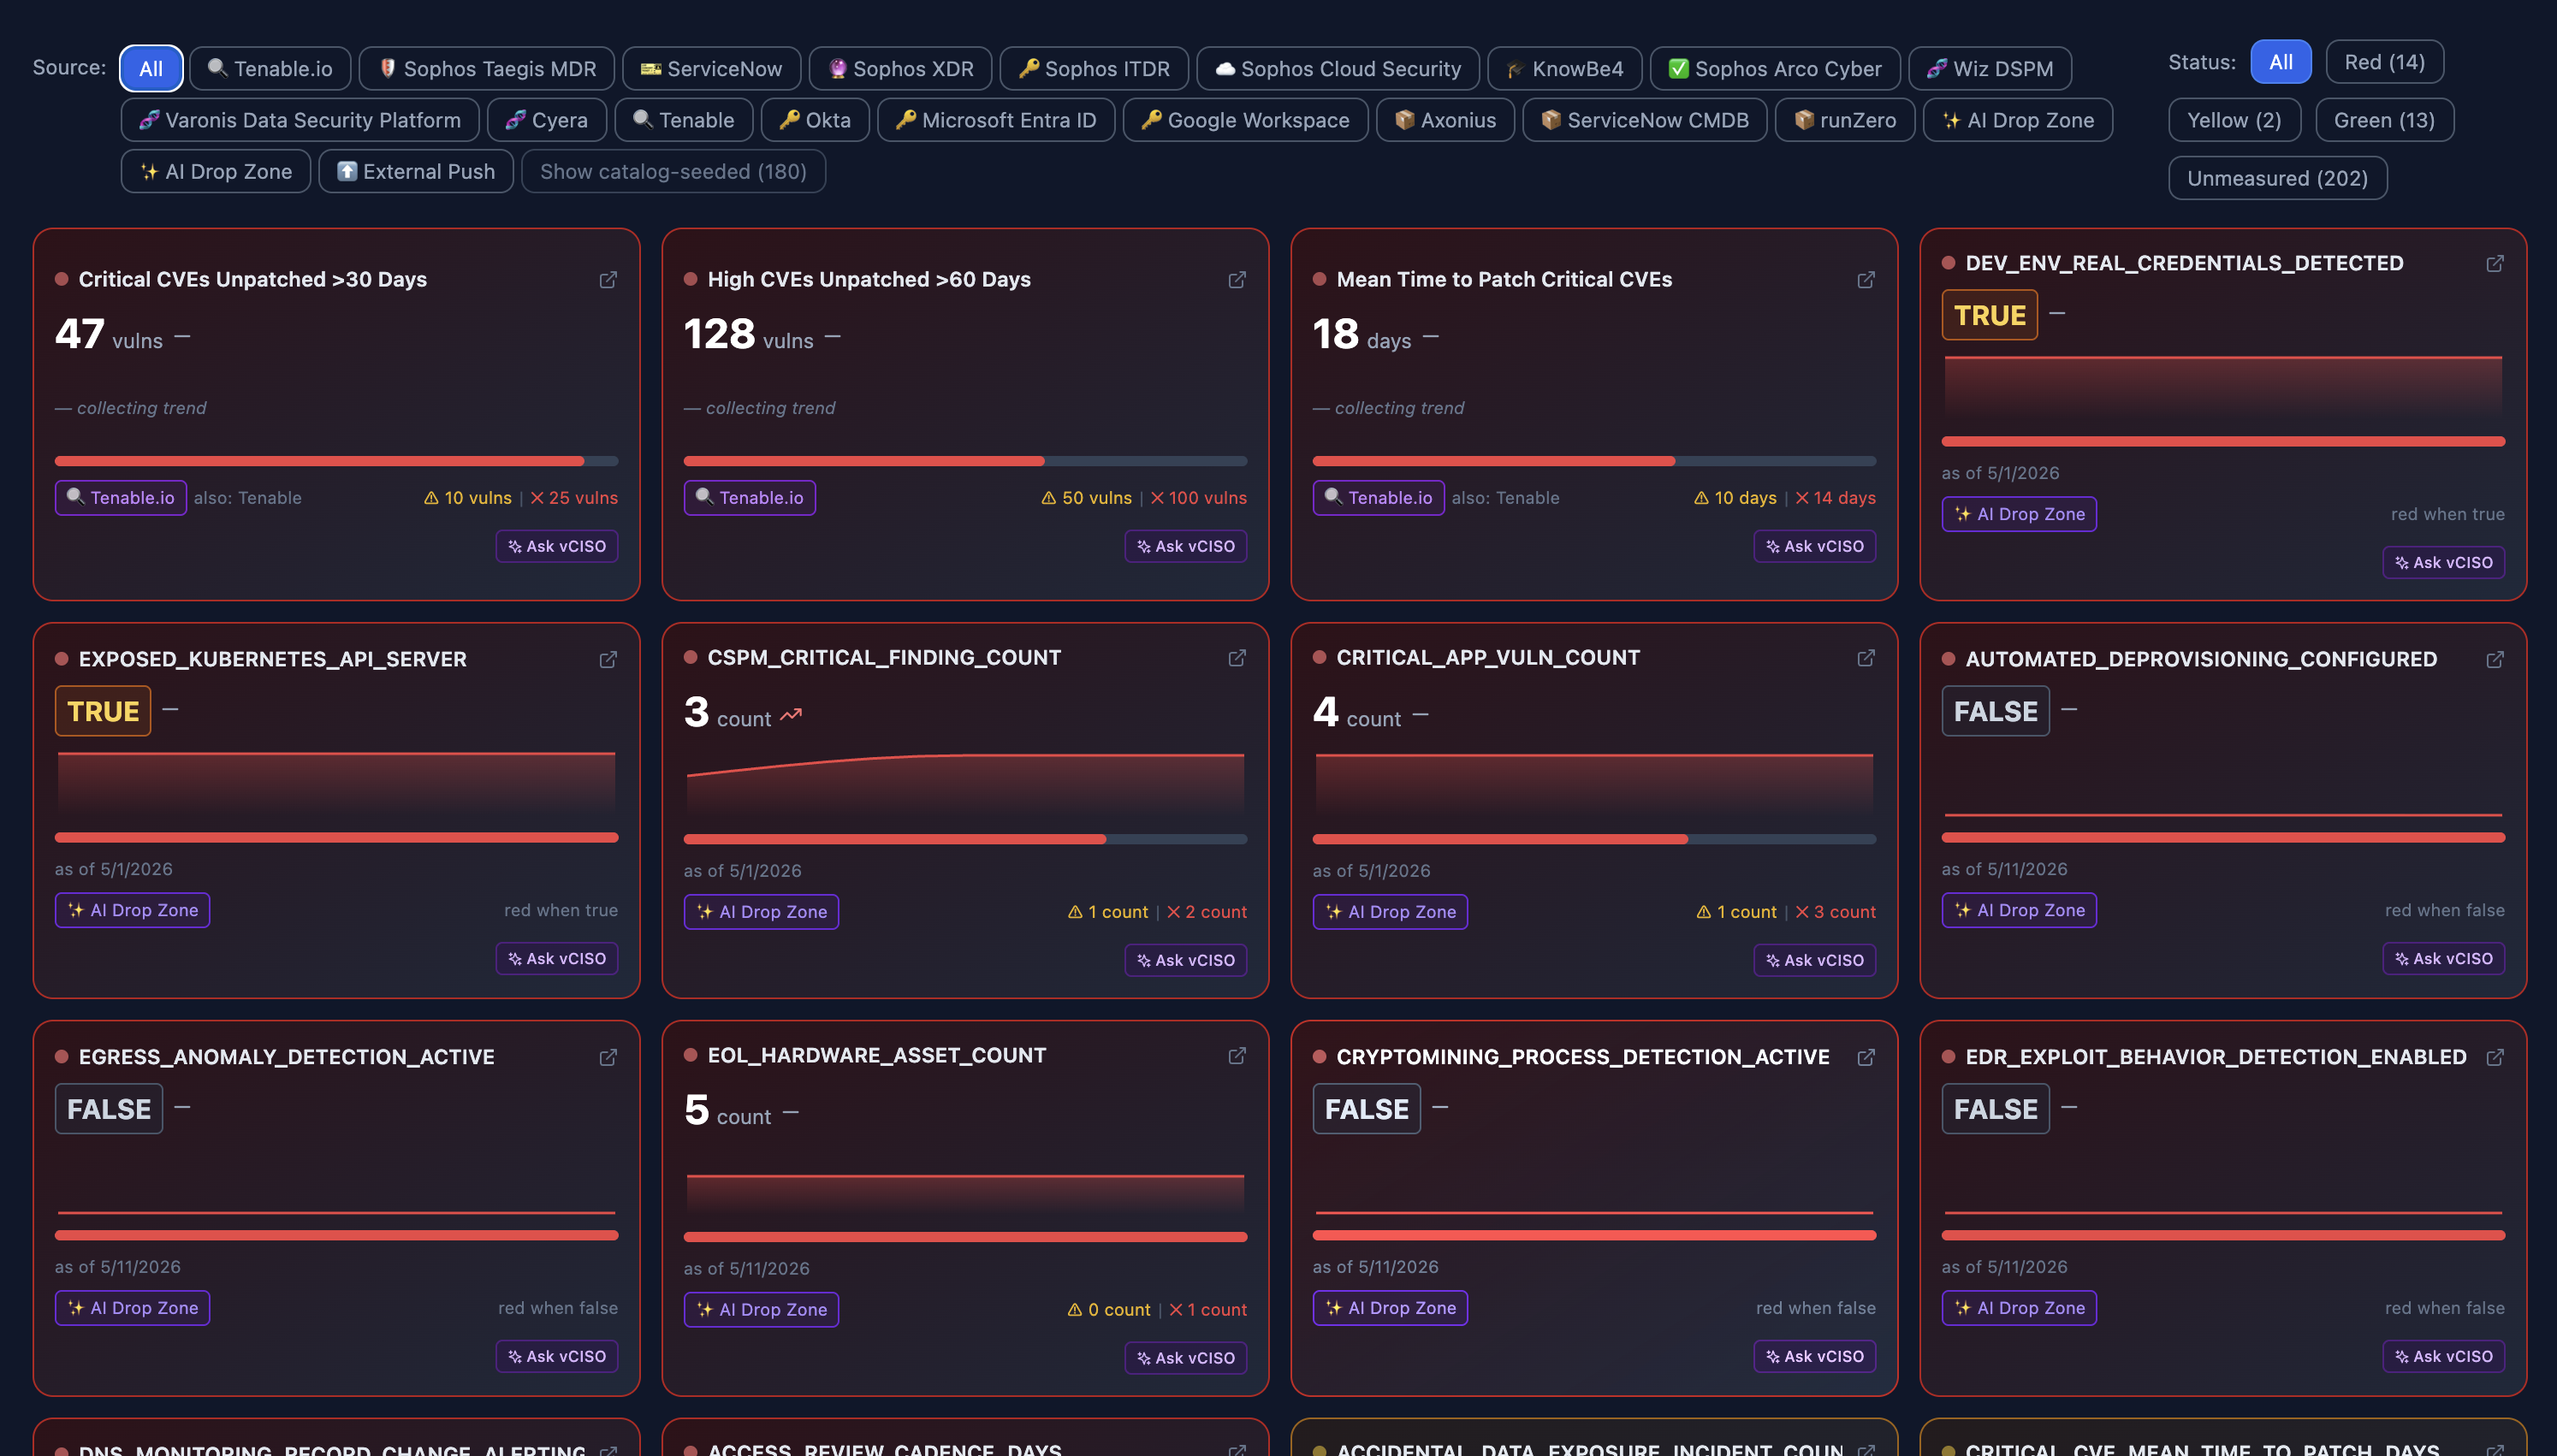
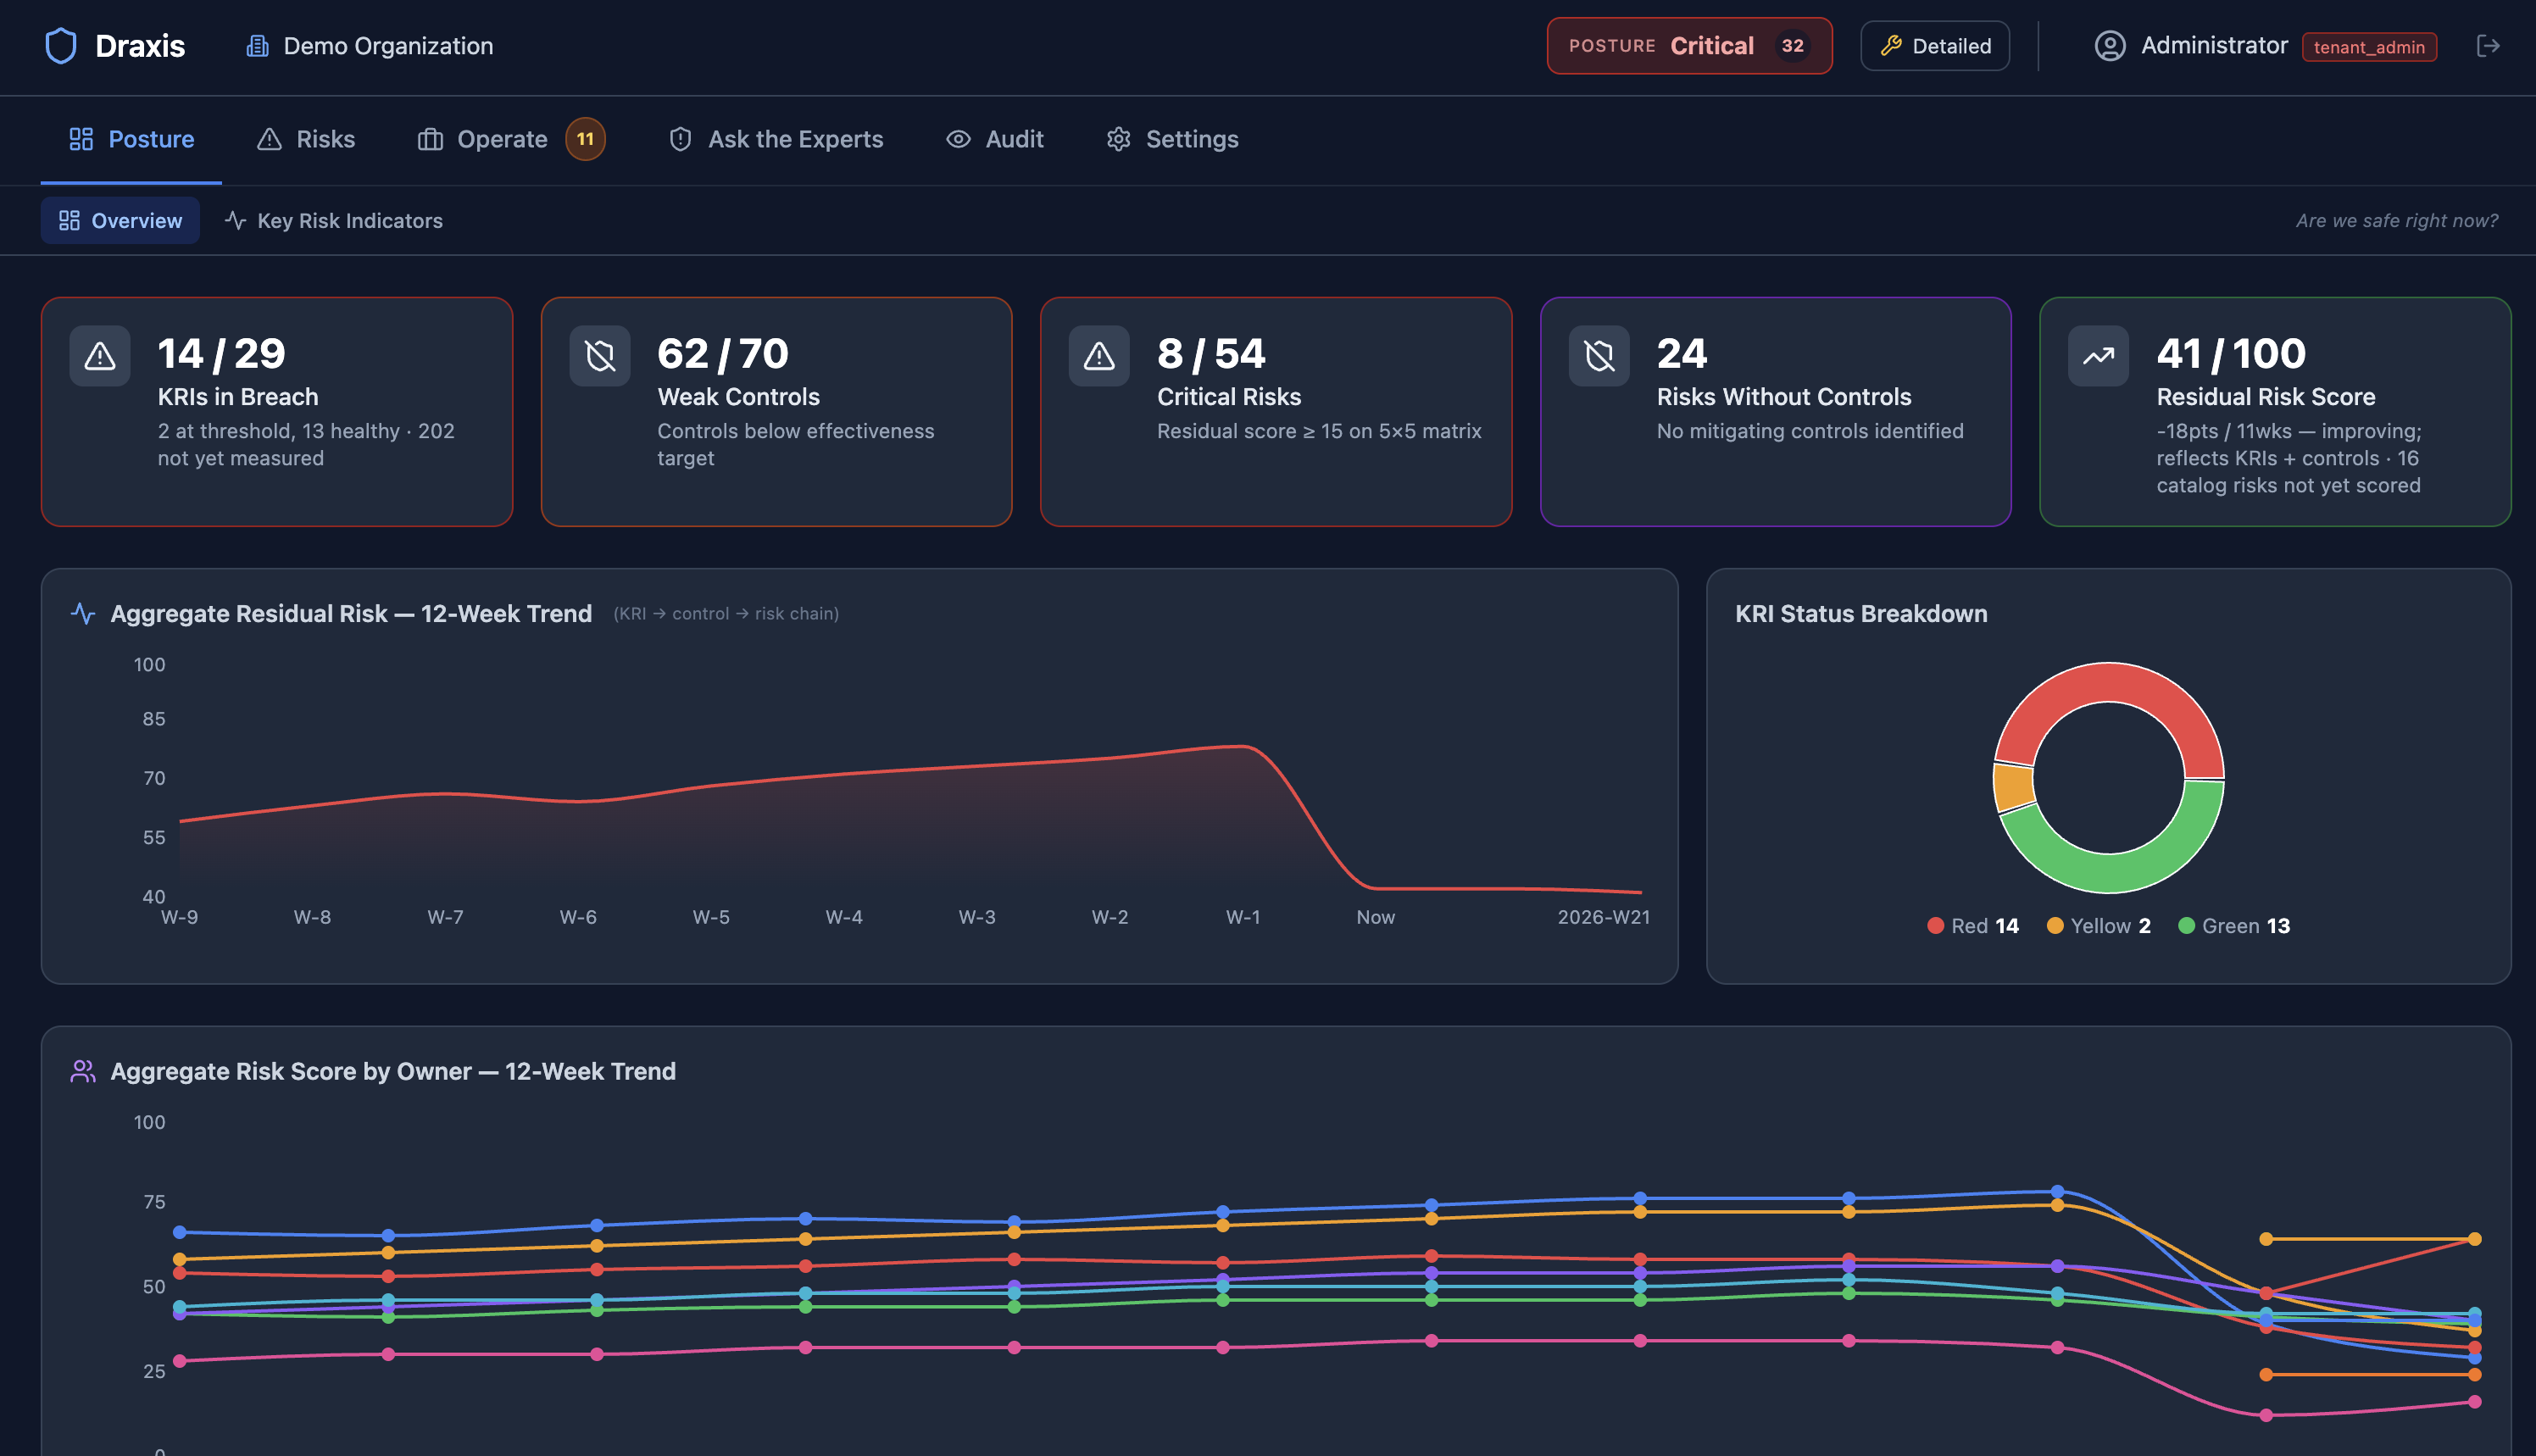
Your SIEM, EDR, vuln scanner, identity platform, and cloud tools generate millions of signals a quarter. Your real risk is in there, changing every day, and most teams find out about it in retrospect. Draxis reads it continuously and gives you a live picture in under 48 hours.
Connect what you already run.
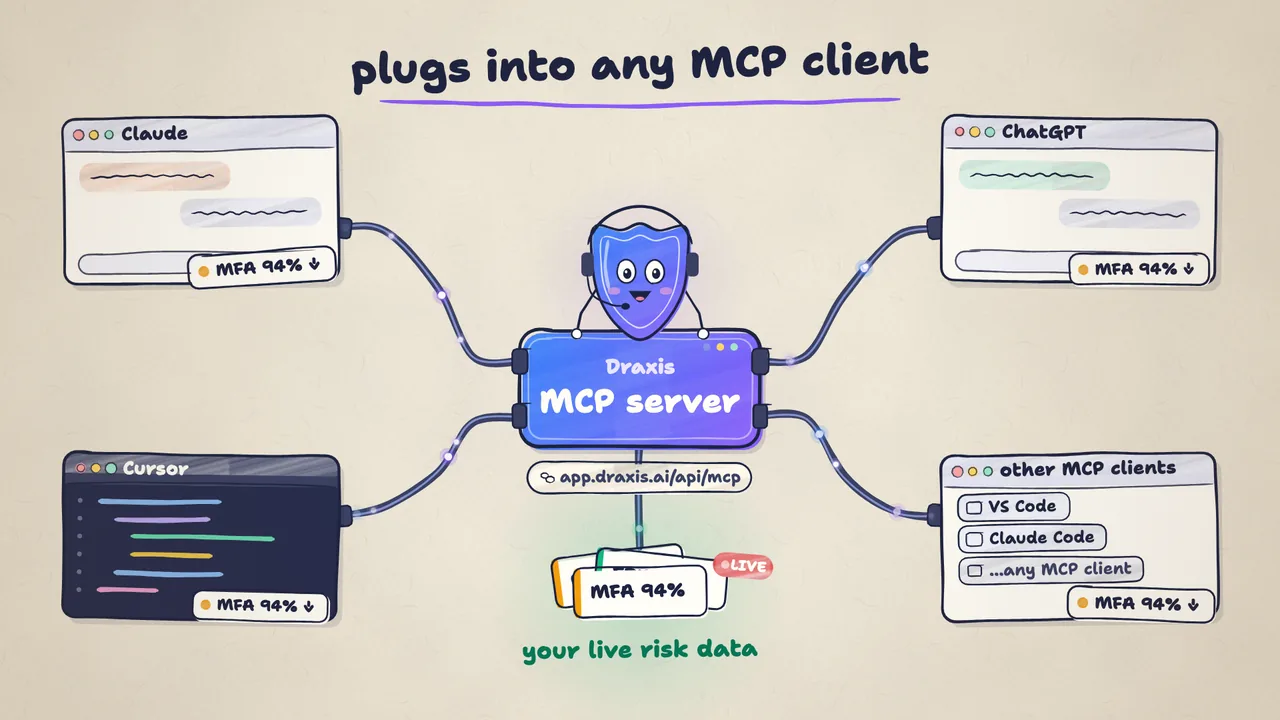
28 native connectors (Okta, Defender, CrowdStrike, Tenable, Splunk, AWS, and more), plus MCP and a REST API for everything else. 180 KRIs map into the risk catalog and your Risk Register is populated on day one.
Trend the signal. Catch the drift early.
Draxis trends every KRI daily, so you see which way each one is moving and how fast. When your drift matches a pattern that preceded a real incident, you get a warning that names the match.
Put a dollar figure on the exposure.
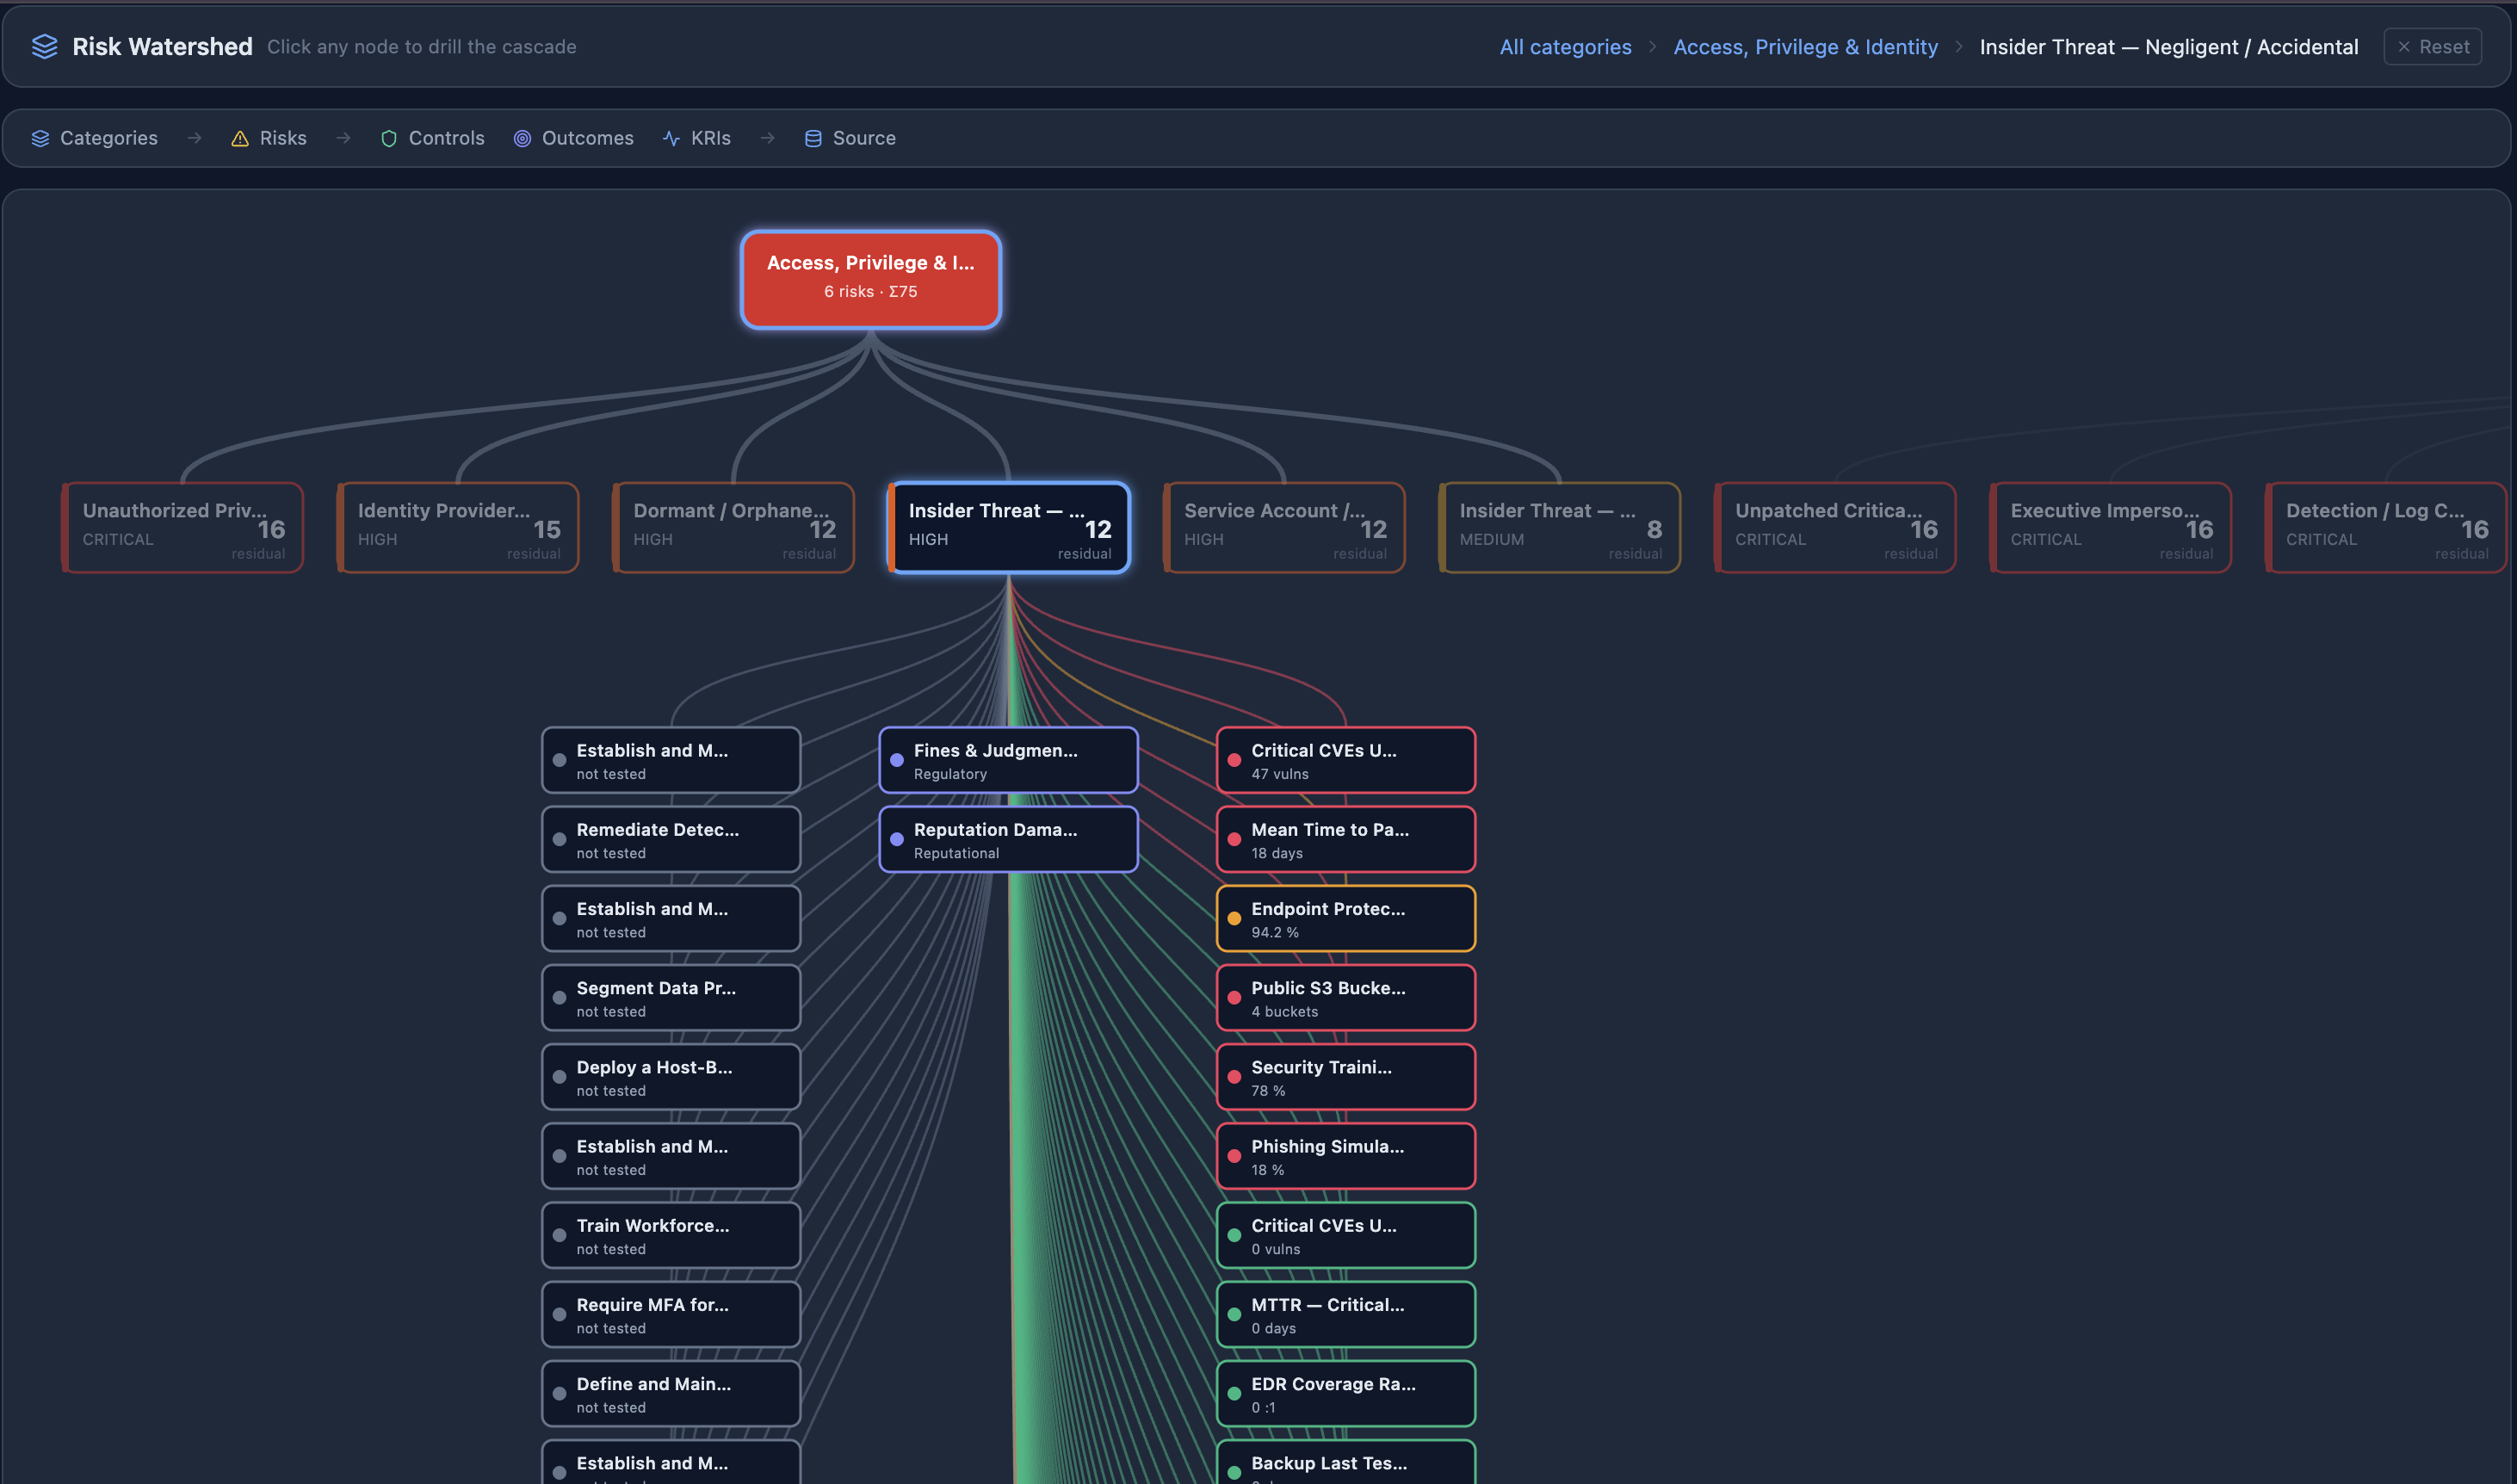
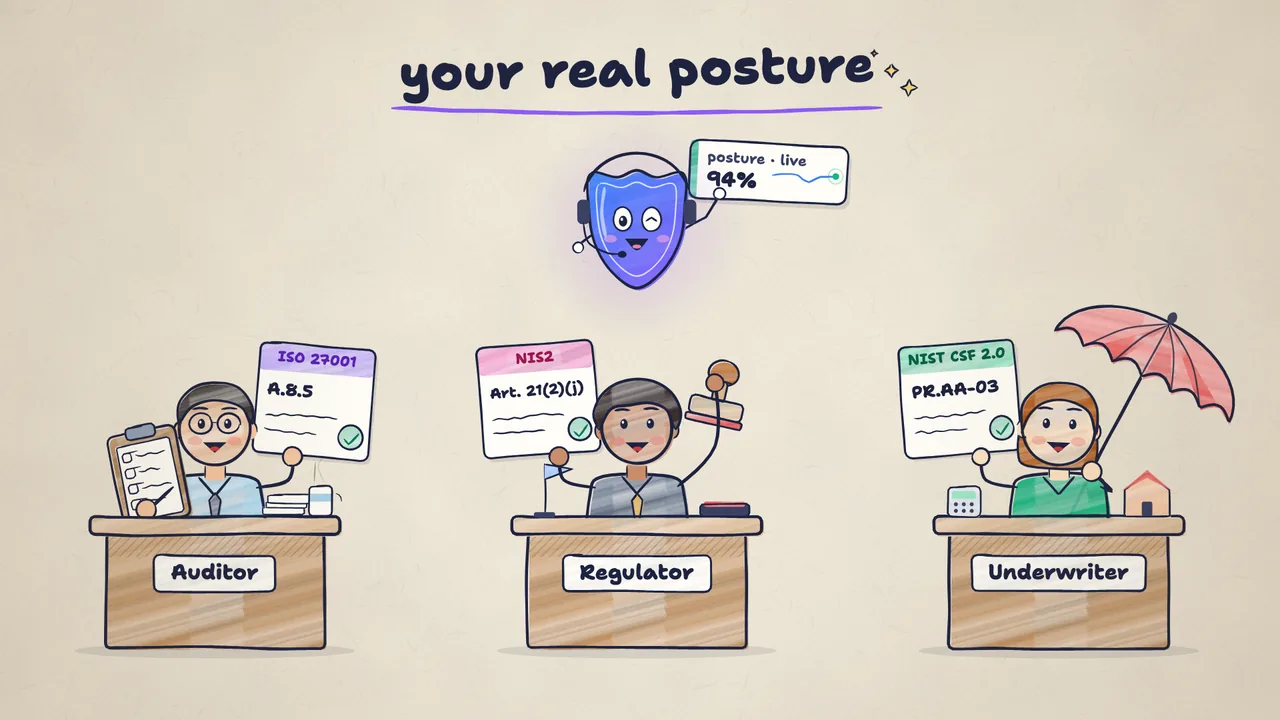
Monte Carlo loss scenarios run against your real asset and identity inventory and return P10, P50, and P90 losses. The auditor evidence, the regulator notification, and the insurer submission all draft from that same picture.
Those warnings draw on your own incident history first, then on Draxis Axon, the cross-tenant network of anonymized drift patterns. No raw values leave your tenant. How Axon works →
Explainer films · sound on
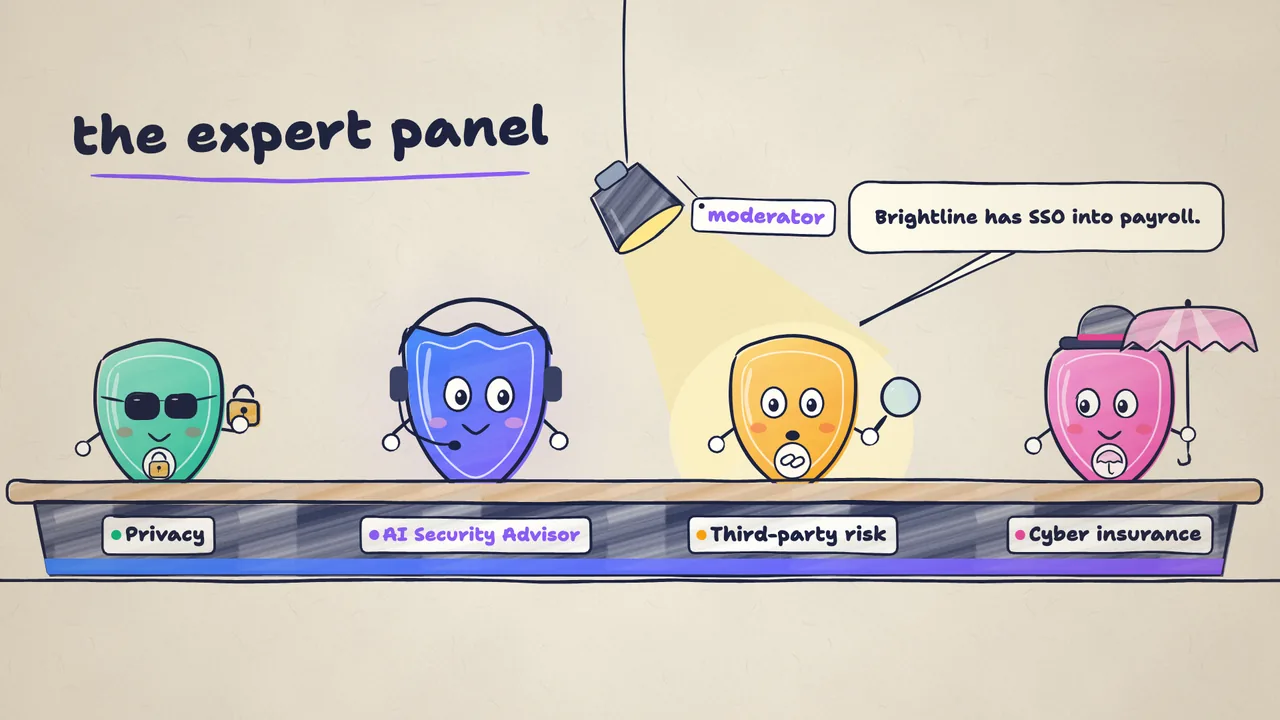
Six parts of the platform, one minute each.
Pick the part you care about. Each film walks through one piece of Draxis in about a minute.
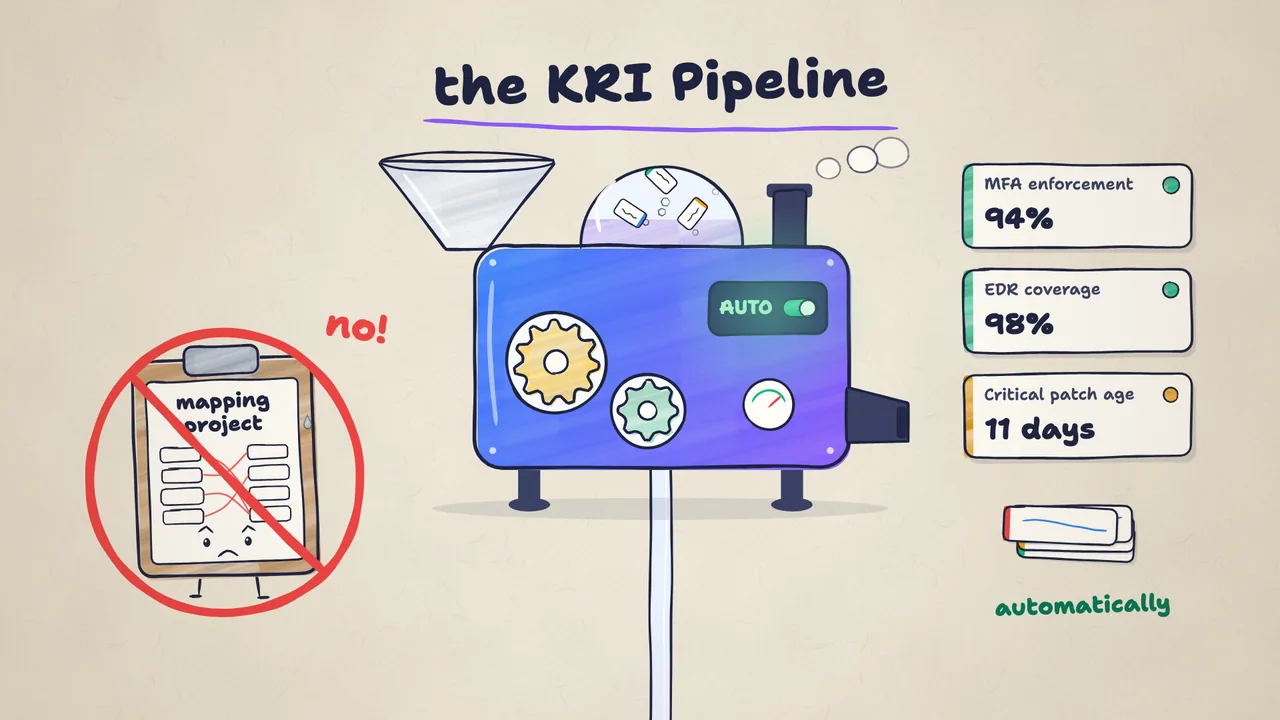
Deep dive 5, the Partner Console for MSSPs, is on the Partner Program page. The written detail behind every film is on the platform page.
AI-first by design. Not AI bolted on after the fact.
Draxis is cyber risk intelligence. It assumes your controls already exist, reads what they’re saying, and turns that into a quantified picture of your exposure. It is not a GRC tool, a vulnerability scanner, an external attack-surface score, or a SIEM.
Already on Vanta, Drata, Bitsight, or SecurityScorecard? Good. Draxis reads from them.
Who it’s for
If your last 90 days included one of these,
you’re who Draxis is built for.
Cyber insurance renewal. SEC, DORA, or NIS2 filing. The board asked for a cyber risk briefing. A peer in your industry got breached. A new privacy law shipped.
$50M–$1B revenue, 200–7,500 employees
You have the stack (EDR, SIEM, identity, vuln scanning) and a security lead with no time to keep a live read on it. Draxis does the reading, and the view is set per user: your analyst gets the full Risk Register while your CFO gets a plain GOOD, WATCH, or URGENT screen.
vCISOs and advisory firms
You can’t keep a live read on ten clients’ environments by hand and still have time to advise them. Draxis does the reading and the drafting for every client tenant, so you take on more clients without adding hours.
See the vCISO program →MSPs and MSSPs
Your managed security stack protects clients. Draxis shows them what that protection is worth in operational, financial, and insurer terms, white-labeled through the Partner Program.
See the MSP program →Decision-makers on the hook for the answer
You’re expected to know your real exposure right now, and to answer the auditor, the regulator, the insurer, and yes the board when they ask. Draxis gives you the live picture and drafts each answer from the same evidence.
Plans
Two plans, scoped to your environment
We price to what you run: organization count, integration surface, and whether you come direct or through a partner. Tell us what your stack looks like and we’ll come back with a number, usually in one call.
The full platform for one organization: your live risk picture, trended continuously, with early warning on top.
- 180 KRIs pulled and trended across 28 integrations (native, MCP, REST)
- Early warning on your own drift, plus Axon cohort benchmarking
- Risk quantification: Monte Carlo loss scenarios (CRSE)
- Full expert panel: AI Security Advisor, Privacy, TPRM, Cyber Insurance
Everything in Signal, plus the full Axon network capability and the controls larger environments need.
- Everything in Signal
- Axon precursor warnings: cross-tenant pattern matches with a track record
- Carrier and underwriter reporting (separate consent gate)
- SSO (SAML / OIDC), additional business units, priority support and SLA
Running an advisory practice or an MSP/MSSP? The Partner Program delivers multi-tenant, white-label Draxis across every client. Draxis needs an existing security stack to read. If you’re building your first security program, we can point you to the right resources first.
Your data, your control.
Four ways to connect Draxis to your stack, from full read-only integration to push-only with zero tool access. Every tenant gets its own database, and every security event lands in an immutable audit log.
See your actual risk, live, by the end of the week.
Connect a few read-only APIs. Within 48 hours you’ll have a populated Risk Register, dollar-quantified loss scenarios, and a live picture of your real exposure. No agents. No rearchitecting.