Every part of Draxis, in detail.
Draxis pulls Key Risk Indicators from the tools you already run, trends them, warns you on drift, and quantifies the exposure. Each section below covers one part, and most come with a one-minute film.
The signal
Every KRI, pulled continuously and trended over time.
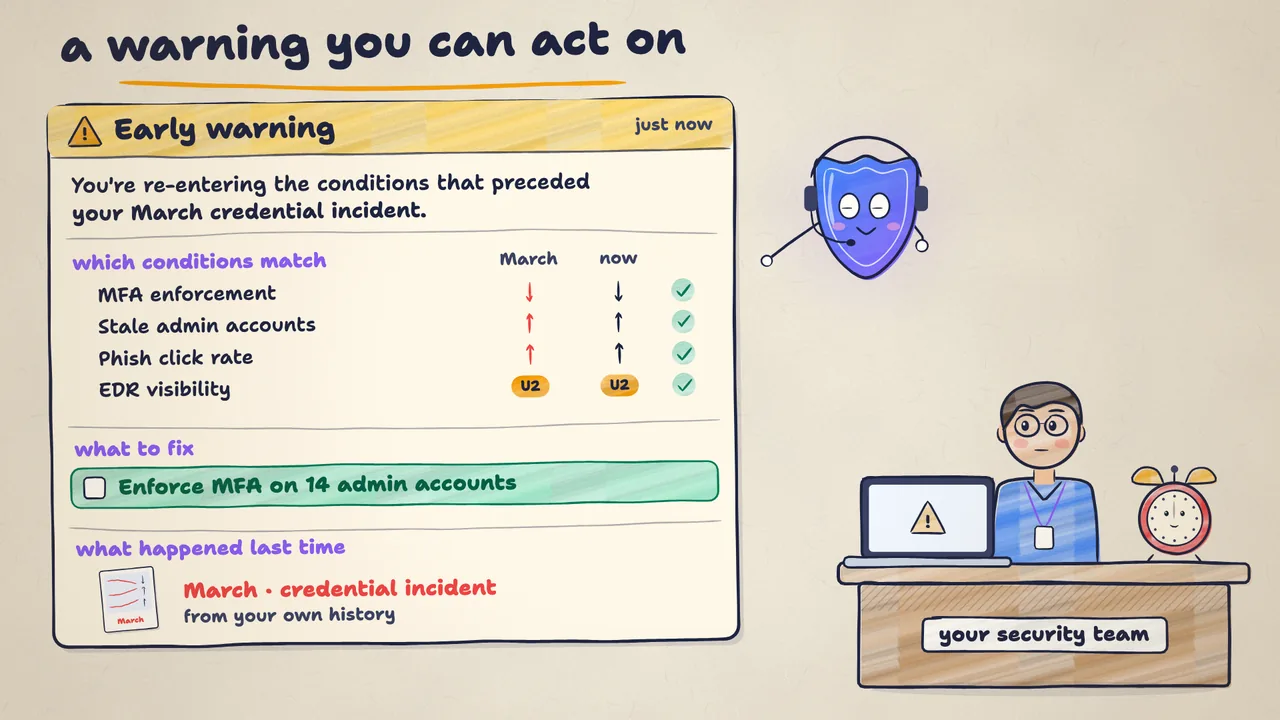
Draxis connects to the tools you already run (EDR, SIEM, CSPM, identity, vuln scanners) and pulls Key Risk Indicators automatically. 180 signals, no analyst configuration, no spreadsheets. Then it does the part nobody has time for: it trends every KRI over time, so you see not just where a metric sits today but which direction it’s moving and how fast.
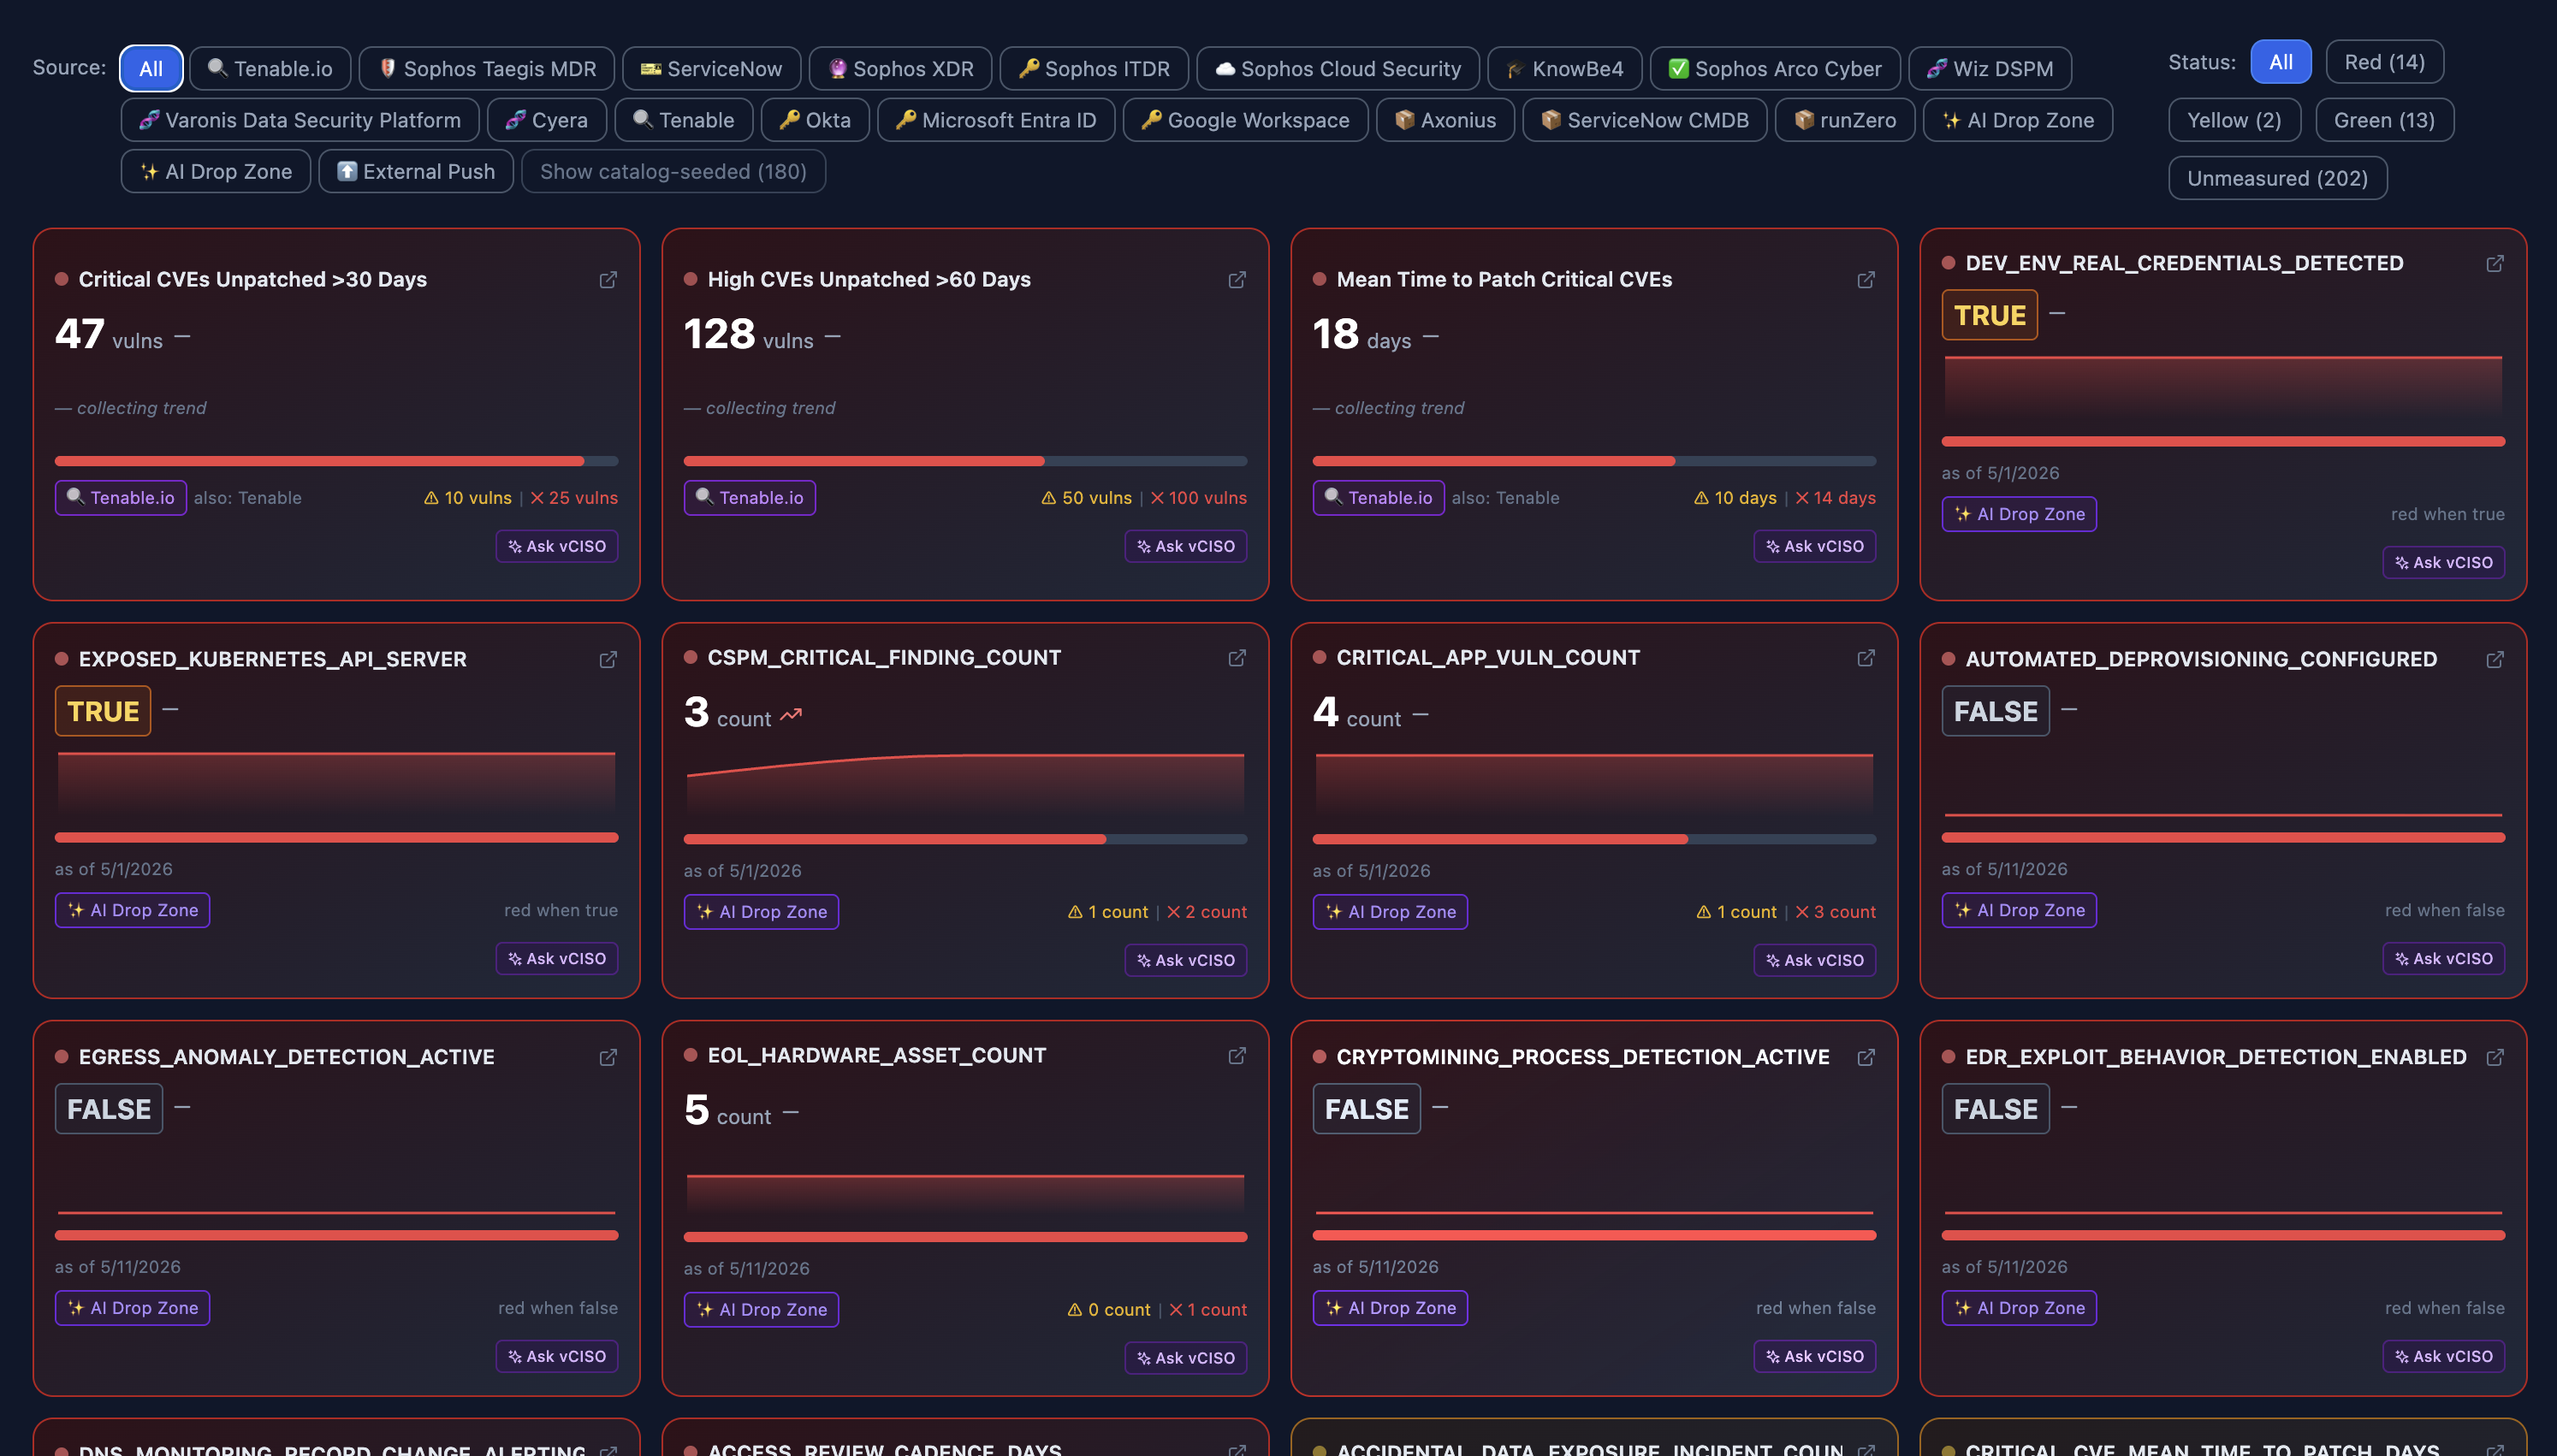
A KRI in the green that’s been sliding for three weeks is a different story than one that’s been stable. Draxis tells you which is which.
180 KRIs, pulled automatically.
From 28 native connectors plus MCP and REST. No manual mapping.
Continuous, not quarterly.
The picture is current today, refreshed as your stack changes, not a snapshot from your last assessment.
Historical drift, not just current state.
Daily-granularity history so you can see the trend forming, not only the value it lands on.
Early warning
Catch the trend before it becomes the failure.
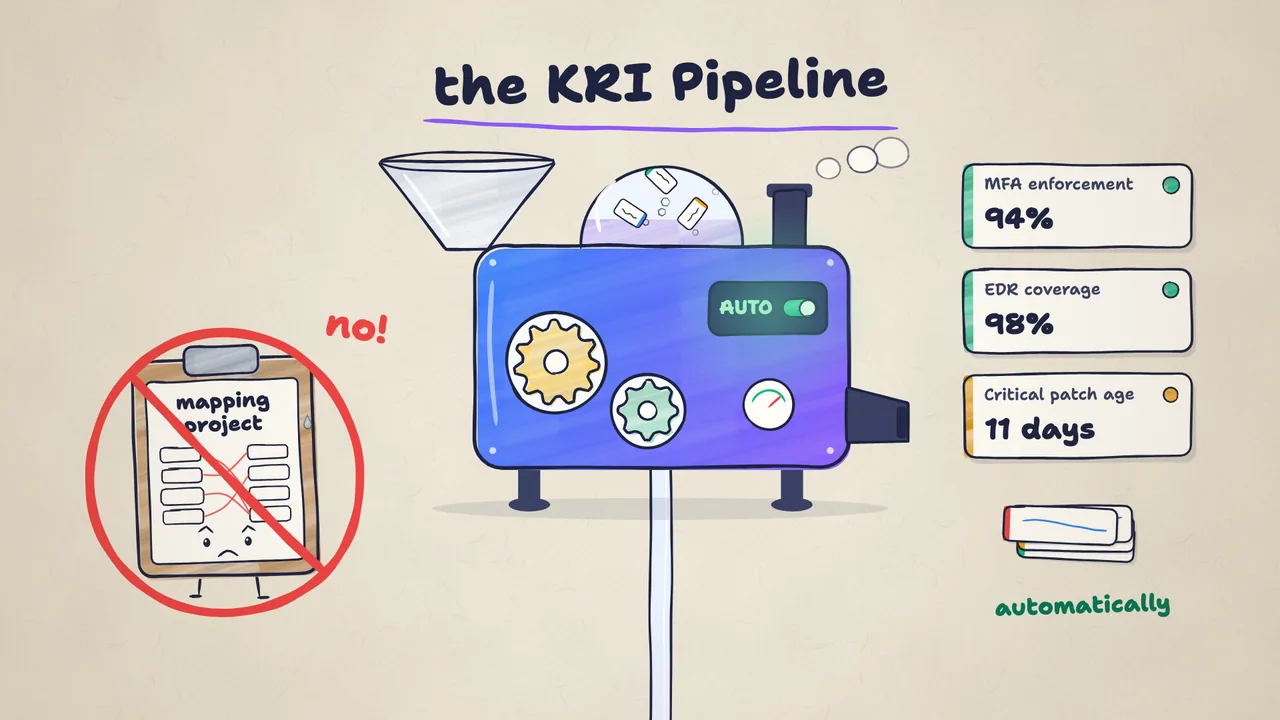
Trending KRIs is only useful if it changes what you do. Draxis watches your live drift against the patterns that have preceded real incidents, your own history first, and the broader Draxis Axon network on top of that. When your KRIs start moving in a way that matches a known precursor signature, Draxis fires a warning.
Not a generic alert. A specific pattern match with a track record:
“You are re-entering the conditions that preceded your March credential incident.”
“Organizations with this drift pattern saw a similar event within 60 days.”
That’s the difference between finding out in retrospect and finding out in time.
Pattern-based, not threshold-based.
A warning fires when drift matches a precursor signature, not just when a single metric crosses a line.
Tenant-local and network-wide.
Learns from your own incident and near-miss history, and from anonymized cross-tenant patterns via Draxis Axon.
Tracks what was averted.
When a warning leads to remediation and no incident follows, that’s the headline number for your insurer and your board: the program working.
Early warning is included in both plans. Cross-tenant precursor warnings via Axon come with Intelligence. See the plans →
Draxis Axon
Every tenant makes the whole network’s warnings sharper.
Draxis Axon is the cross-tenant signal network built into the platform. Every tenant contributes anonymized drift patterns, never raw values, never anything identifiable, and every tenant’s early warnings get sharper as the network grows. When a drift pattern precedes an incident anywhere in the network, that signal protects everyone.
How Axon works →Two modes, one platform
Built for organizations with a CISO. And ones that can’t afford one.
Same AI engine, two distinct experiences. The mode is per-user, so your CFO sees plain English on the same tenant where your analyst sees the full Risk Register.
Amplify the CISO you already have
The problem: your CISO is one person trying to read every signal, run the loss math, and stay current on privacy law, third-party risk, and cyber insurance. Real-time understanding of the actual environment is the first thing that falls off the desk.
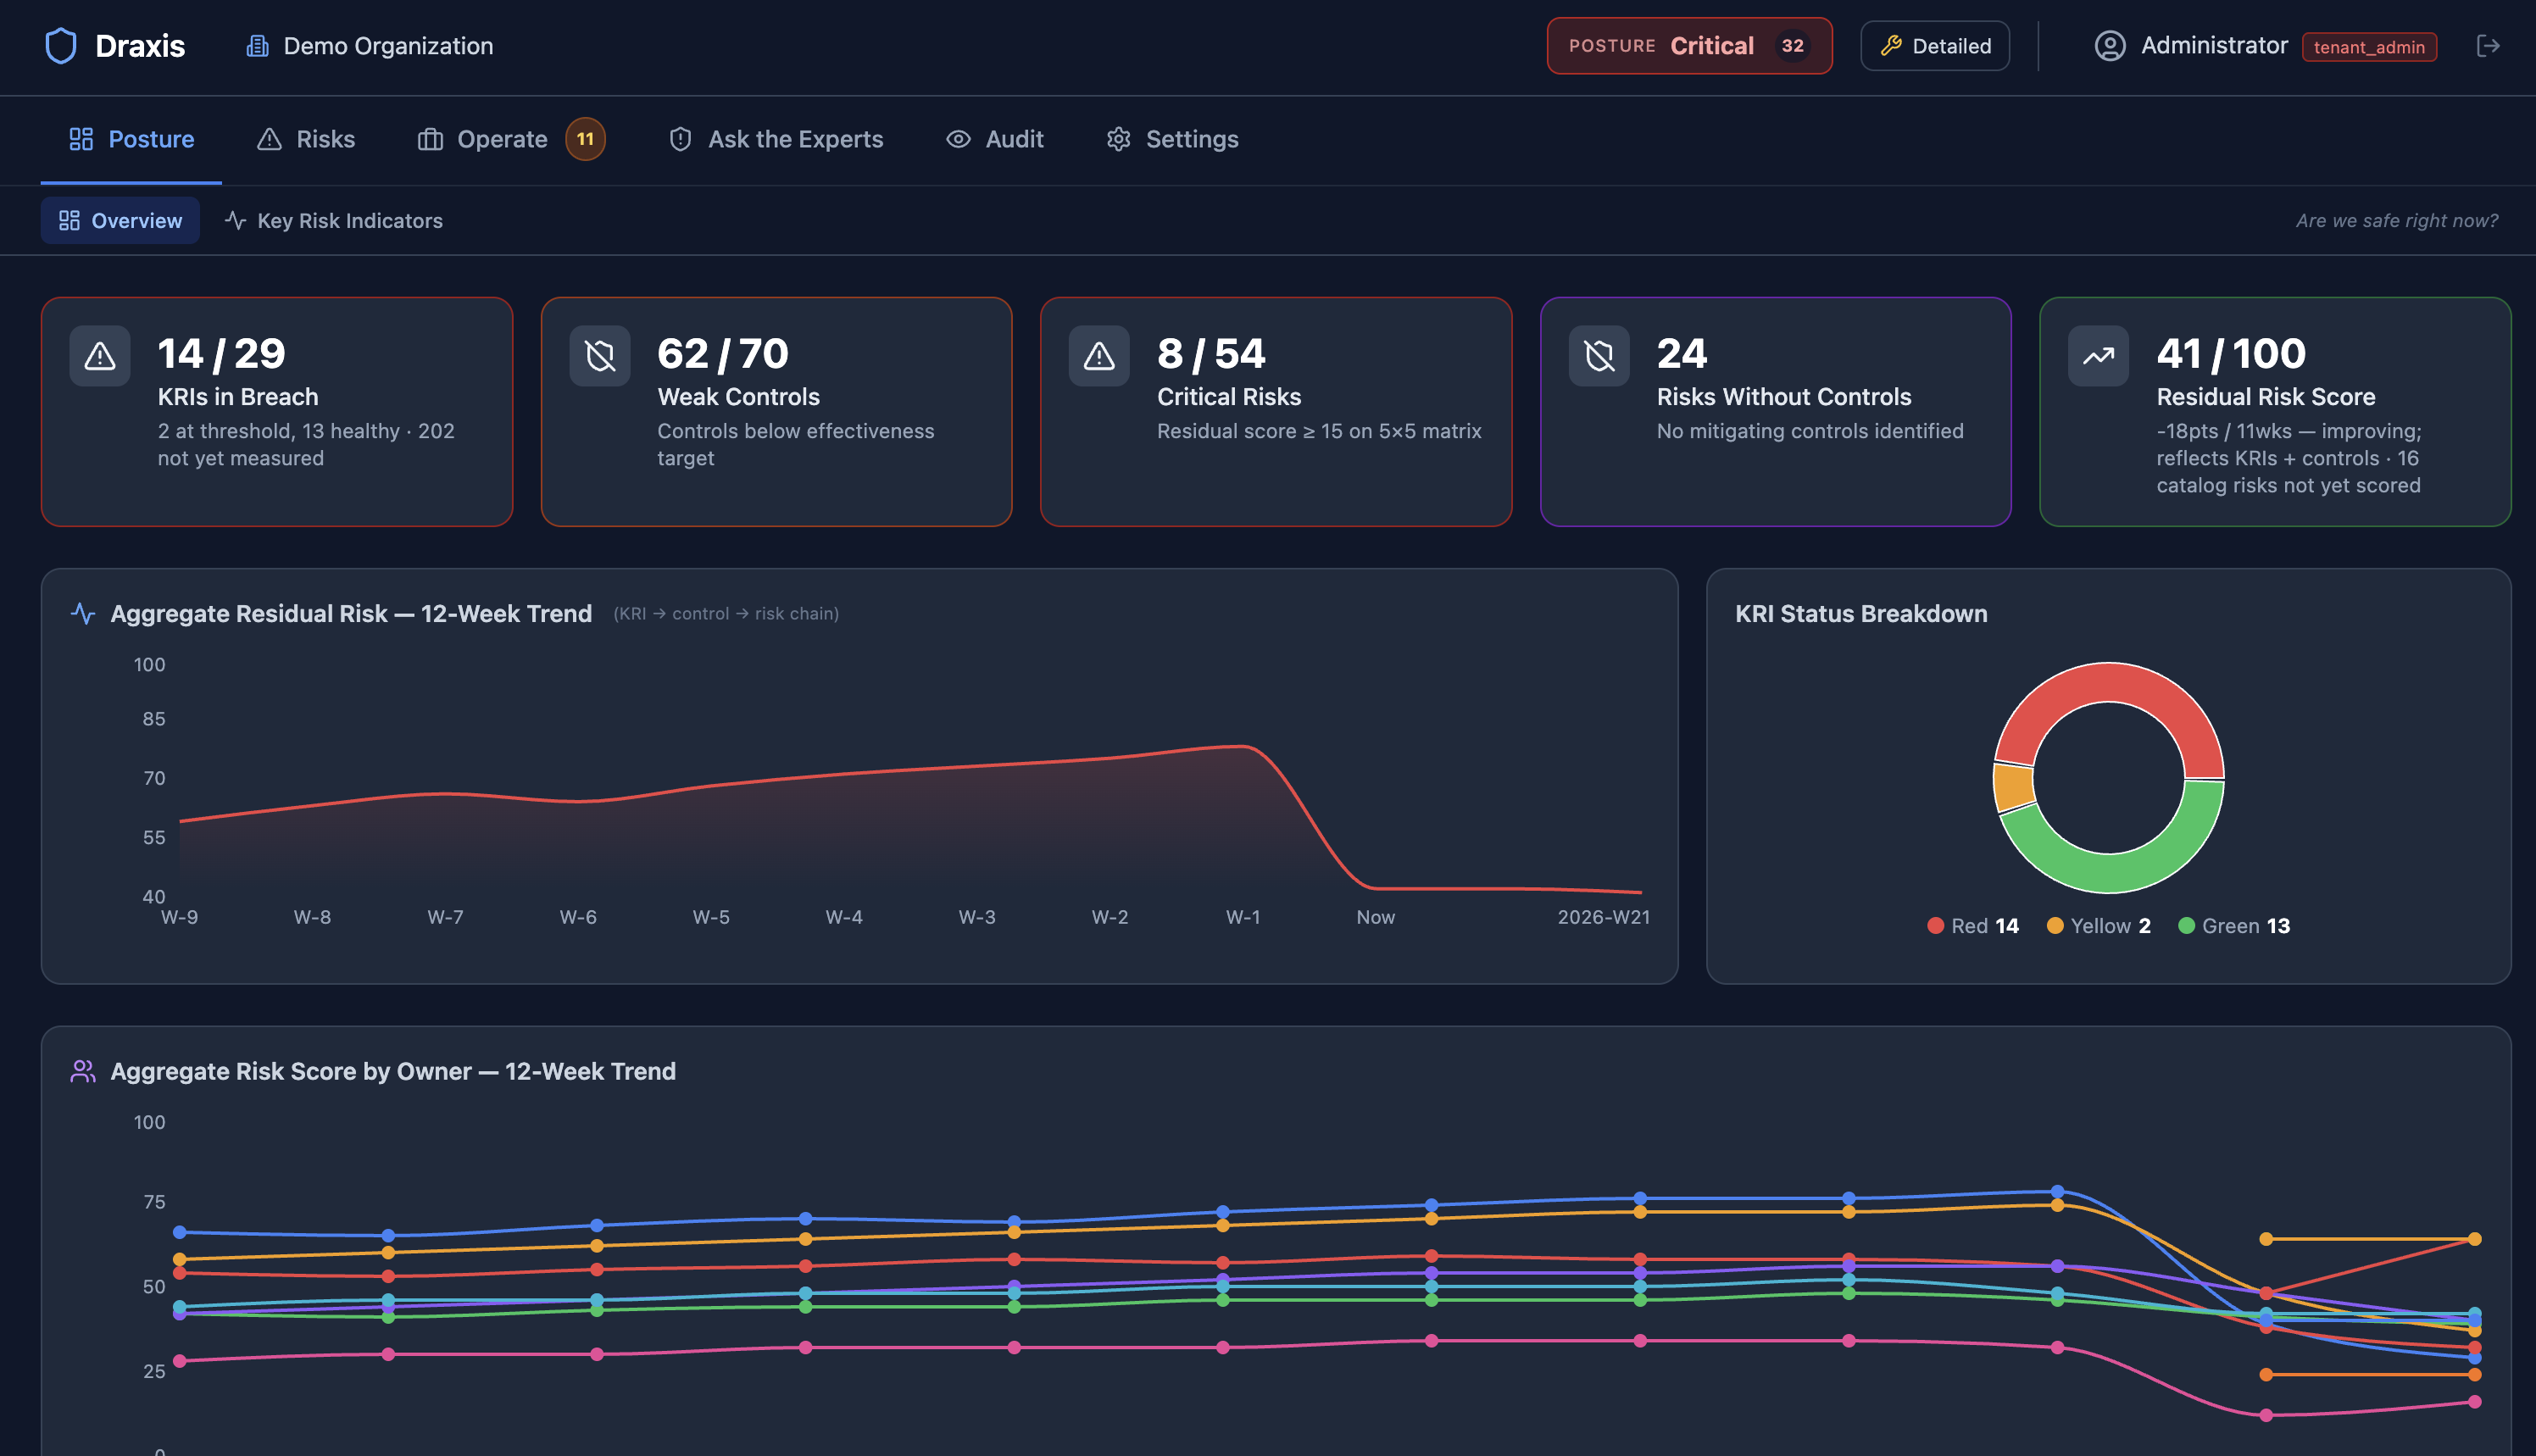
What AI does: ingests your stack continuously, runs the loss simulations, surfaces what is drifting before someone has to ask, and pulls in AI specialists in Privacy, TPRM, and Cyber Insurance on demand. Your CISO operates with a live picture instead of a quarterly snapshot, and gets the audit, regulator, and stakeholder drafts as a downstream byproduct. Detailed mode exposes the full Risk Register, KRI Board, Loss Scenarios, and Inbox.
Your security advisory function until you hire
The problem: most growth-stage and mid-market companies aren’t ready for a full-time CISO hire. They still need someone watching the environment, calling out drift, and owning the answer when an auditor, regulator, or insurer asks.
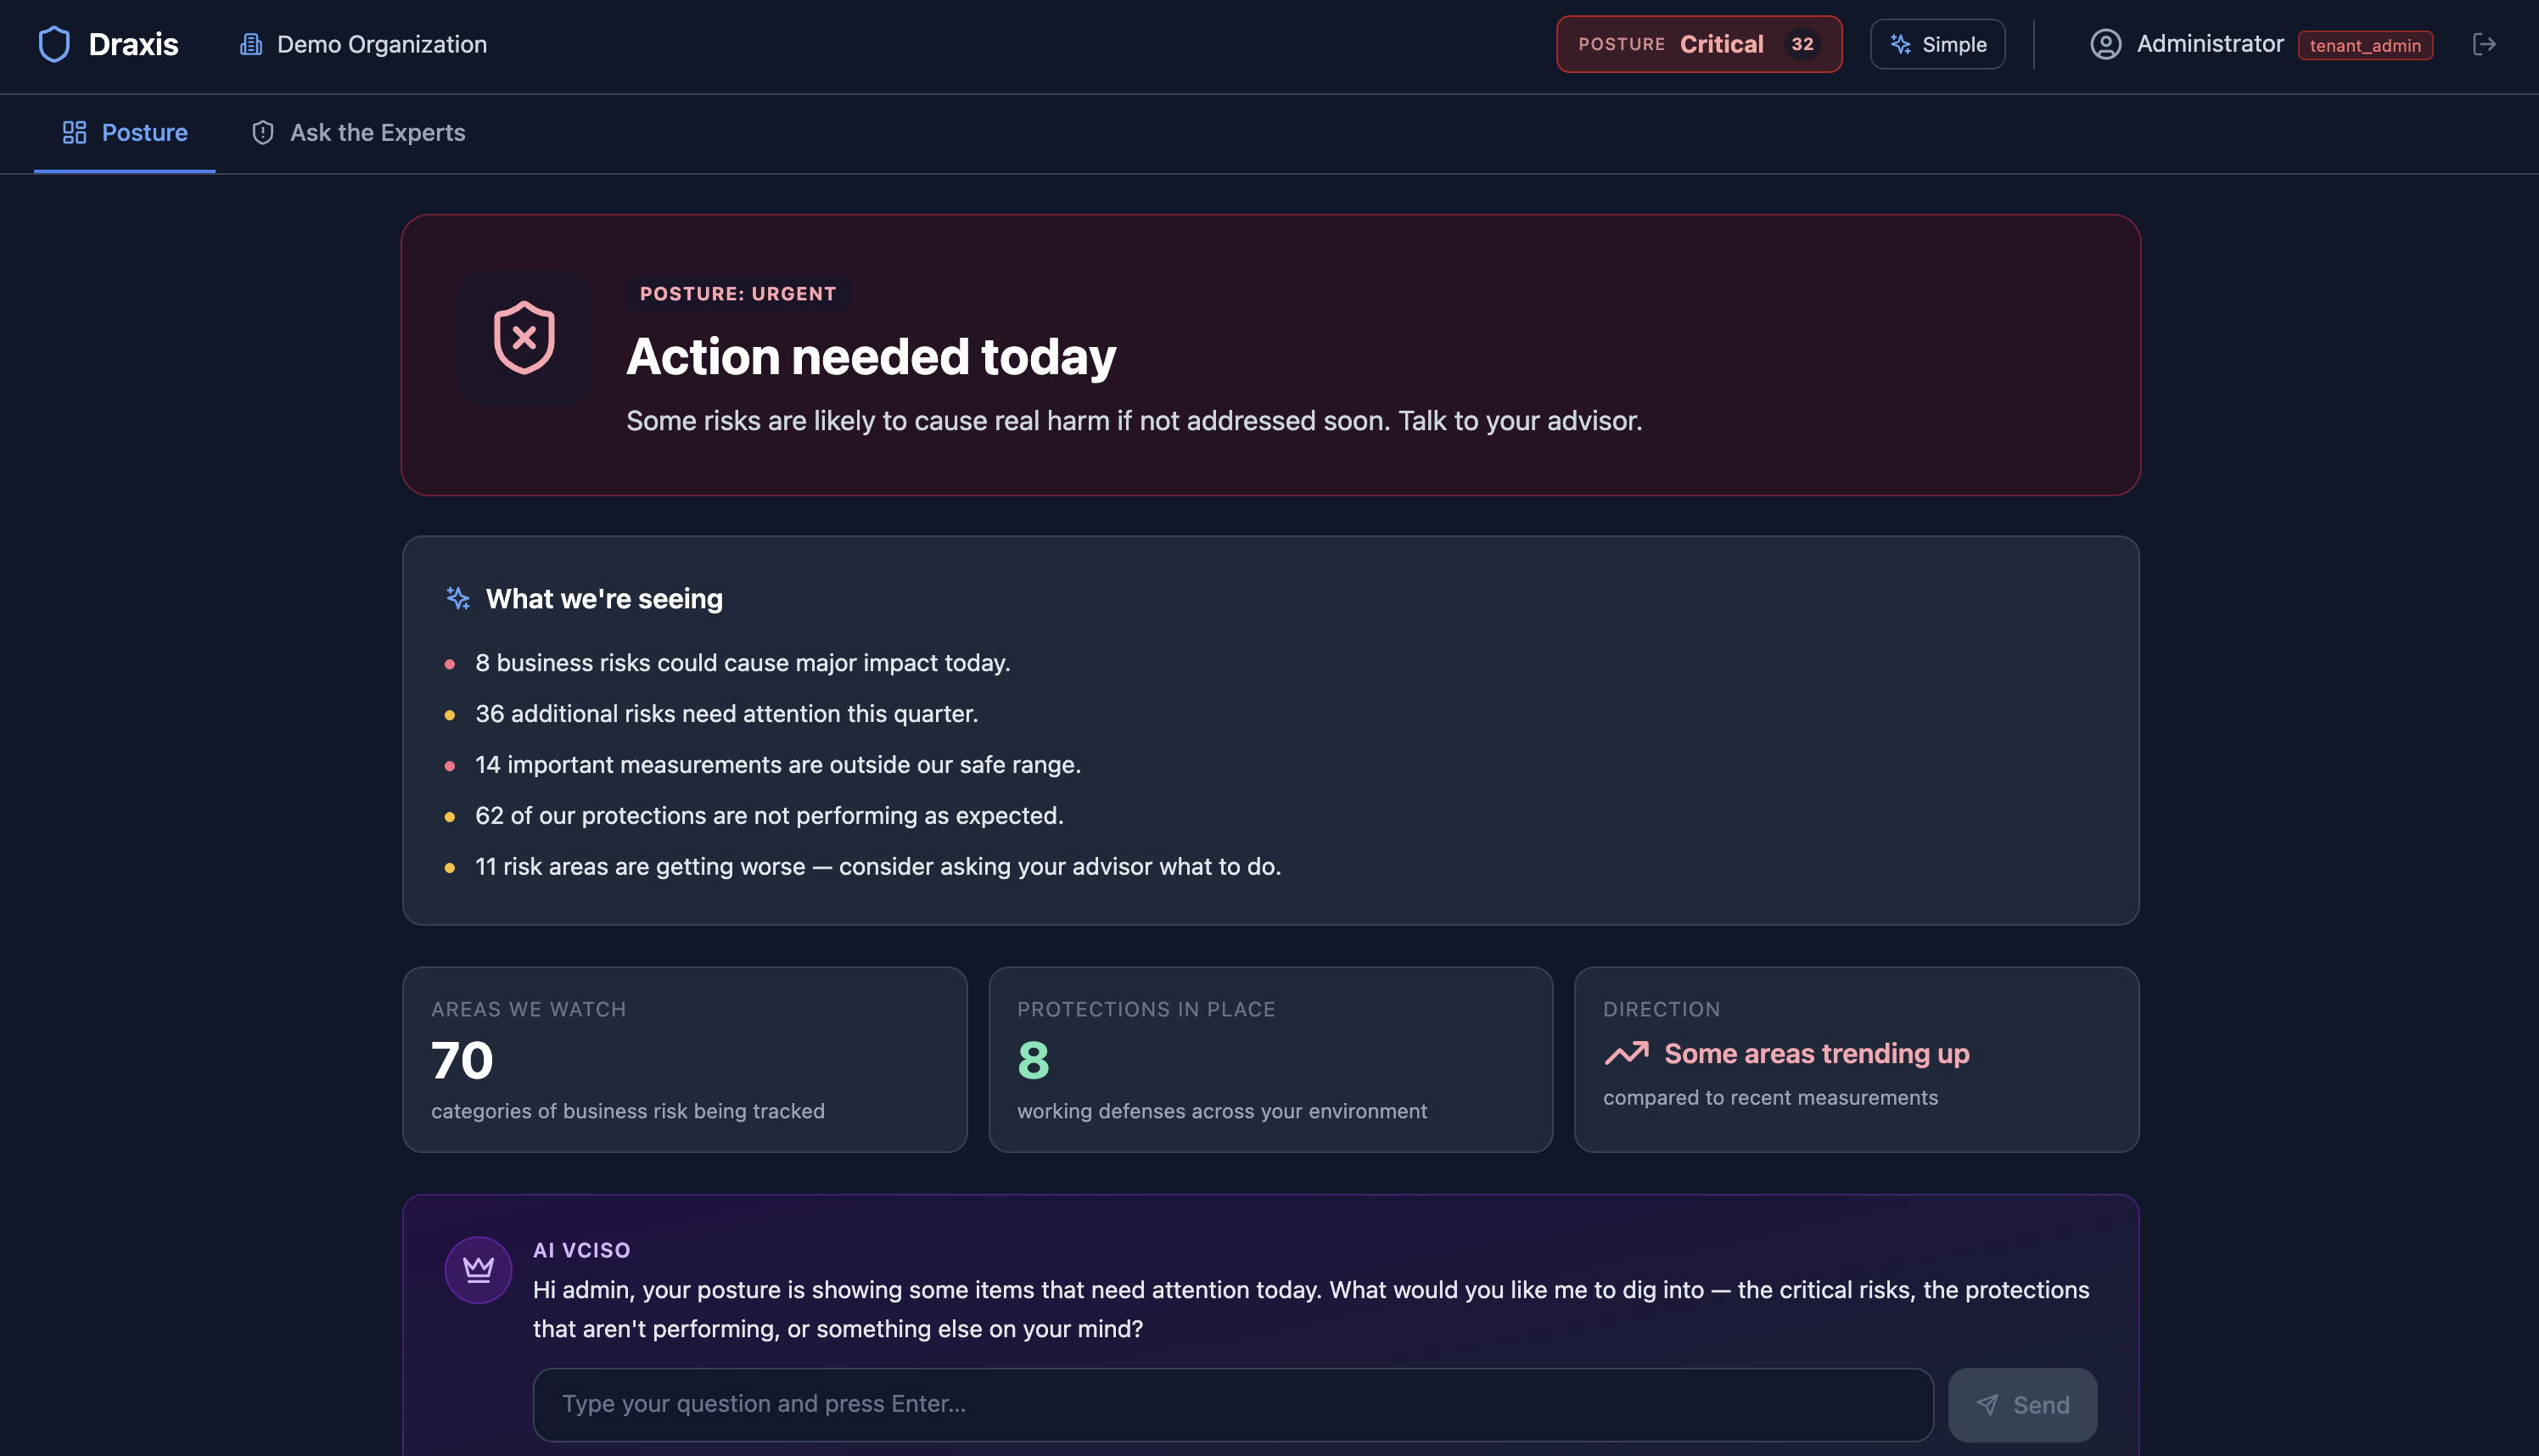
What AI does: the AI Security Advisor covers your security advisory function until you hire: continuous monitoring of your actual stack, investment guidance grounded in your real exposure, and the experienced perspective of a seasoned operator. Simple mode shows your CFO a single GOOD / WATCH / URGENT screen and an “Ask the Advisor” panel. No jargon, no KRI, no MITRE, no CVE acronyms.
The Advisor-led AI expert panel
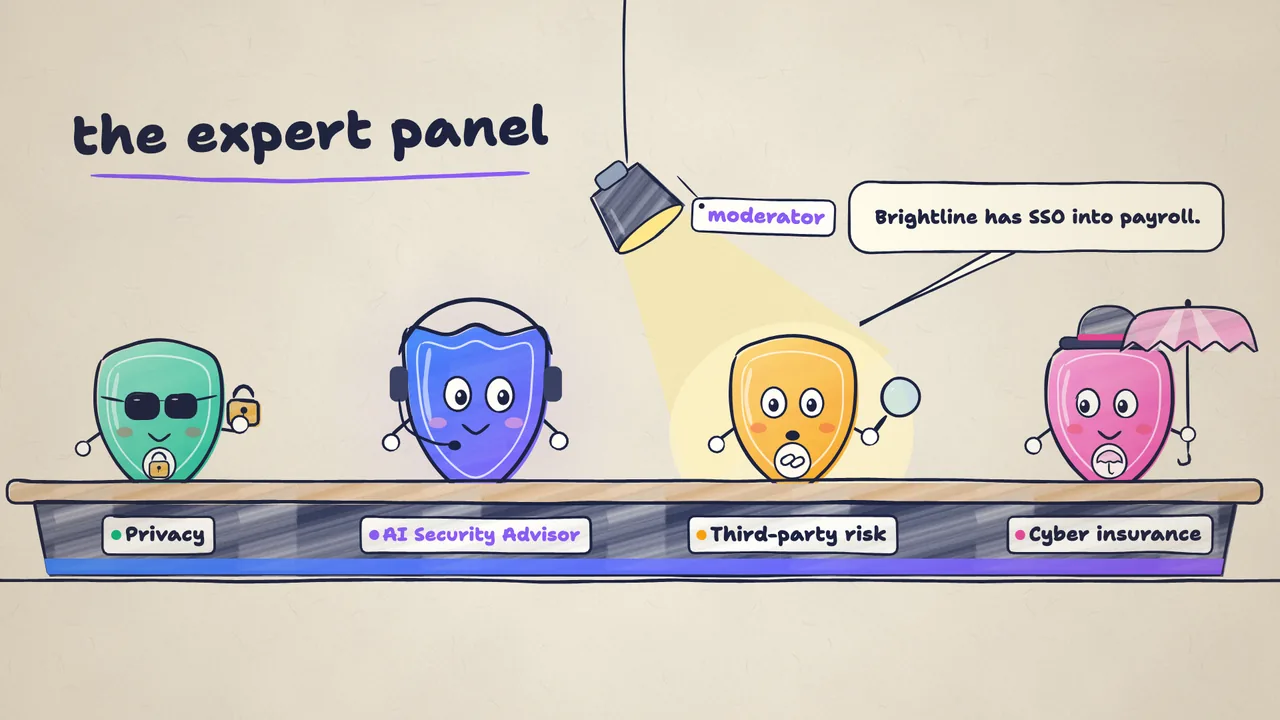
You only ever talk to the Advisor. It brings in the right specialist for you.
The signal, the trend, and the early warning are the engine. The AI Security Advisor and expert panel are how you act on them. Cyber risk decisions touch privacy law, third-party risk, and insurance, and few CISOs are deep in all three. The Advisor opens every conversation, grounds it in your live posture and your early-warning history, and routes you to the specialist who can answer. You never have to know who to ask.
The CISO voice that knows your environment
- Solves: “our CISO has no time to keep up with what just changed in our stack”, or “we don’t have a CISO at all”
- Continuous risk-posture briefings tied to financial loss potential, refreshed as your stack changes
- Drafts strategy memos, investment cases, trend deltas, and yes board readouts when those are needed
- Per-stakeholder memory: CFO answers and CISO answers diverge by framing, grounded in the same evidence
The privacy counsel you didn’t hire
- Solves: SEC Cyber Rules, DORA, NIS2, GDPR, CCPA, HIPAA, NYDFS. Nobody on staff owns all of it.
- Maps your live posture to what each regulator requires
- Drafts regulator-shaped breach notifications from real evidence
- Stays current as regulations change. No code release needed.
Vendor risk from your stack, not questionnaires
- Solves: “our vendor questionnaires are self-attestation theater”
- Vendor concentration risk, supply-chain gaps, and fourth-party exposure, derived from your existing stack
- Detects drift between what a vendor attests and what your telemetry shows
- Tailored for the CRO and the security lead who own vendor risk
Turns posture into premium leverage
- Solves: “our renewal questionnaire is a guess and our premium reflects that”
- Maps loss scenarios to your actual policy language
- Surfaces control gaps that move underwriting outcomes
- Drafts the renewal narrative your broker can put in front of the carrier
AI across the platform
Every painful step in a risk program. AI does the lifting.
Each surface below replaces a specific manual job that used to need an analyst, a consultant, or a quarter you didn’t have. Together they cover what a real cyber risk program does, end to end: ingestion, scoring, simulation, and reporting.
Tools without a connector still land risk signal.
- Solves: long-tail tools with no native integration go invisible to your risk program
- Drag a PDF, paste a CSV, push a webhook. AI extracts typed Key Risk Indicators against the catalog.
- Pentest reports, vendor SOC 2s, audit notes, log snapshots, config exports, screenshots
- Every value cites its source span. High-confidence extractions auto-accept, the rest queue for review.
Connect a new tool. Your Risk Register populates itself.
- Solves: “I plugged in EDR and the Controls list is still empty”
- When you add an integration, AI fills the catalog gaps (signals → safeguards → controls → ATT&CK techniques) within seconds
- Your Risk Register’s Controls list goes from empty to populated in 5–15 seconds, not weeks of analyst configuration
- Low-confidence proposals queue in the Inbox so analysts review instead of author from scratch
No more default 3×3 heat map.
- Solves: a brand-new tenant where every catalog risk sits at the default until an analyst configures all 42
- At onboarding and on every connector save, AI proposes per-tenant likelihood and impact based on your industry, headcount, KRI mix, and control density
- High-confidence scores apply automatically. The rest queue with reasoning for your analyst to tweak in seconds.
- AI never overwrites a human-set value. Provenance is tracked per score.
You see the risk. AI tells you what to install.
- Solves: “I see this risk on the heat map. I have no idea what control would actually move it.”
- For every catalog risk, AI surfaces the CIS Controls v8 safeguards that should govern it, not only the ones wired today
- Names the connectors and signals that would measure each one (e.g. Require MFA for Admin Access · measured by Okta, Entra, Google Workspace)
- One-click path: I see the risk → I know what should govern it → I know what to install
Quantify scenarios in dollars, not vibes.
Once Draxis has caught the drift, the simulation engine tells you what it’s worth.
- Solves: “we have no idea what a ransomware event would actually cost us, in dollars, given our real asset and identity inventory”
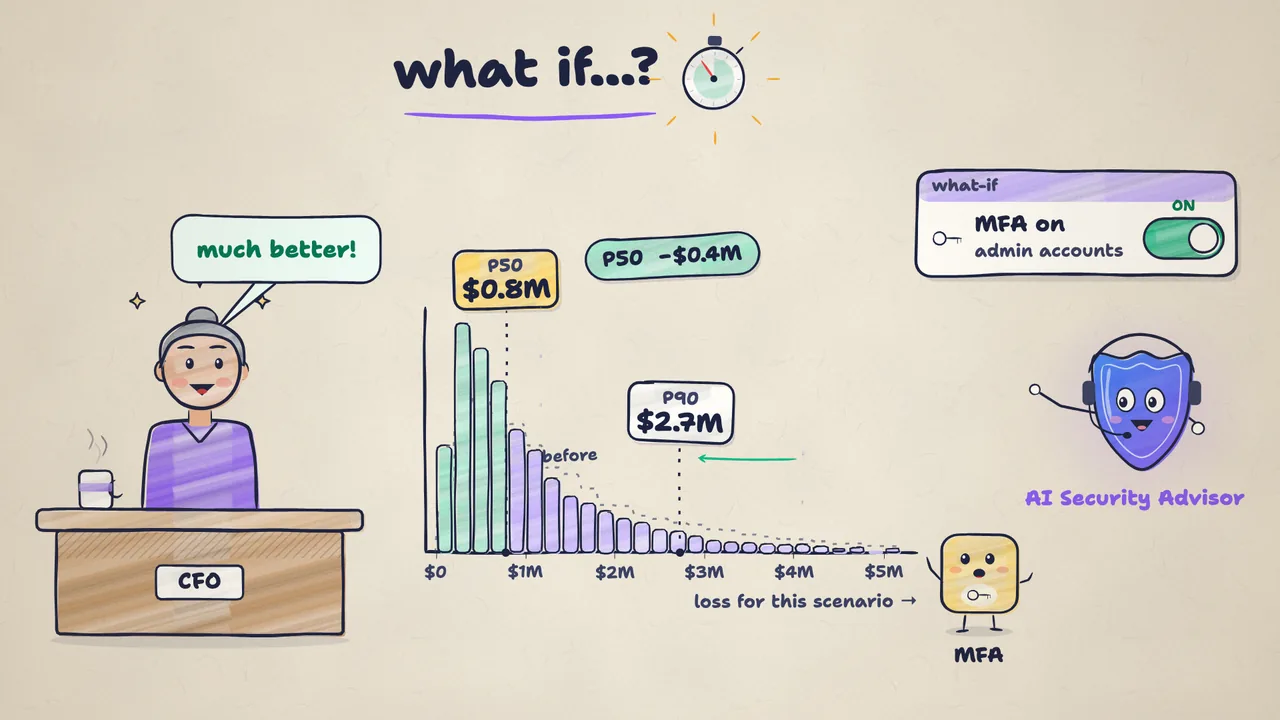
- Monte Carlo loss scenarios grounded in your real asset, identity, and data inventory, with P10 / P50 / P90 outputs
- Multi-step attack chains, blast-radius graphs, toxic-combination detection
- Counterfactuals: “what if we added MFA on this asset class?” runs instantly with the dollar delta
- Regulatory fines modeled directly (GDPR, CCPA, HIPAA, PCI-DSS, state breach laws)
Your risk catalog stays current automatically.
- Solves: “new threats land every day; my risk register is from last year”
- Daily threat-intel sweep (CISA KEV today; ENISA + MITRE ATT&CK on roadmap) plus tenant-drift detection
- AI proposes catalog additions, applicability filtering keeps narrow CVEs out of your queue
- Approved updates ship to every tenant on next sync, so you inherit the catalog work everyone else triggered
Universal AI integration
Universal AI integration. Every direction.
Draxis connects to your stack three ways, and all three are universal. It reads from your tools, it answers from any AI client, and the rest lands through the Drop Zone.
Ingest from any MCP-enabled tool
Draxis ingests from any tool that exposes an MCP server. As more tools adopt MCP, every new one becomes a native integration automatically. No custom connector to build.
Universal fallback, any tool, any format
For everything without a connector yet, the REST API and the AI Drop Zone take whatever you have. Paste a CSV, upload a log, POST a webhook, and AI extracts the signal.
Query Draxis from any LLM client
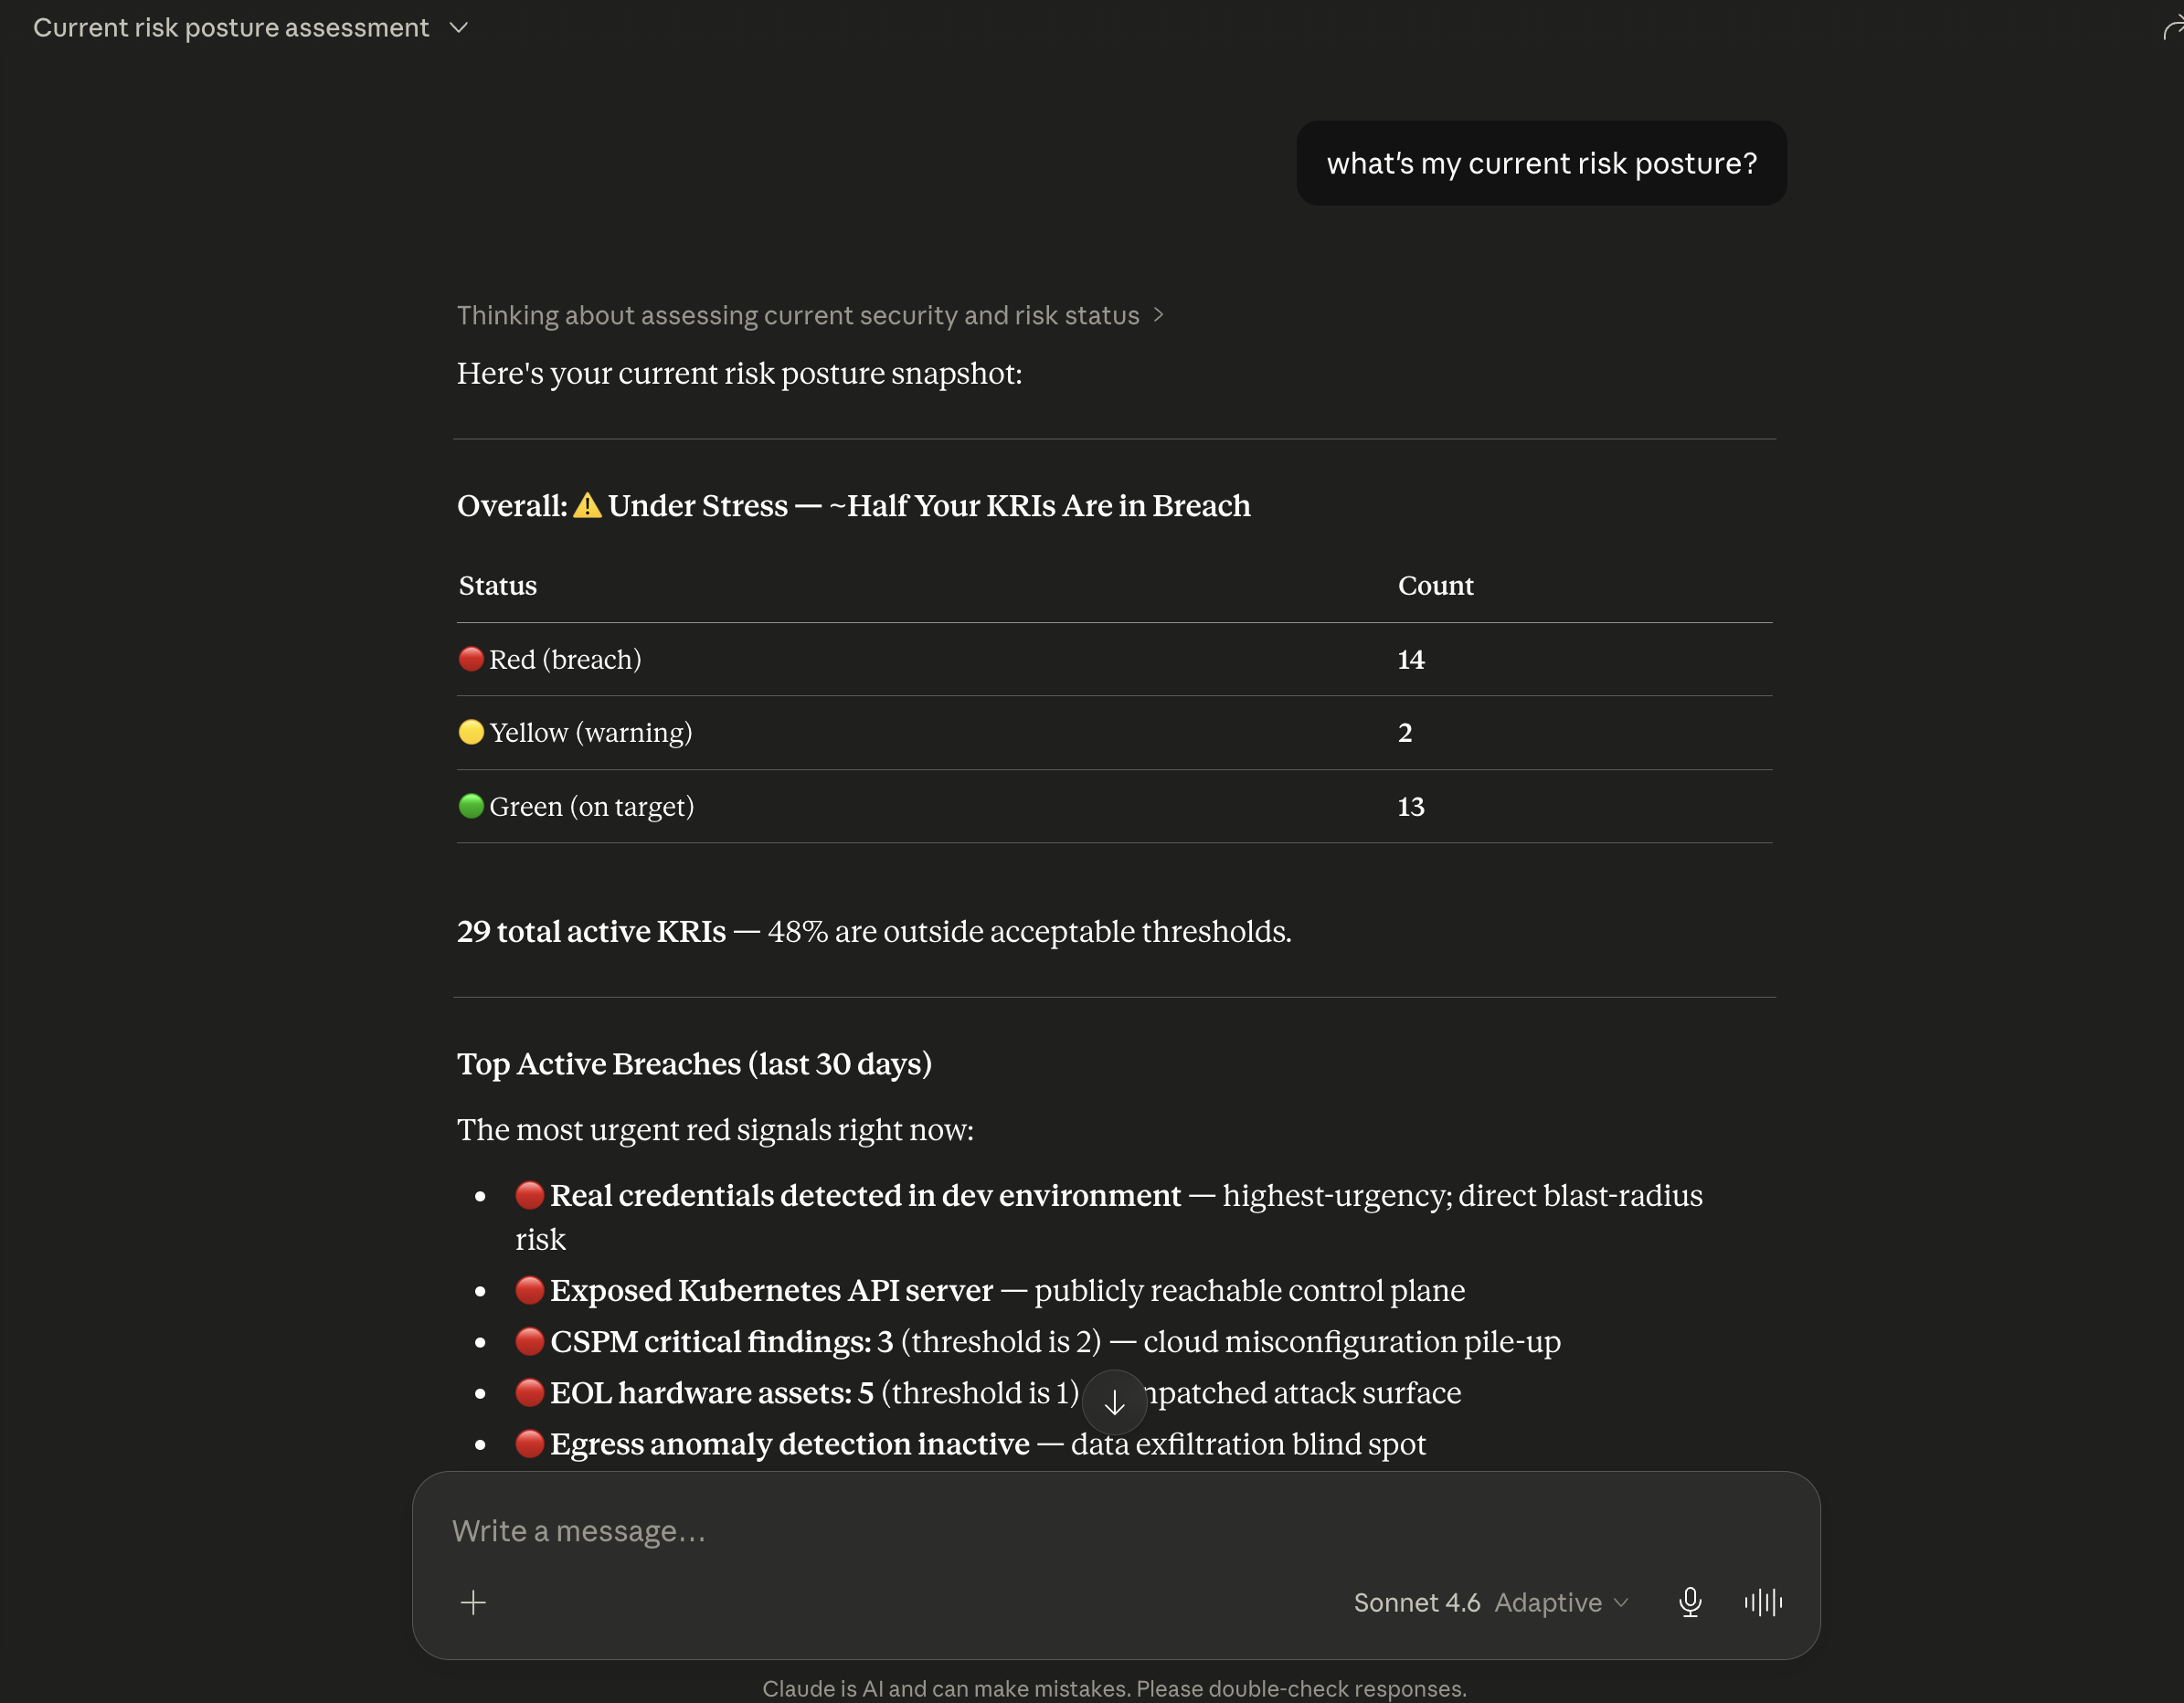
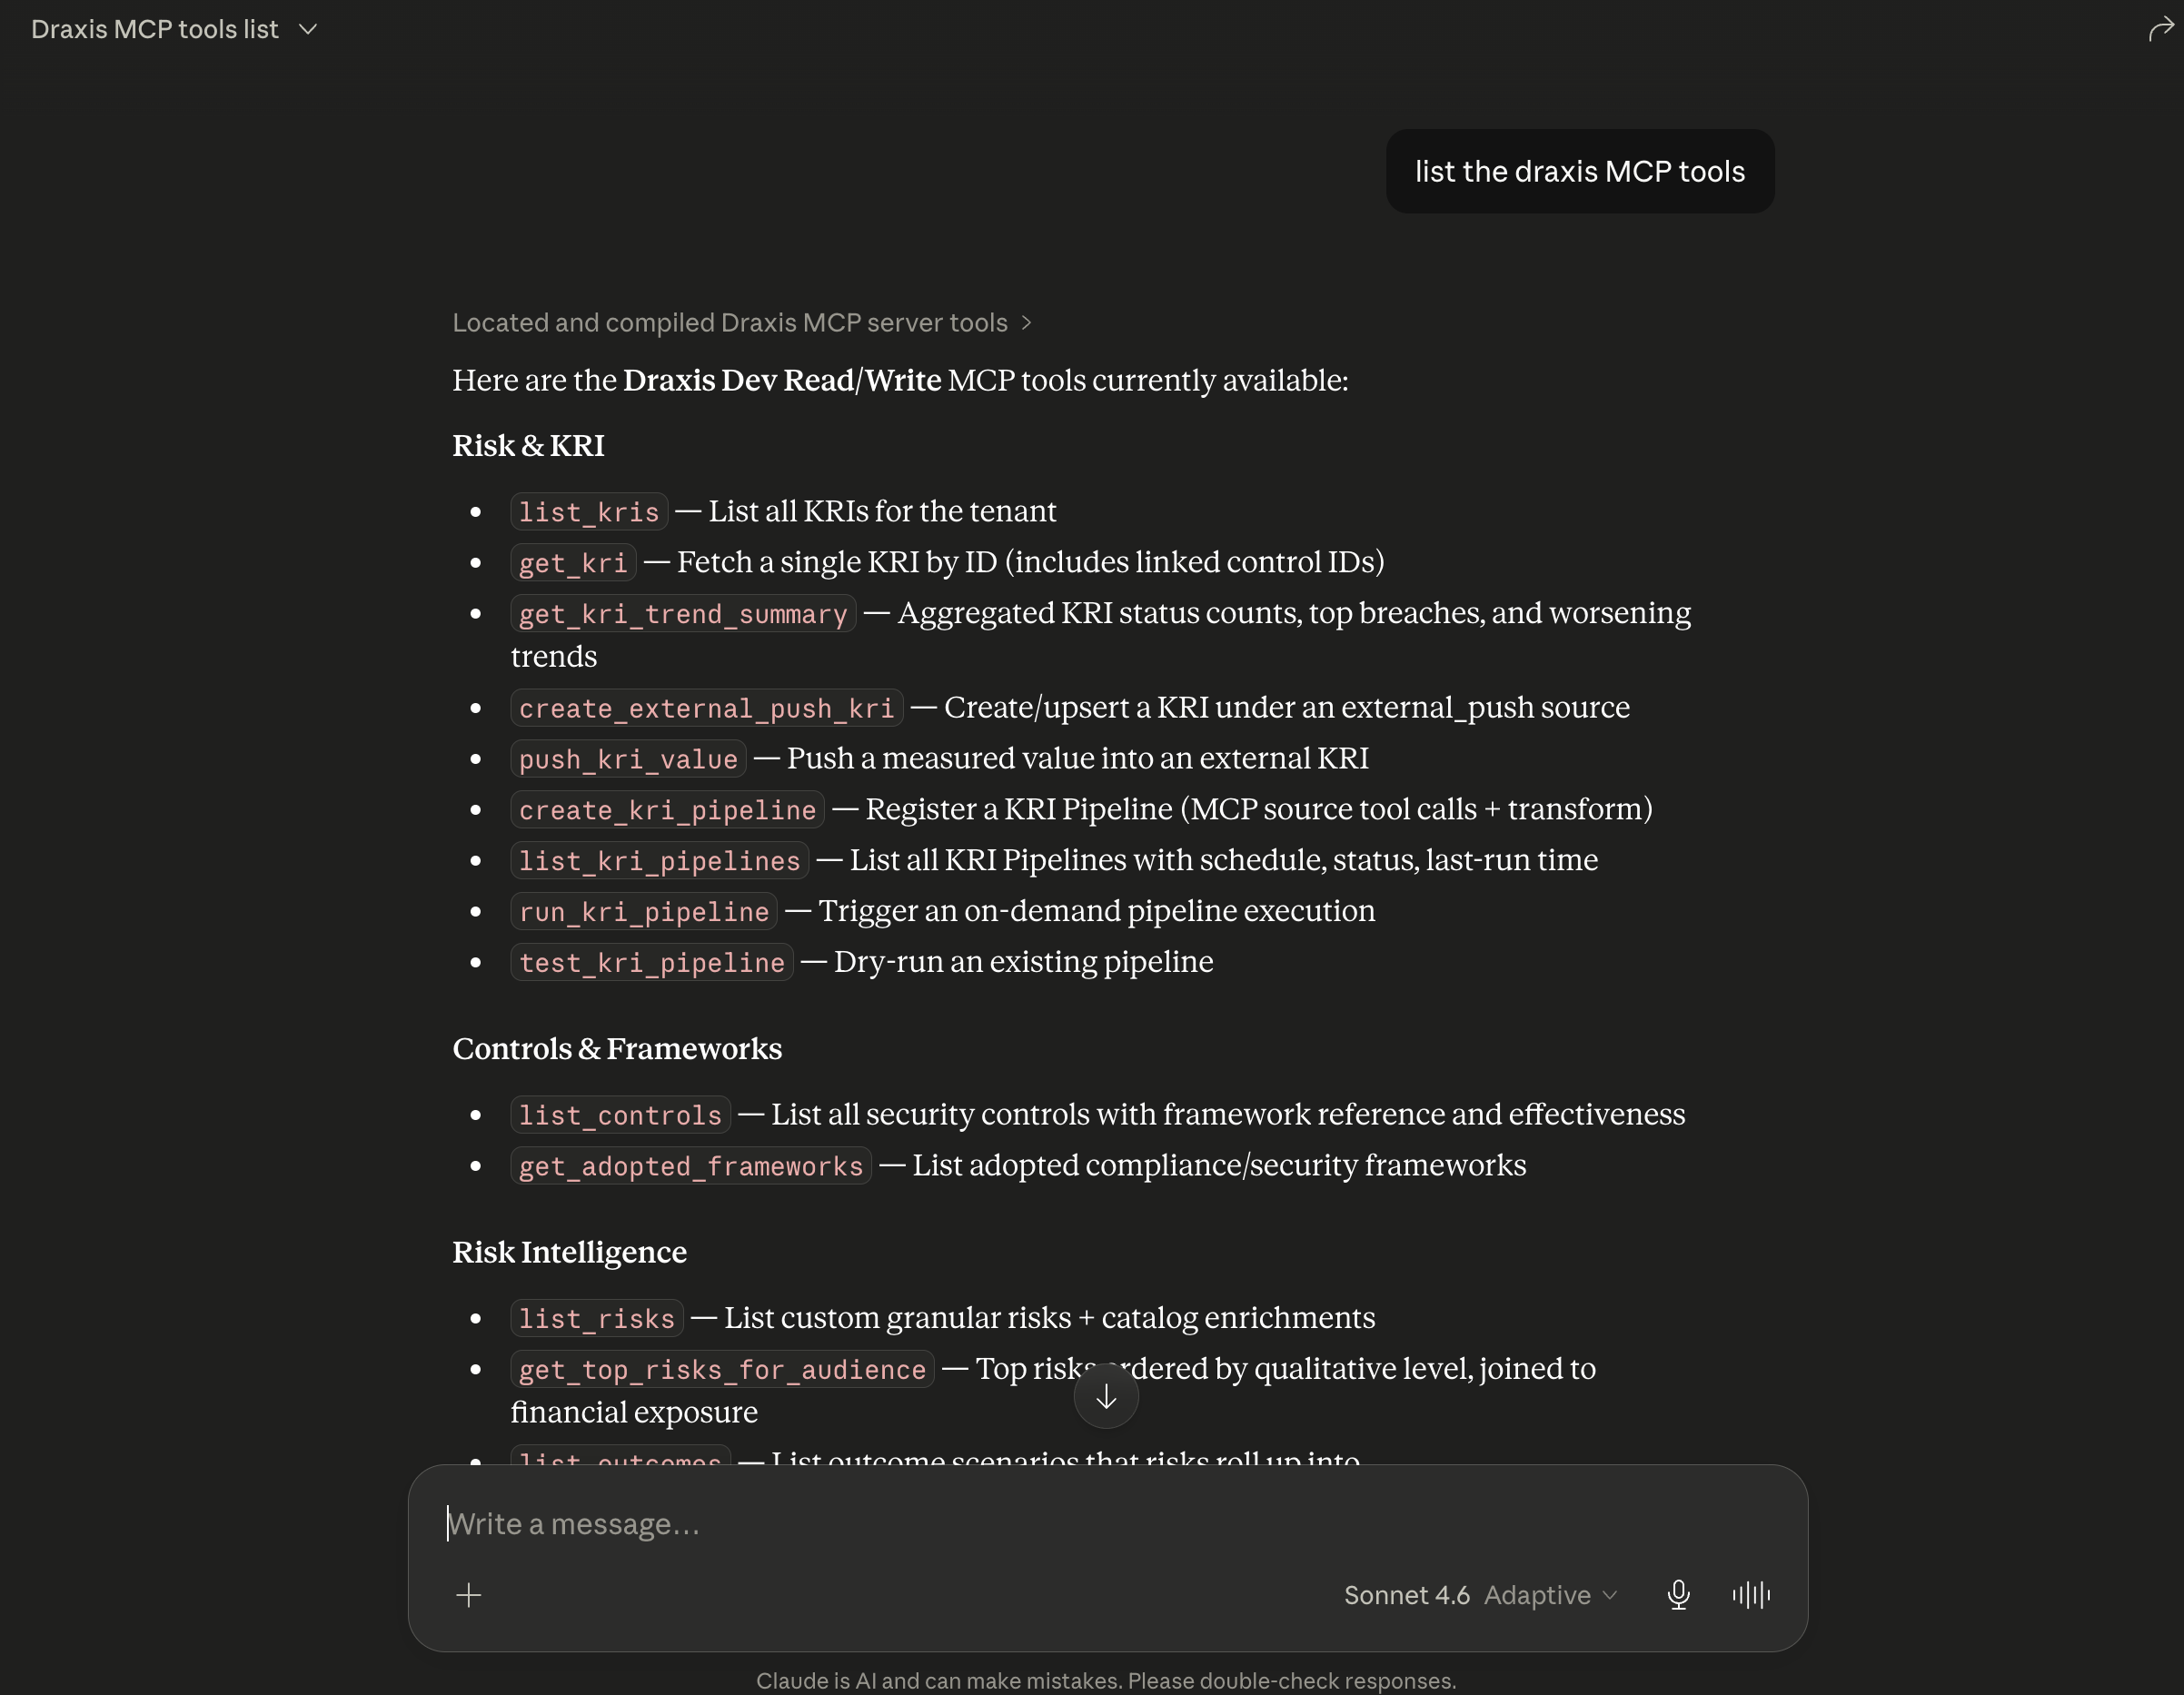
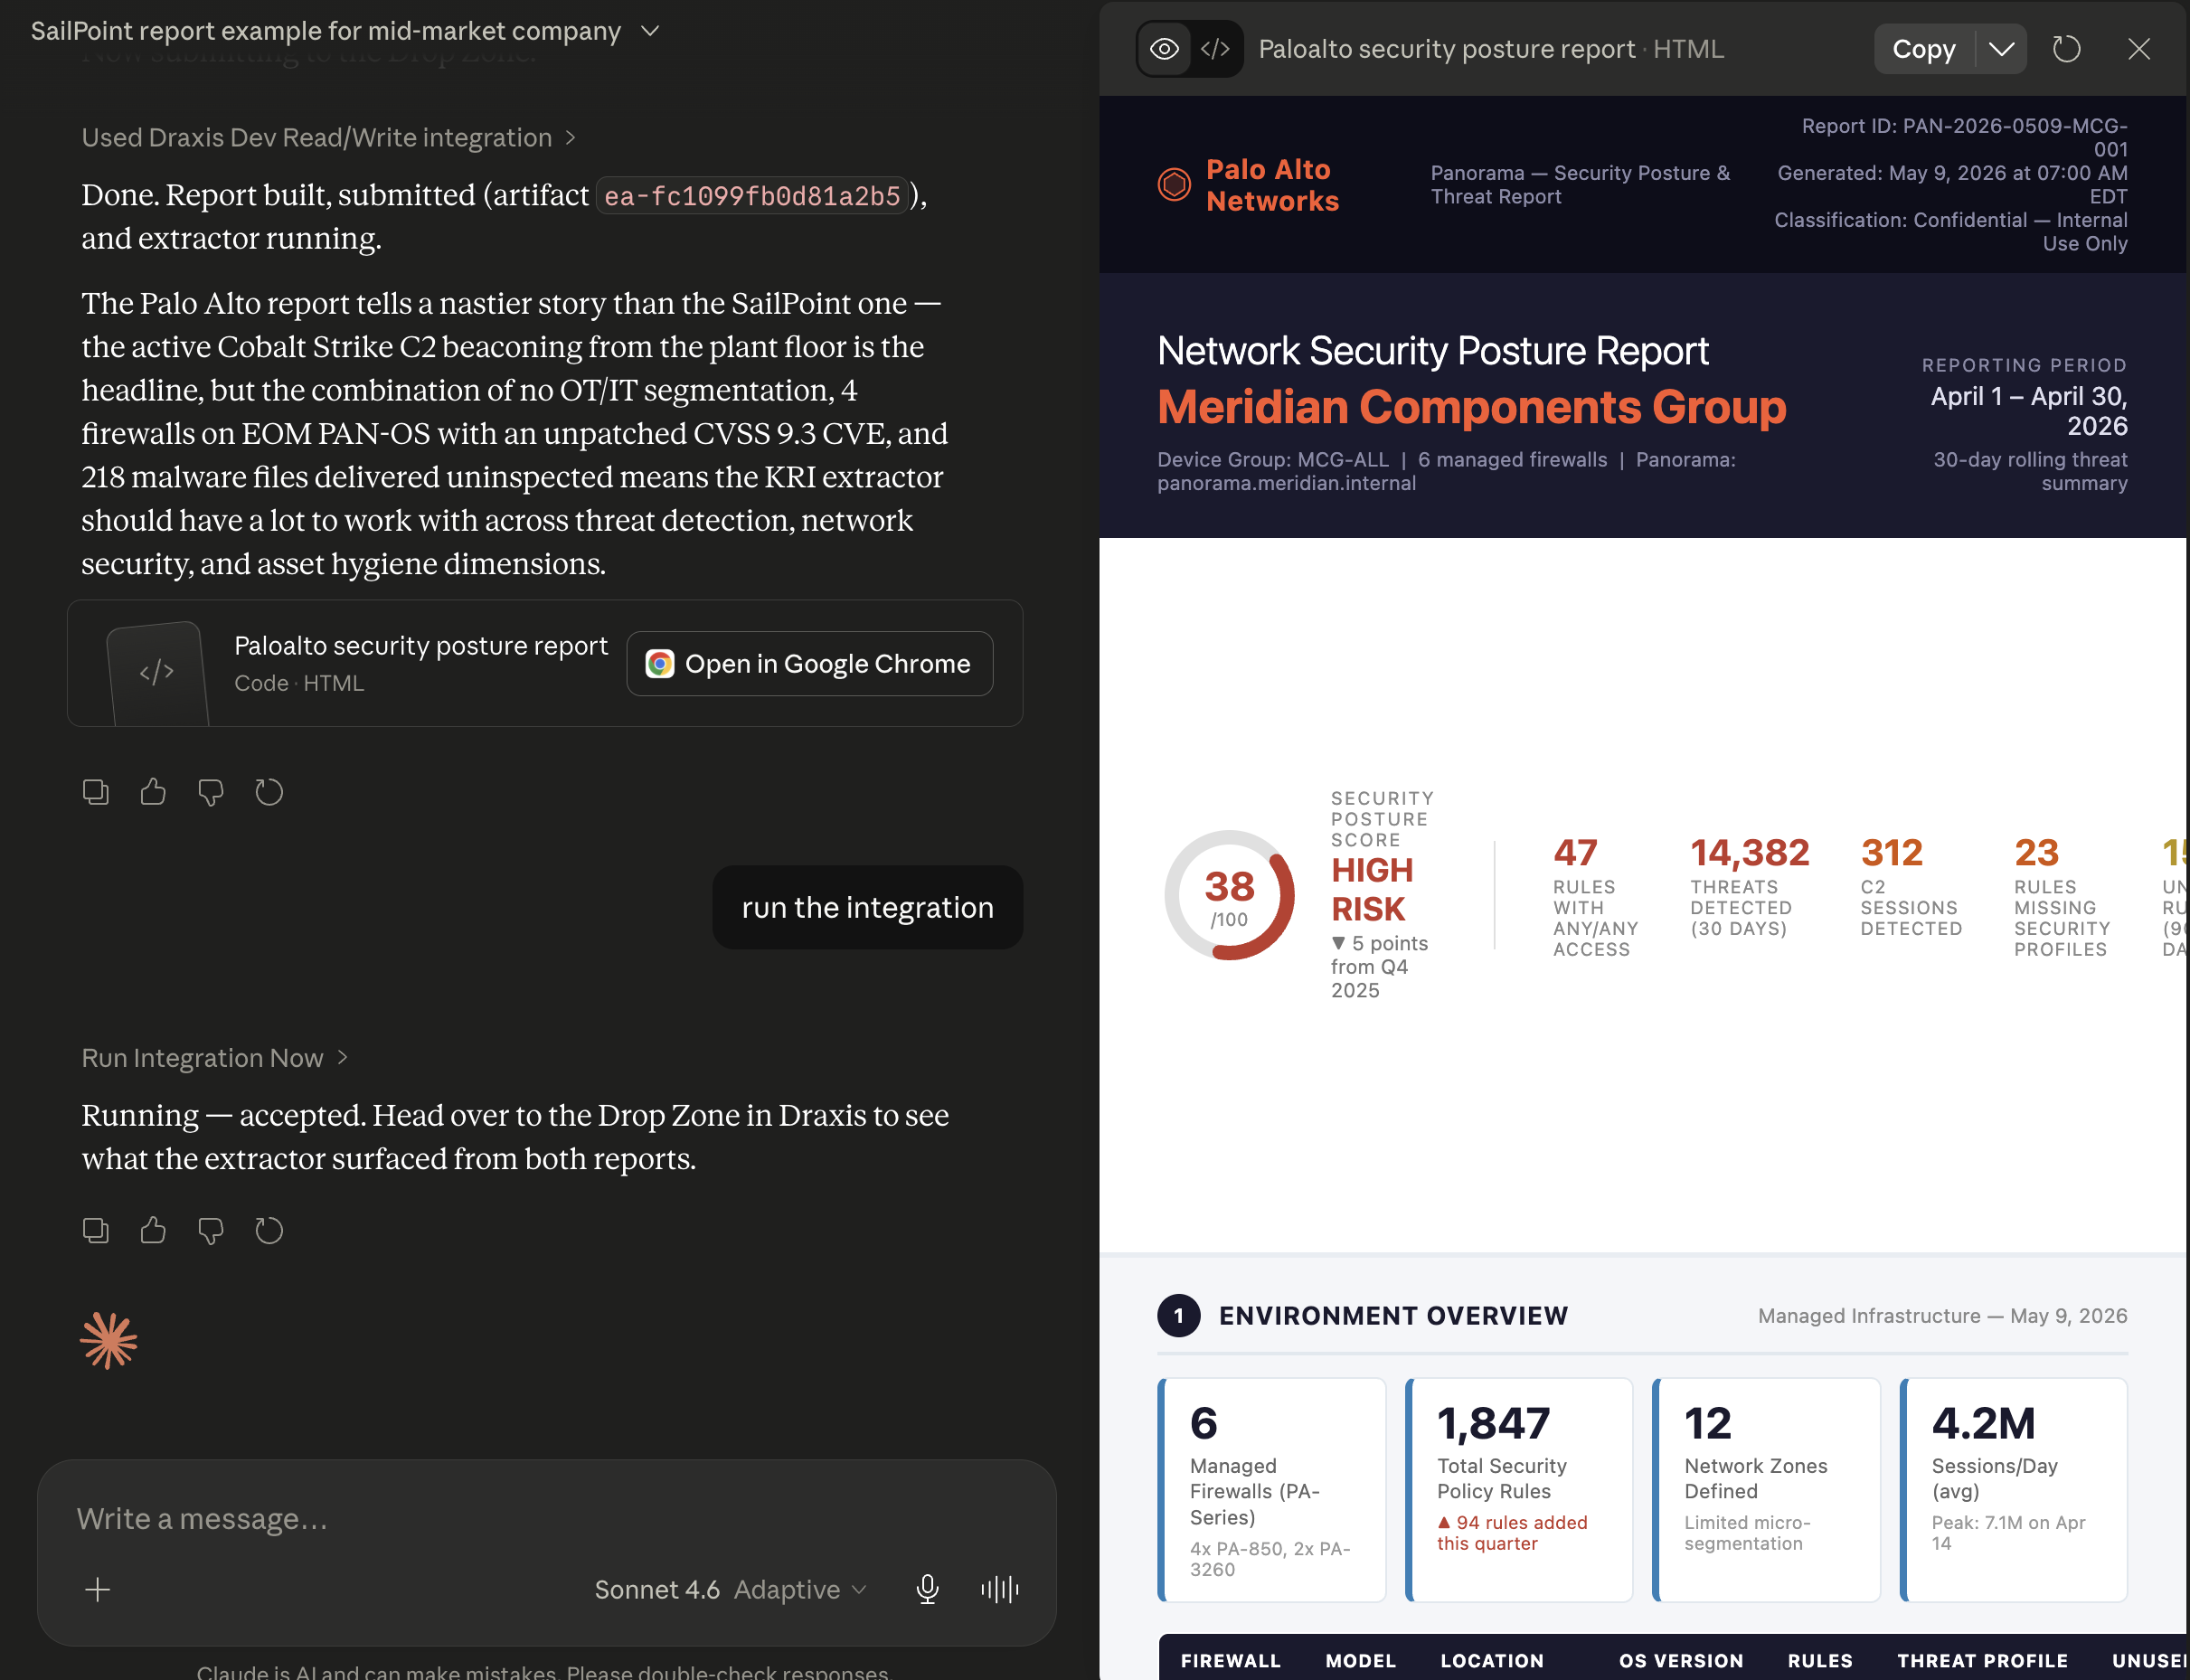
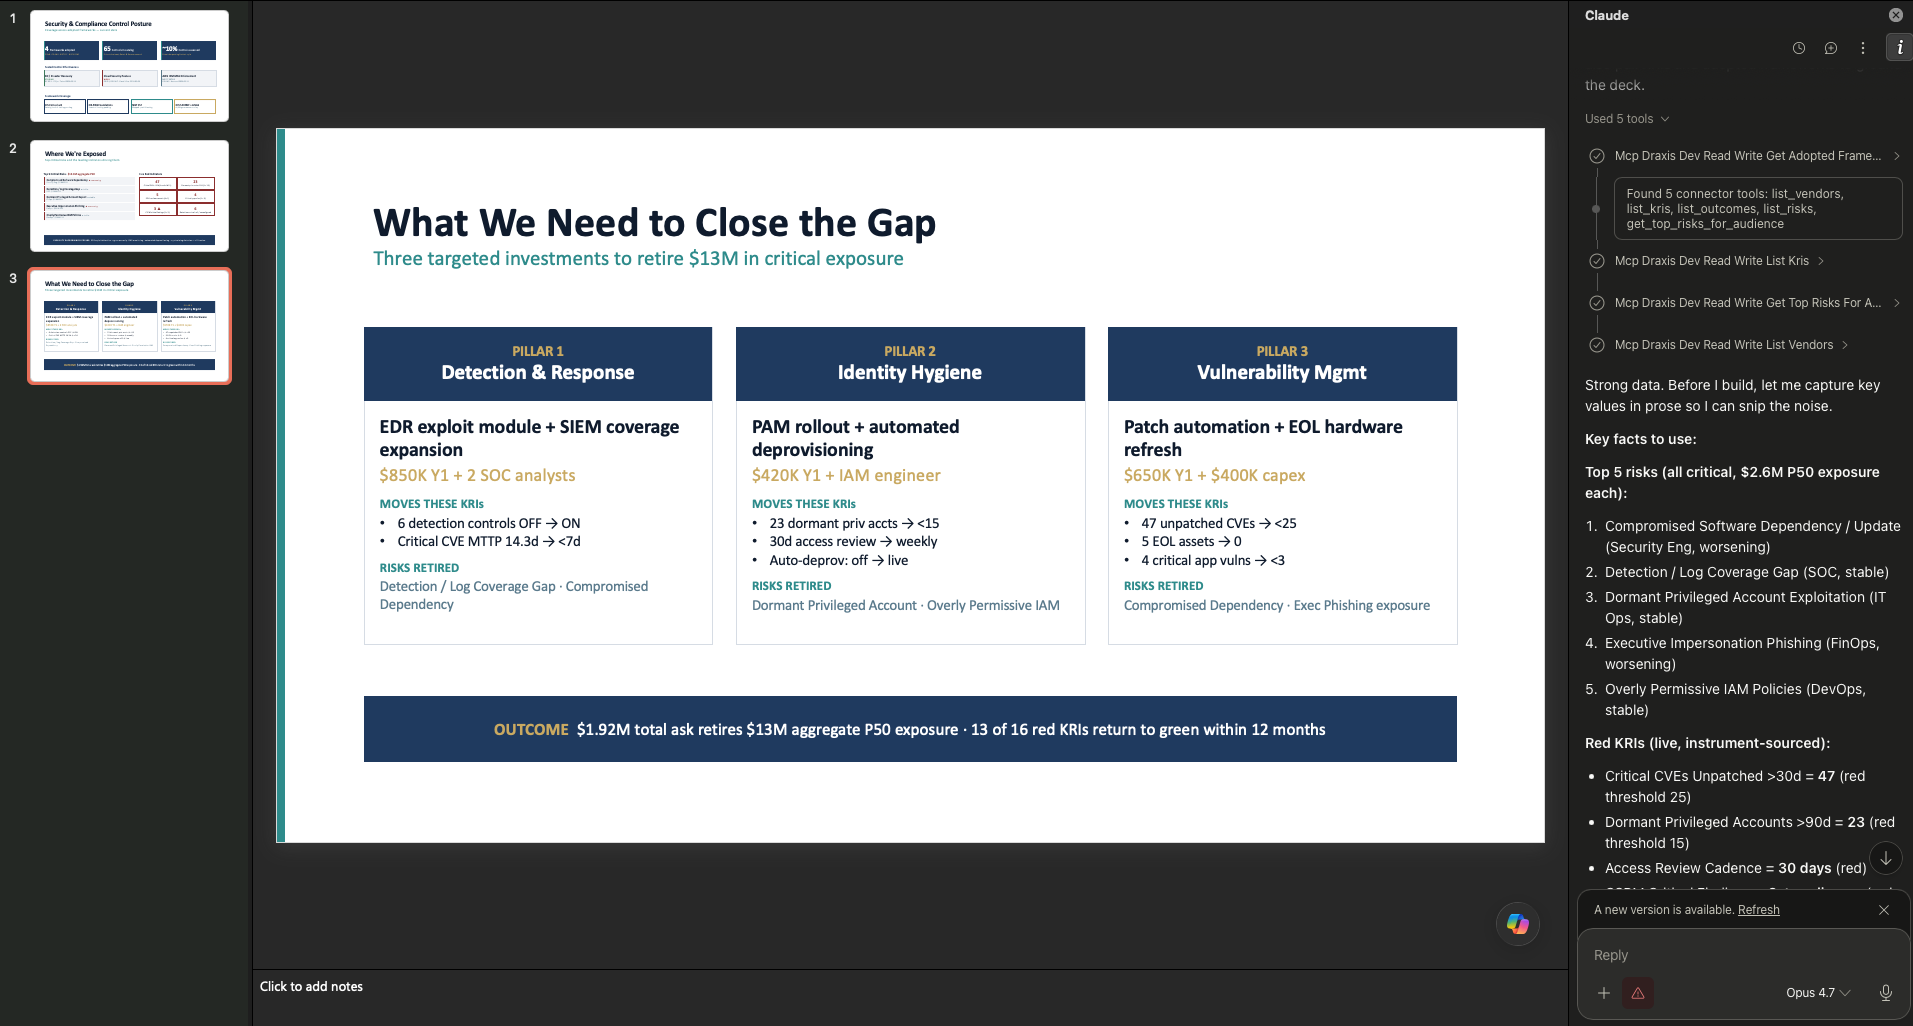
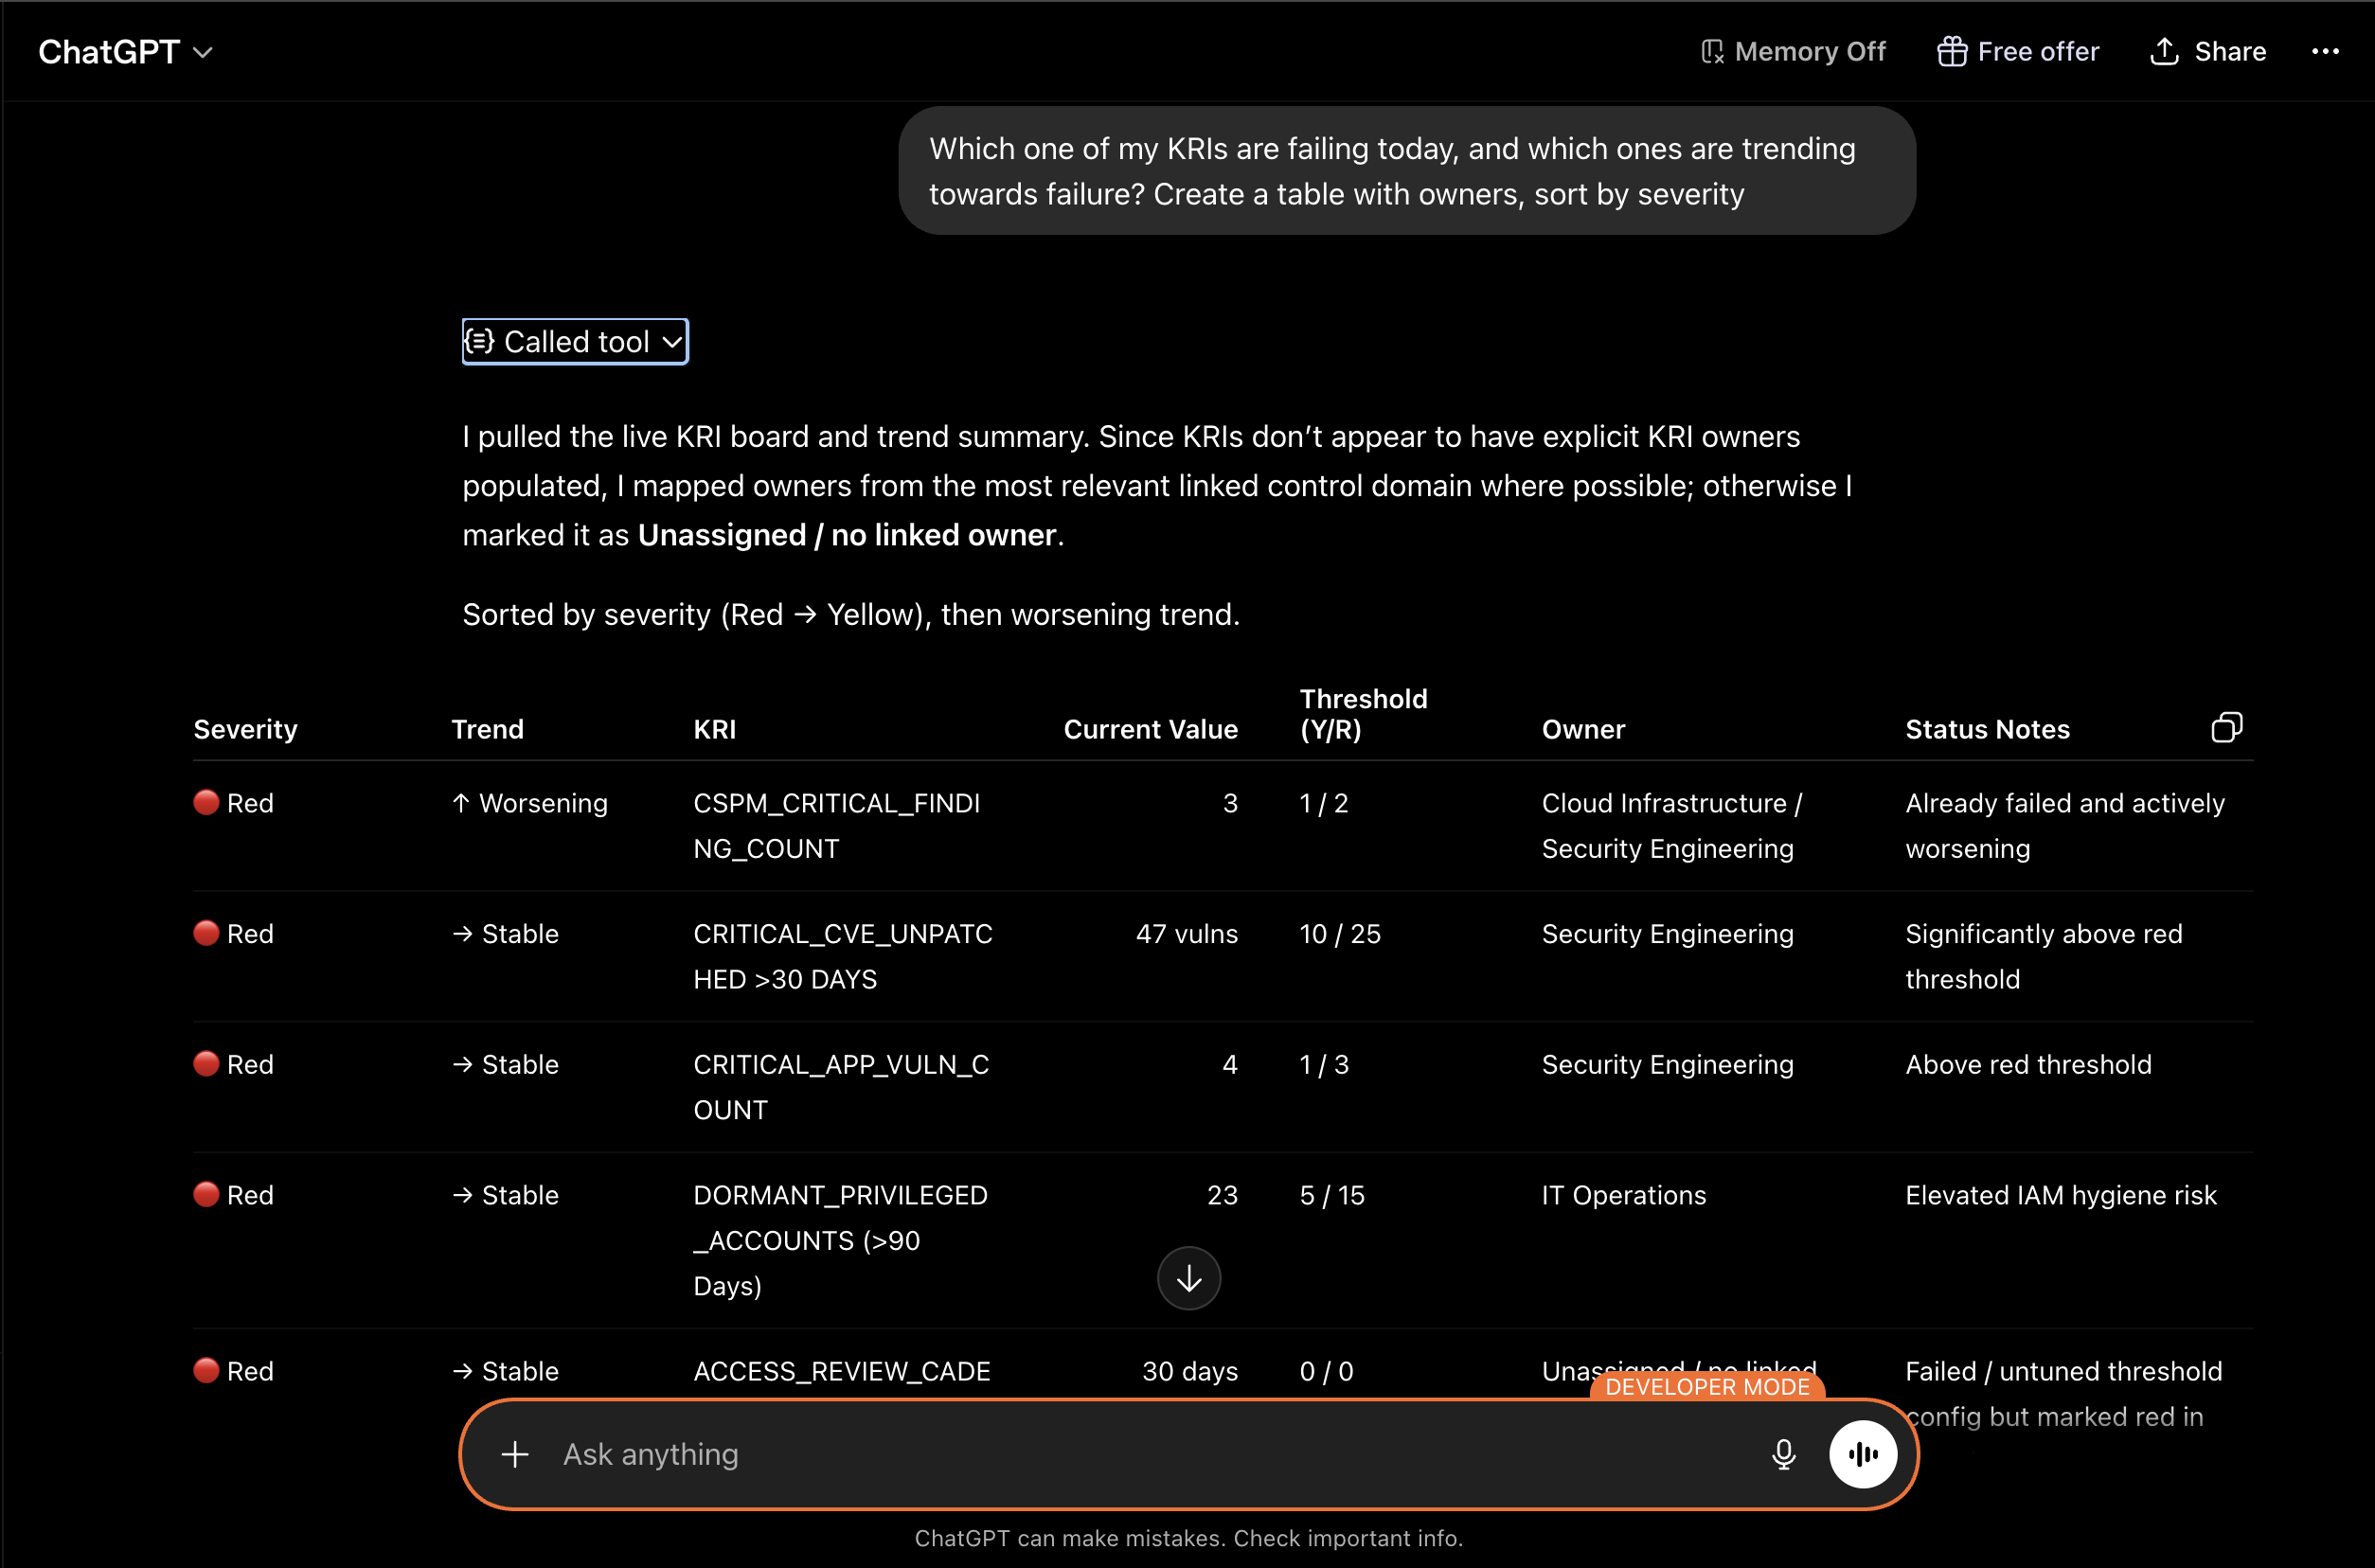
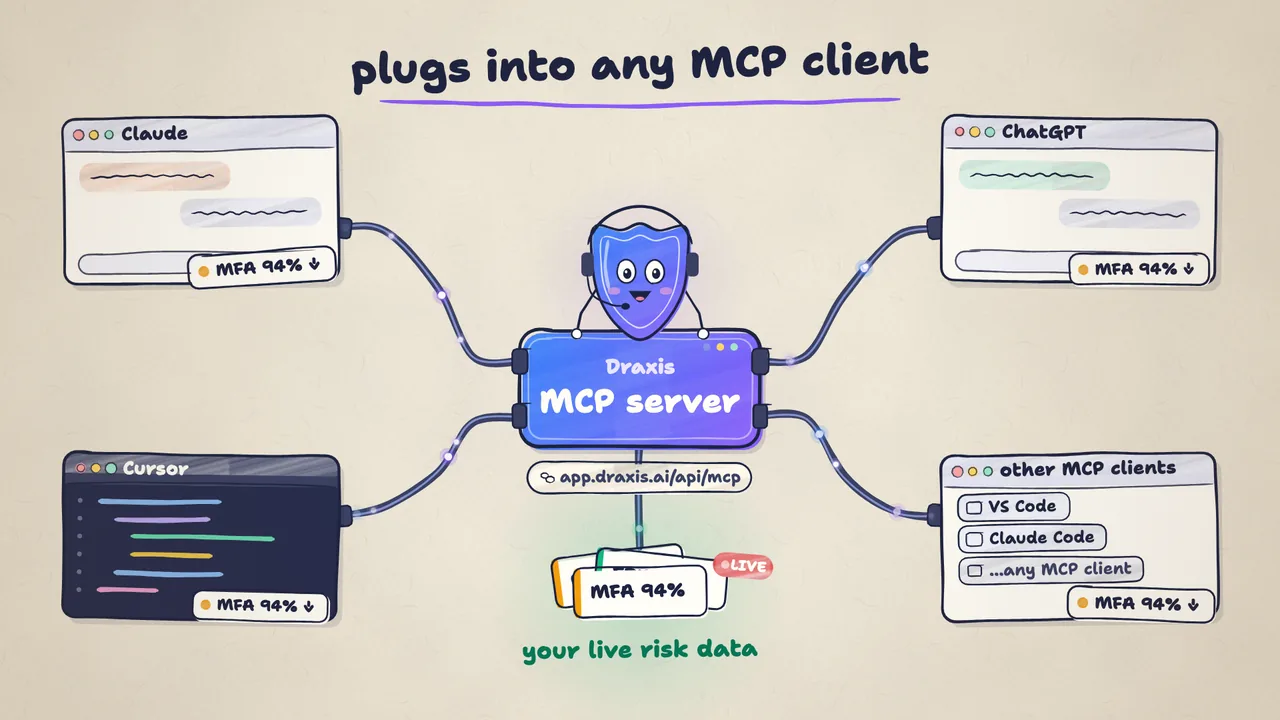
Any LLM client queries Draxis directly. Ask your live risk posture anything from Claude, ChatGPT, or any MCP-compatible AI client, and get an answer drawn from your real environment.
Ask your live control signals anything from your LLM client of choice.
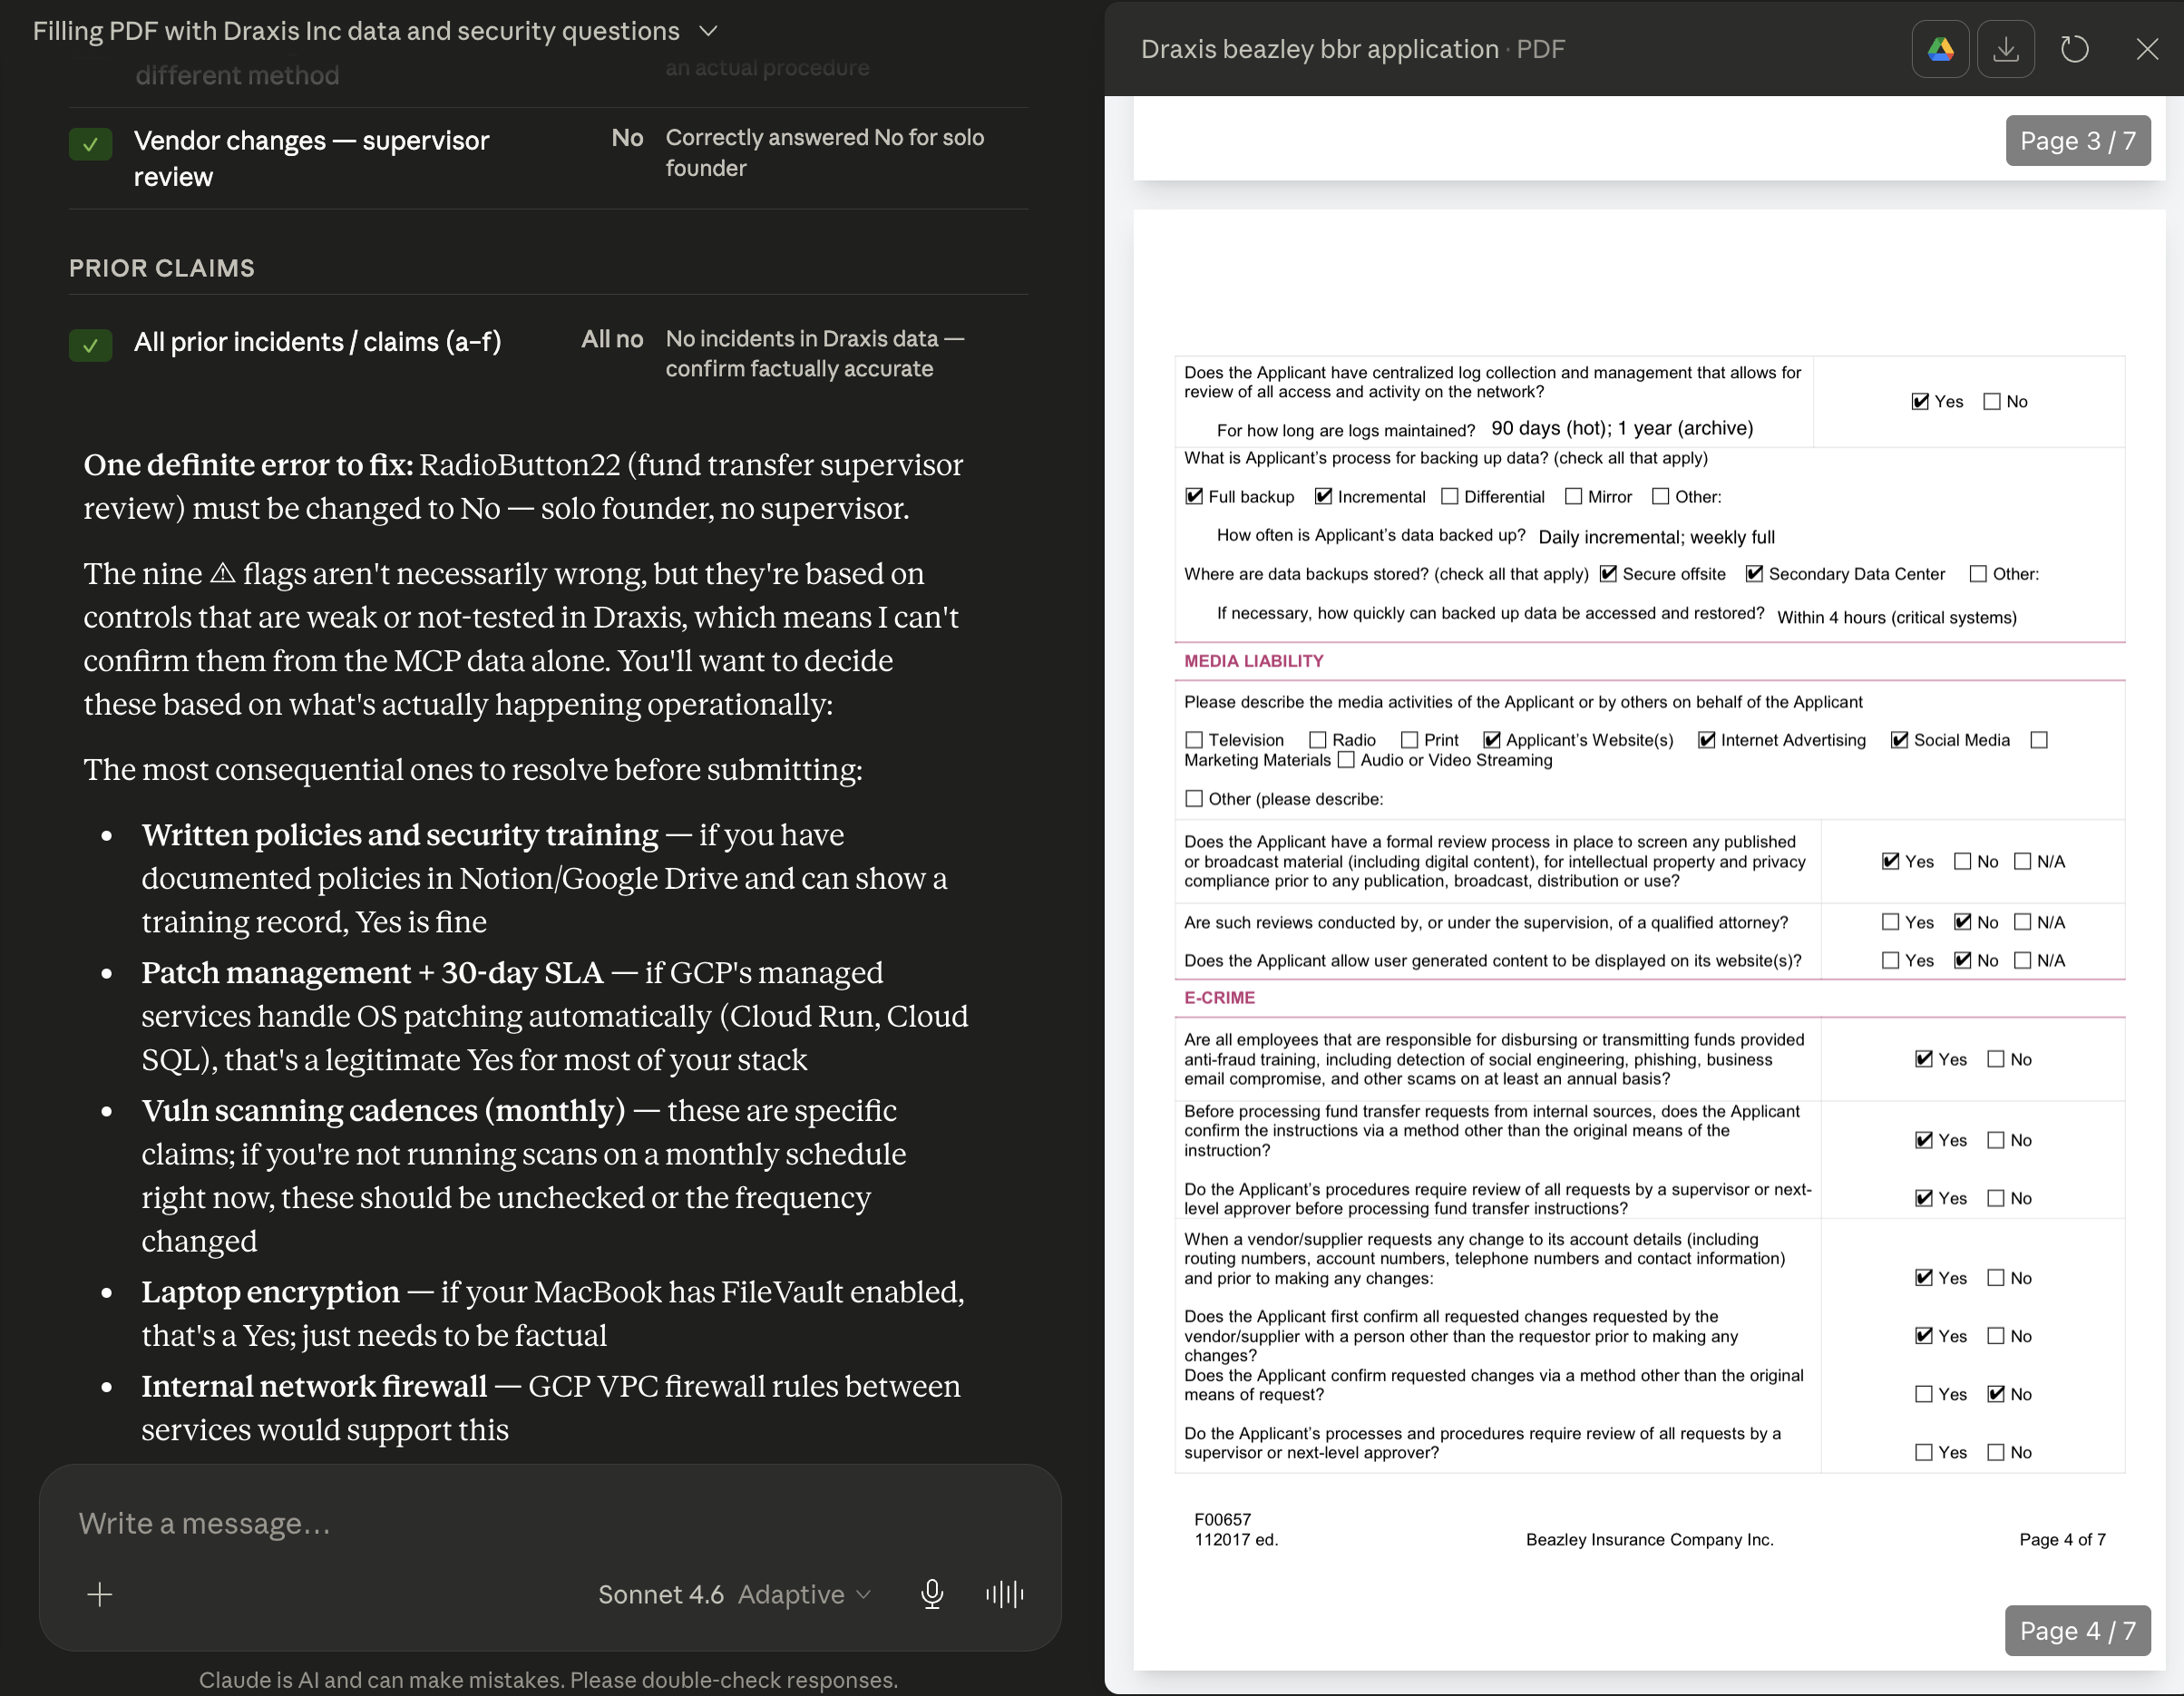
Fill out cyber insurance applications using live Draxis posture data.
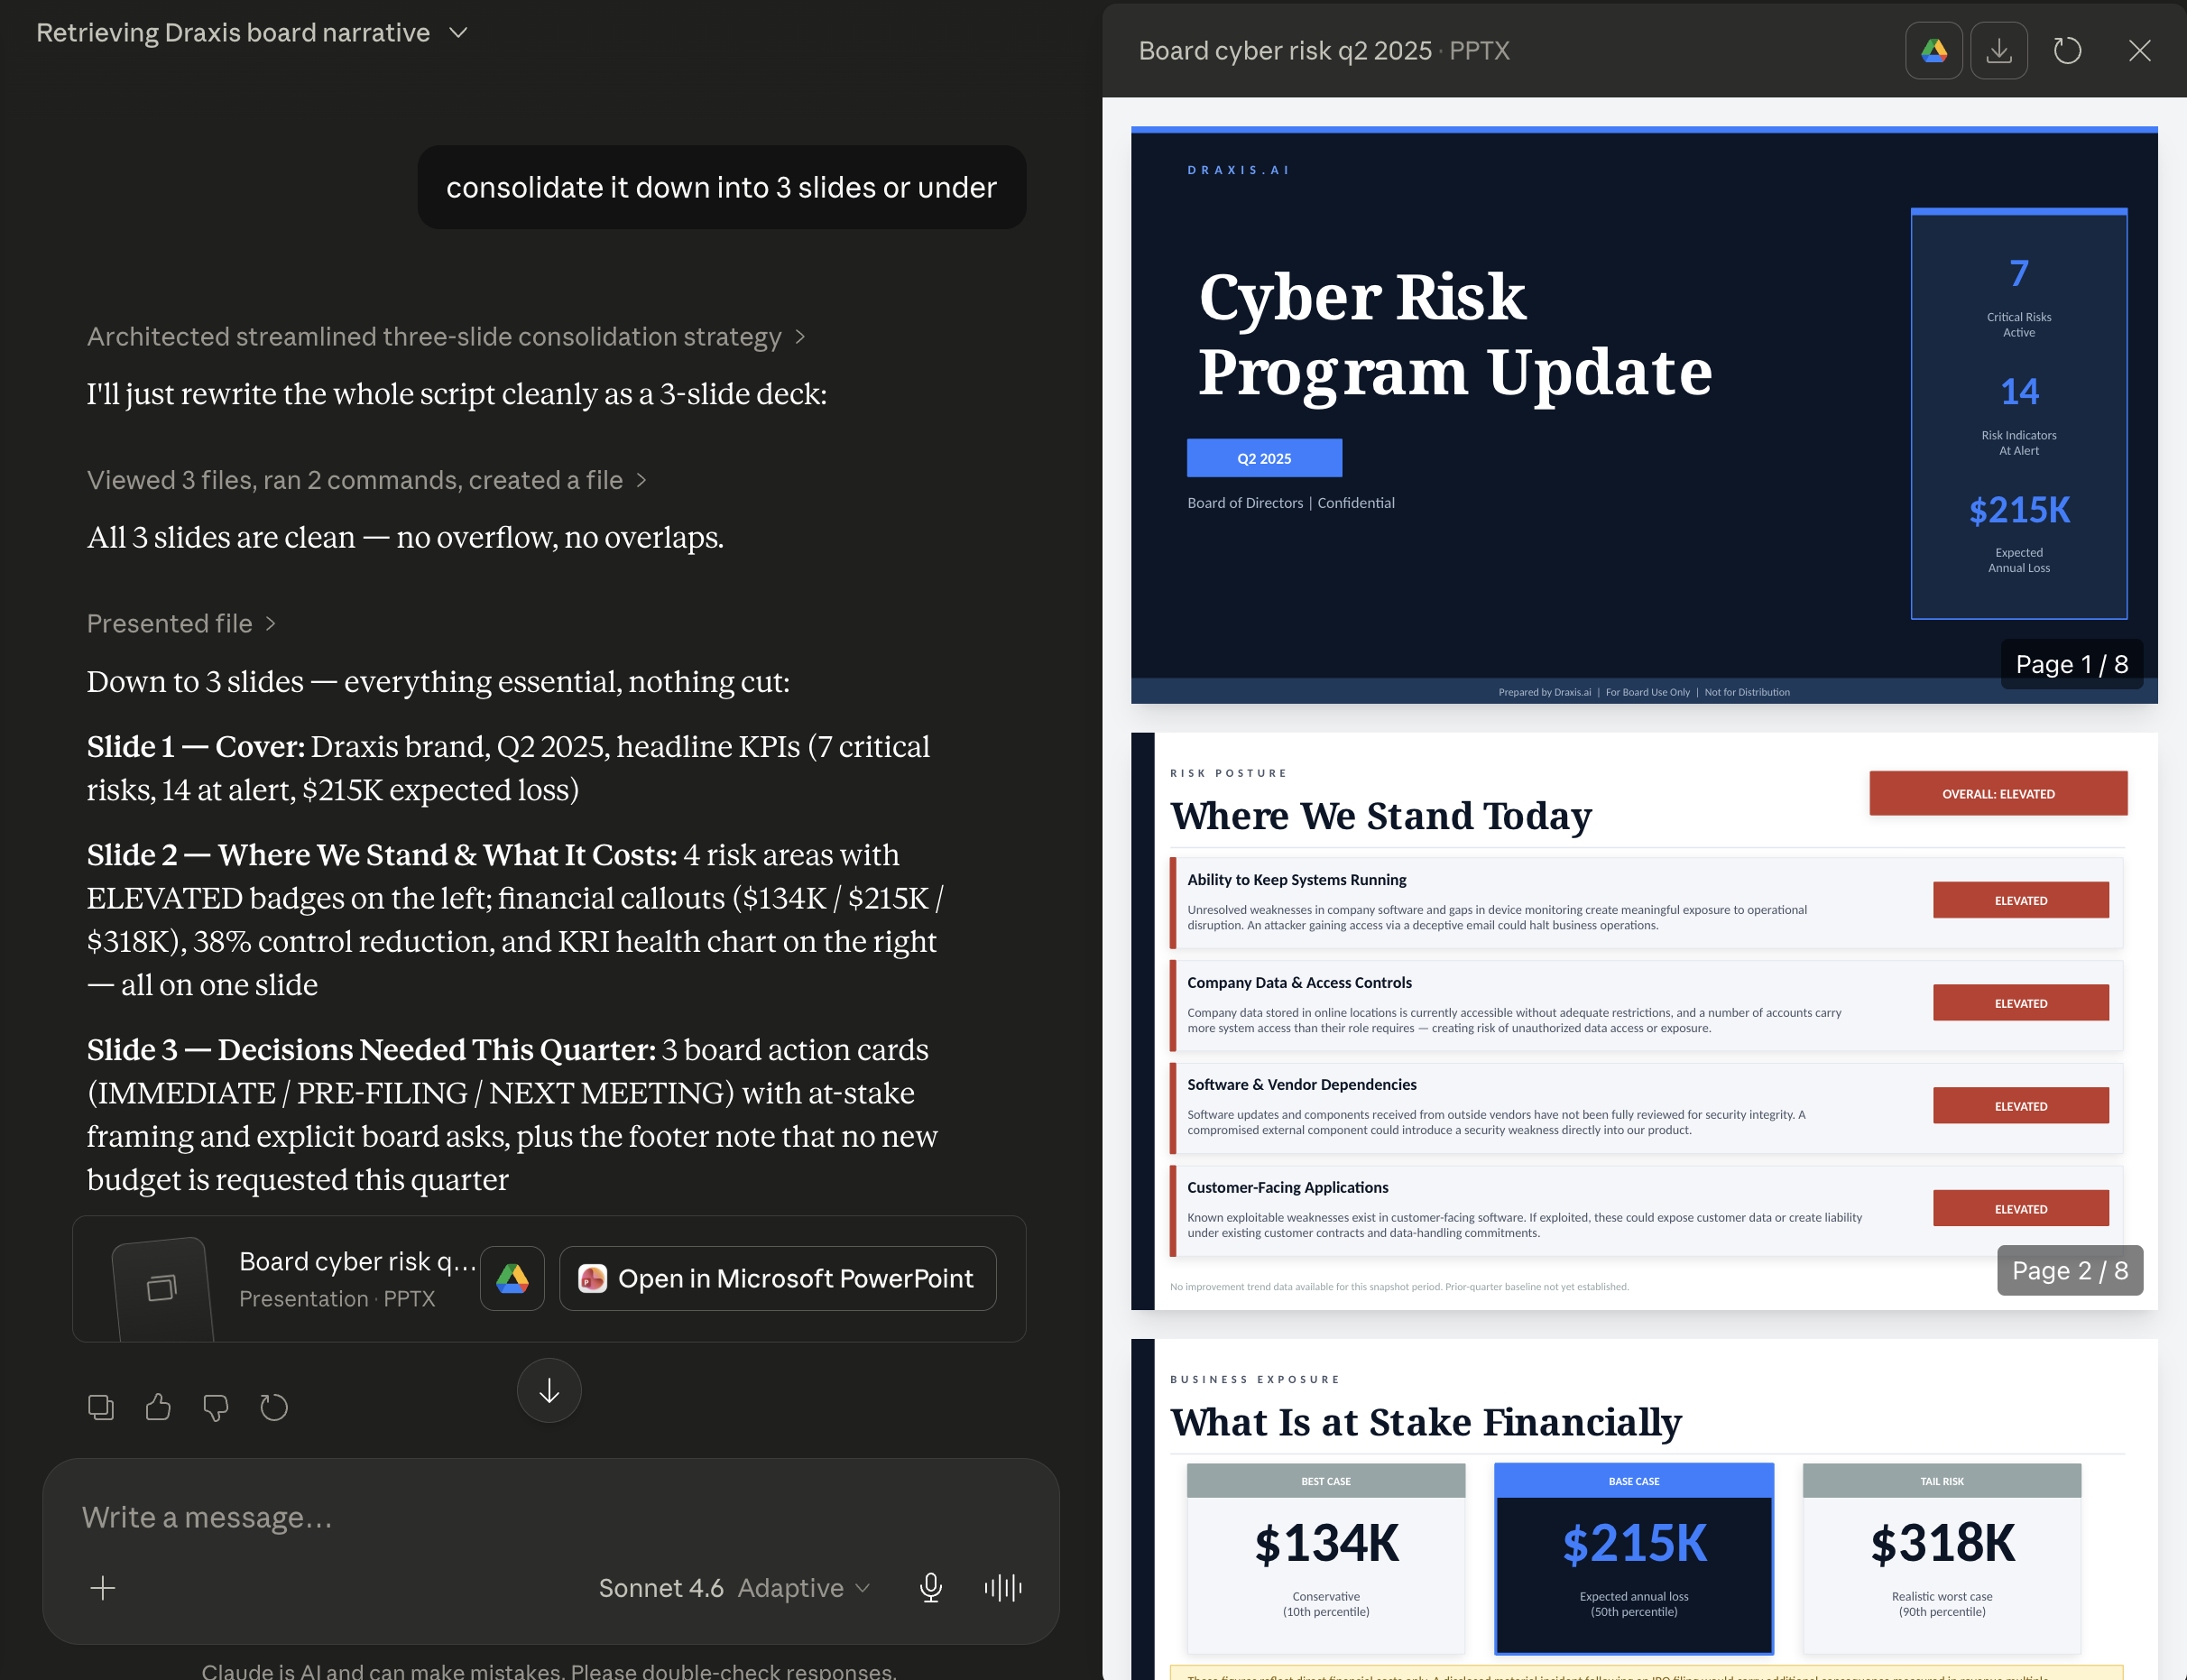
Generate board-deck narratives straight from PowerPoint, drawn from your live posture.
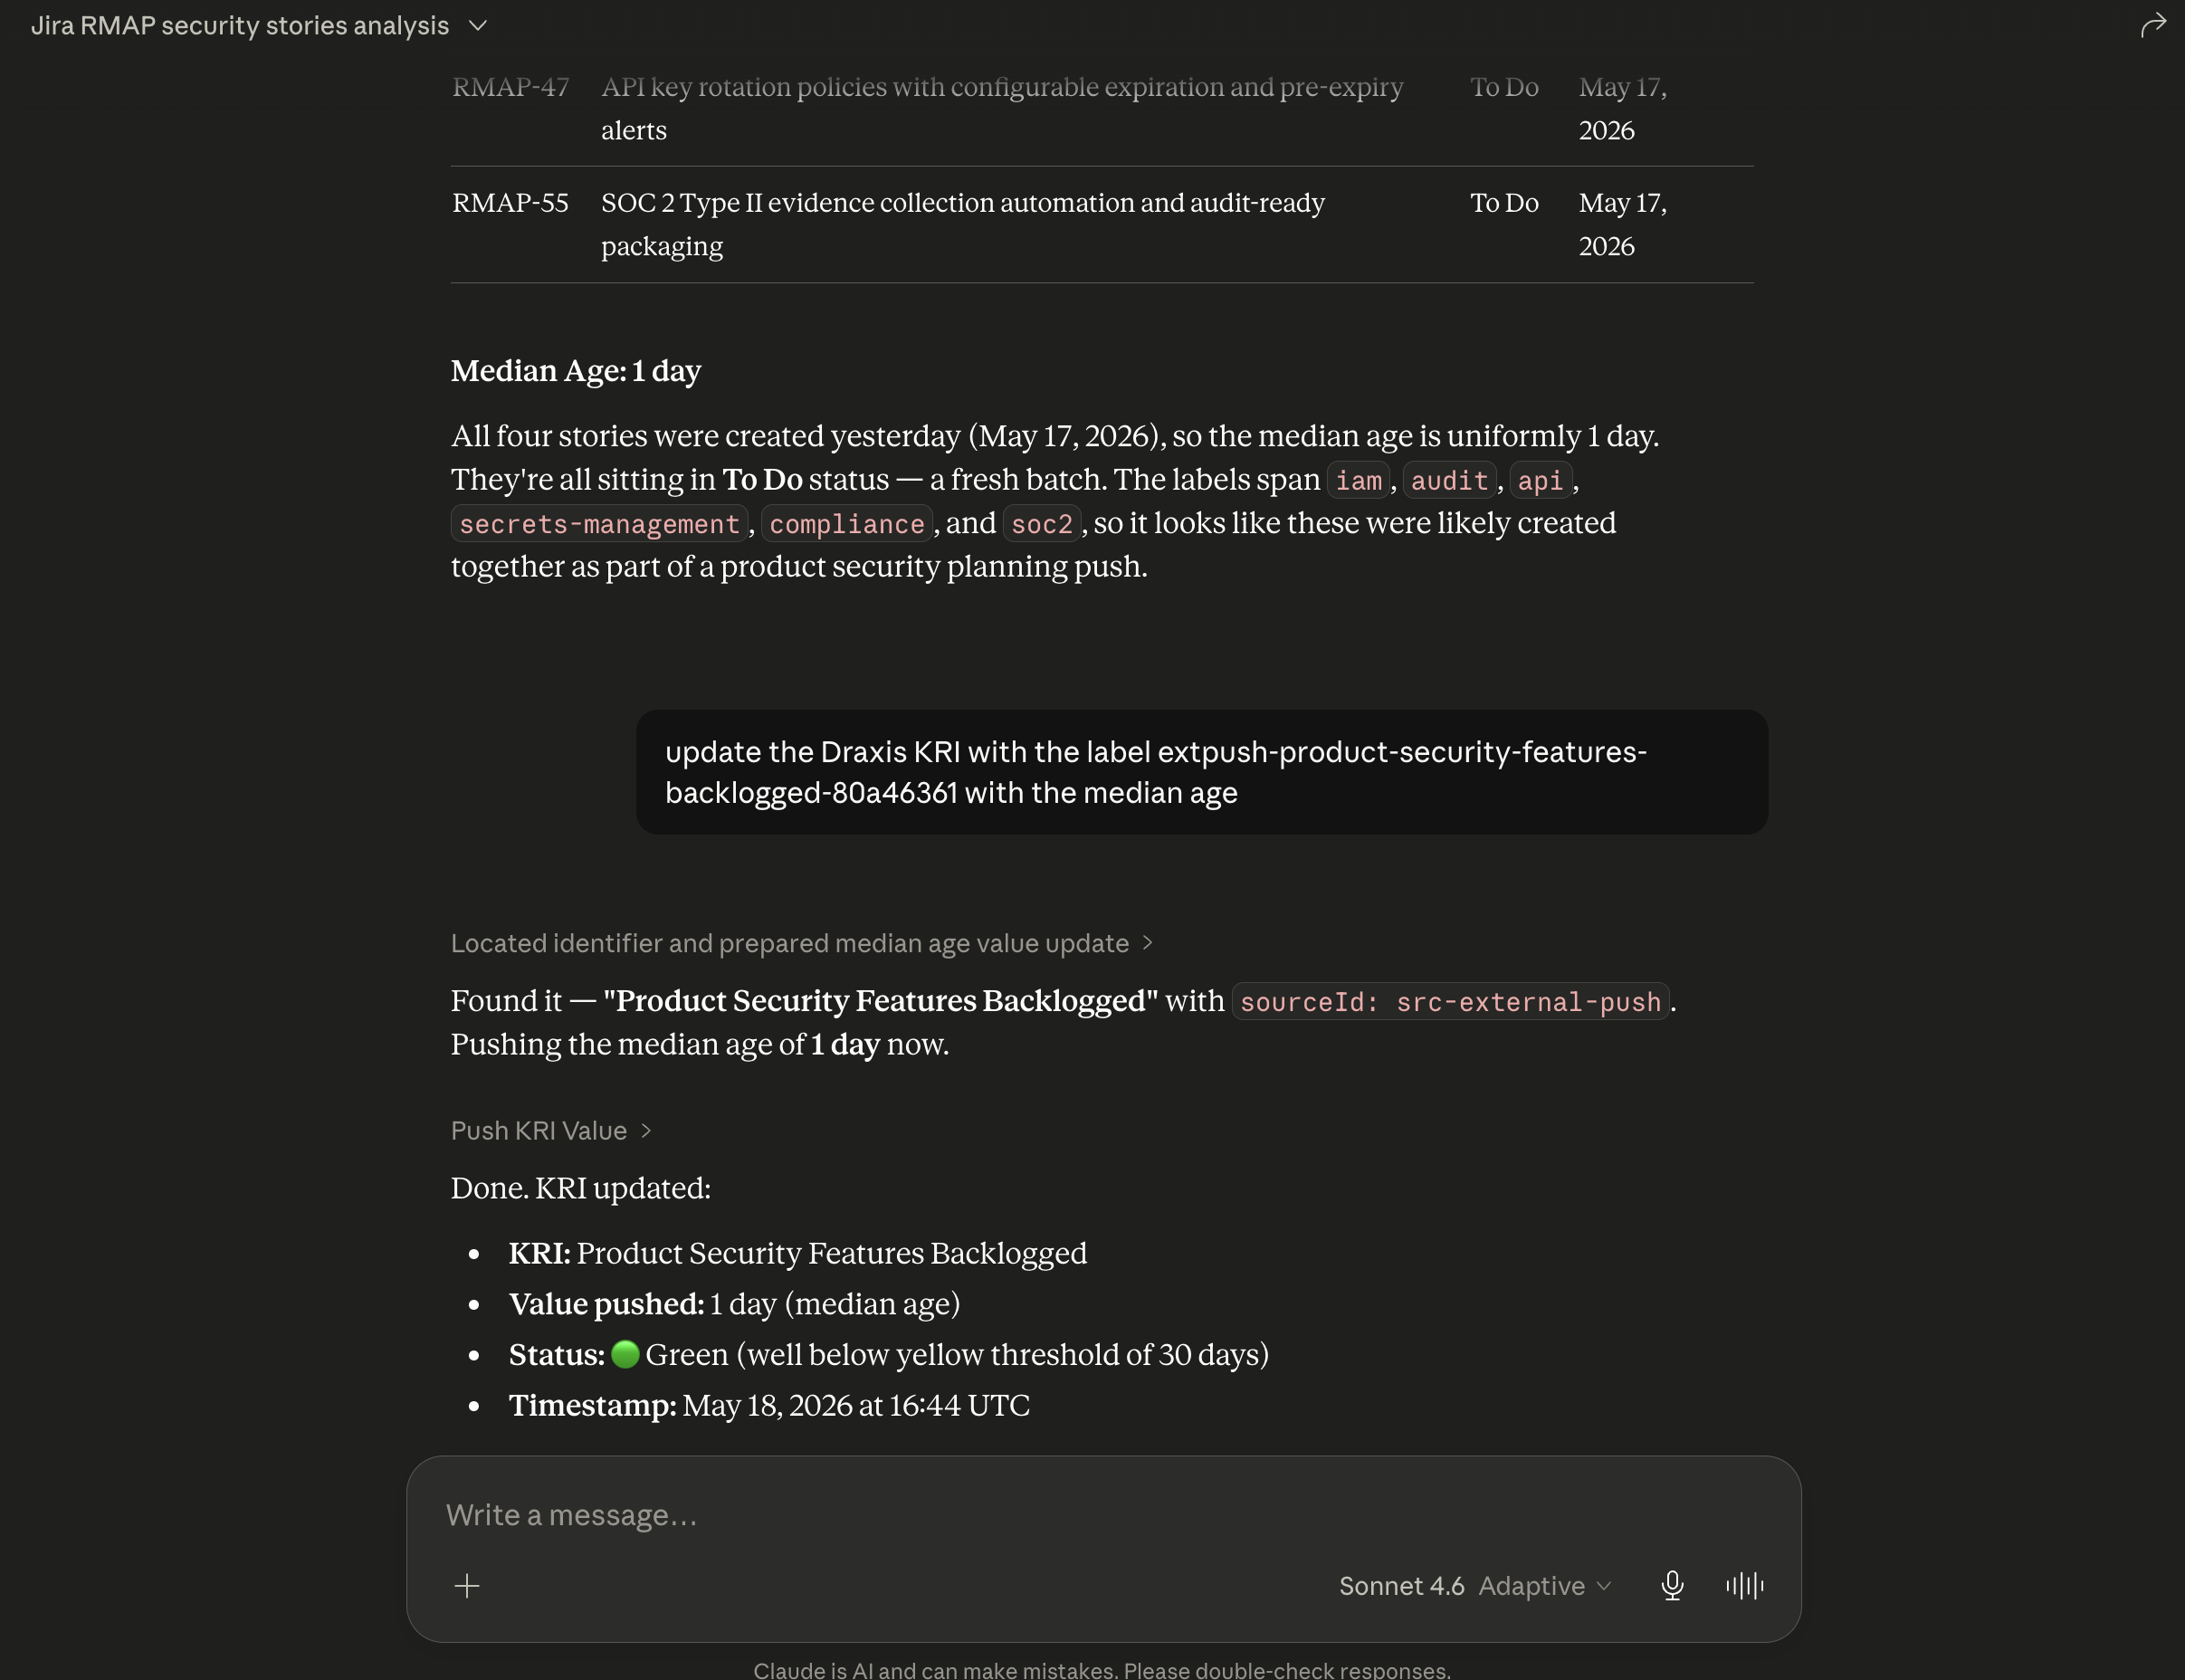
Connect any MCP-enabled AI agent or workflow to your security intelligence.
Compounding learning
Worth more in month 12 than in month 1.
Every conversation, decision, and signal becomes part of your tenant’s memory. And the platform itself gets sharper as more organizations join.
Your AI starts to sound like it actually works there.
Every Drop Zone extraction, Advisor answer, panel deliberation, and risk decision is captured as institutional memory, with provenance. Future answers get framed against your baseline, your conventions, your prior reasoning. Not an industry average. Not a generic prompt.
A Draxis instance that’s been live for a year is materially smarter about your business than any consultant can be on day one.
Enterprise-Grade Security
Built for trust
from day one
- ✓ JWT RS256 with auto-rotating refresh tokens
- ✓ TOTP MFA with encrypted secrets & backup codes
- ✓ Four-tier RBAC (Super Admin → Viewer)
- ✓ Per-tenant database isolation (physical separation)
- ✓ Immutable audit logging for all security events
- ✓ HttpOnly cookies with CSRF protection
- ✓ Rate limiting on authentication endpoints
- ✓ SSO-ready architecture (SAML 2.0 / OIDC)
- ✓ Secure SDLC with AI-powered code scanning & blocking
- ✓ Vulnerability Disclosure Policy (RFC 9116)
Support & Documentation
Everything you need to connect Draxis to your stack: integration guides, API reference, architecture overviews, and direct access to the team.
Multi-Tenant SaaS Architecture
Database-per-tenant model ensures complete data isolation. Central registry manages tenant lifecycle. Stateless JWT enables horizontal scaling.
Your data, your control.
Four ways to connect Draxis to your stack, from full read-only integration to push-only with zero tool access. You pick the model that fits your risk tolerance.
See how Draxis handles your data →FAQ
Questions security buyers ask
What is Draxis.ai?
Is Draxis a GRC platform?
How is Draxis different from external security ratings?
What does the AI do?
Does Draxis work without a CISO?
Who is Draxis built for?
How long does it take to get value from Draxis?
Do I need to replace my existing security tools?
What is the MCP integration?
Is Draxis an insurance platform?
See it on your own stack.
Connect a few read-only APIs and you have a live, quantified picture of your exposure within 48 hours.